Like a Luna Moth to a Flame
Alfred Kubin, Die Einbeere (One Berry), c. 1900 (digitally altered)
Contents
- Executive Summary
- Source Materials
- Data Provenance
- Introduction
- ‘The Luna Moth Files’
- Attribution: Luna Moth Lineage
- Operator Analysis
- Chat Room Directory
- Assessment
- Room-by-Room Analysis
- Extortion Targets: Law and Accounting Firms
- Extortion Methodology
- Technical Infrastructure
- On-Chain Blockchain Analysis
- Warning Signs for Target Organizations
- Detection and Hunting Guidance
- MITRE ATT&CK Mapping
- Appendix A: Consolidated IOC Registry
Executive Summary
This report analyzes four leaked operational files from the established Russian-speaking extortion group “Silent Ransom Group” (aka SRG or Luna Moth). These files are internal documents from the SRG group which were leaked on a Tor site and proliferated widely via X (formerly Twitter) on 2026-10-03.
The leaked chat export (taken from two self-hosted Rocket.Chat servers run by the group) holds 5,692 messages across 36 rooms. These messages were sent by seven human operators between August 2025 and September 2026.
The operation combines six activity lines:
- Law firm data extortion (primary revenue)
- HUMINT targeting of [REDACTED MILITARY] nuclear submarine personnel
- Vishing (voice phishing) for initial access
- Physical building infiltration with field agents
- Kidnapping and armed enforcement
- Fake employee placement at defense contractors
Classification: Hybrid criminal-espionage operation | Language: Russian and English | Period: Aug 2025 to Sep 2026 | Messages: 5,692 across 36 rooms | Operators: 7 humans + 1 bot | Confidence: High
Key Findings
- SRG logged 27 victims as paid, $206.95M in total (Probable). The group's own accounting records at least $43.95M received (Confirmed).
- The attacks used no malware. Vishing calls opened AnyDesk sessions, and operators copied the data out by hand (Confirmed).
- The group planned kidnapping, armed enforcement, honey traps, insider placement and naval targeting. None of it is confirmed as carried out (Possible).
- Money from the largest Bitcoin address named in the chat passes through a WhiteMist exchange wallet that earlier reporting links to Akira and LockBit payments (Possible).
- SRG is a Luna Moth lineage operation, and the core operators work on Moscow time, UTC+3 (Probable).
Source Materials
| File | Type | Size | SHA256 |
|---|---|---|---|
chat_export_full.json.gz | gzip JSON | 214 KB (1.2 MB raw) | 41900fbcc8a172629c695bba46ad15b7981610ea52d3a61ab4061fd6d860e809 |
target_list_naval_bases.xlsx | Excel 2007+, no macros | 11.5 KB | 4bee44ec615b61d6f1acdb4b3d92497f9f200757f4b6653068dce23a9f100d4f |
fake_employee_resume.pdf | PDF 1.4, 1 page, clean | 53.7 KB | a6a580e4aff45d4812123eb18ec7bd1c53f44b3369e3b430d7b72f4cdb30778e |
vishing_call_script.txt | UTF-8 text | 8.6 KB | d2f3a78a814ca628ca54358cc35808b8bd032bcde81f72134addc05e5546285e |
Data Provenance
This report draws on the four files leaked from the SRG Tor site, (announced on X/Twitter on 2026-10-03, see Introduction). Three figure slides in the Attack Flow, Victim Confidence Model, and Assessment sections have additional details from Crystal Intelligence reporting. Each slide caption names those details.
Authenticity Assessment
Ransom-ISAC has assessed that the SRG leaks are most likely authentic for the following reasons:
- The messages are internally consistent. Timestamps, usernames, room references, and cross-room citations agree with one another.
- The operational detail is both mundane and specific. Payroll disputes, wallet addresses, inside jokes and server credentials match the pattern of previously confirmed internal chat links.
- The financial data checks out on-chain. Wallet amounts in the chat match the Bitcoin blockchain to the satoshi. See the On-Chain Blockchain Analysis section.
- The victim firms, domains, and infrastructure mentioned are real and match screenshots included in the archive.
Research Limitations
The research done on these leaks has exposed a number of limitations that affect analysis:
- The files were published on the Tor site and announced/claimed on X on 2026-10-03 by user “Donald Hamei” (@DonaldHame0q), but the identity of the leakers has not been confirmed.
- The export has no cryptographic signature, meaning single messages could in theory be altered or inserted.
- The chats contain only a partial window into SRG’s internal chats ranging from August 2025 to September 2026. The export may also omit rooms or messages.
- Figures that operators state about themselves as fact have to be taken at face value unless independently verified.
Confidence Grading
| Grade | Meaning | Example in this report |
|---|---|---|
| Confirmed | Direct evidence in the data: an on-chain match, an exfiltrated file path, or a named victim room | The group's internal accounting recording $43.95M received. The REDACTED FIRM 3 and REDACTED FIRM 4 data theft. |
| Probable | Strong but indirect evidence: consistent operator statements plus corroboration | The operators sit in UTC+3. The group is a Luna Moth lineage operation. |
| Possible | A single source or an uncorroborated plan | The REDACTED CYBERWARFARE COMPANY and REDACTED CYBERWARFARE COMPANY placement (one chat line). The kidnapping plans (detailed, no confirmed execution). |
| Claimed | An operator statement with no corroboration | The $500M season goal. The 800 BTC cash-out boast. |
Introduction
On October 3, 2026, user @DonaldHame0q posted to X (formerly Twitter) claiming that they had obtained extensive chat logs from Silent Ransom Group detailing months of operational planning.
The post links an onion site address:
h7v7qkdil4lkm3ocwmcudzfmx7xmihtw53n3yk7b2cjtqu3zc4xqo7qd[.]onion
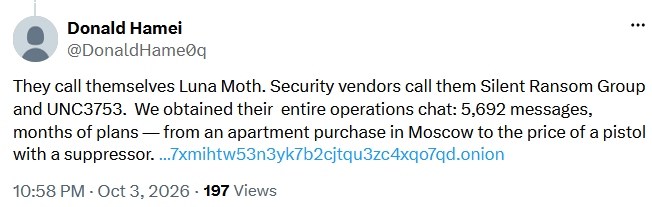
From X (formerly Twitter)
The linked server is hosted with nginx/1.18.0 (Ubuntu) and was live on October 3, 2026.
‘The Luna Moth Files’
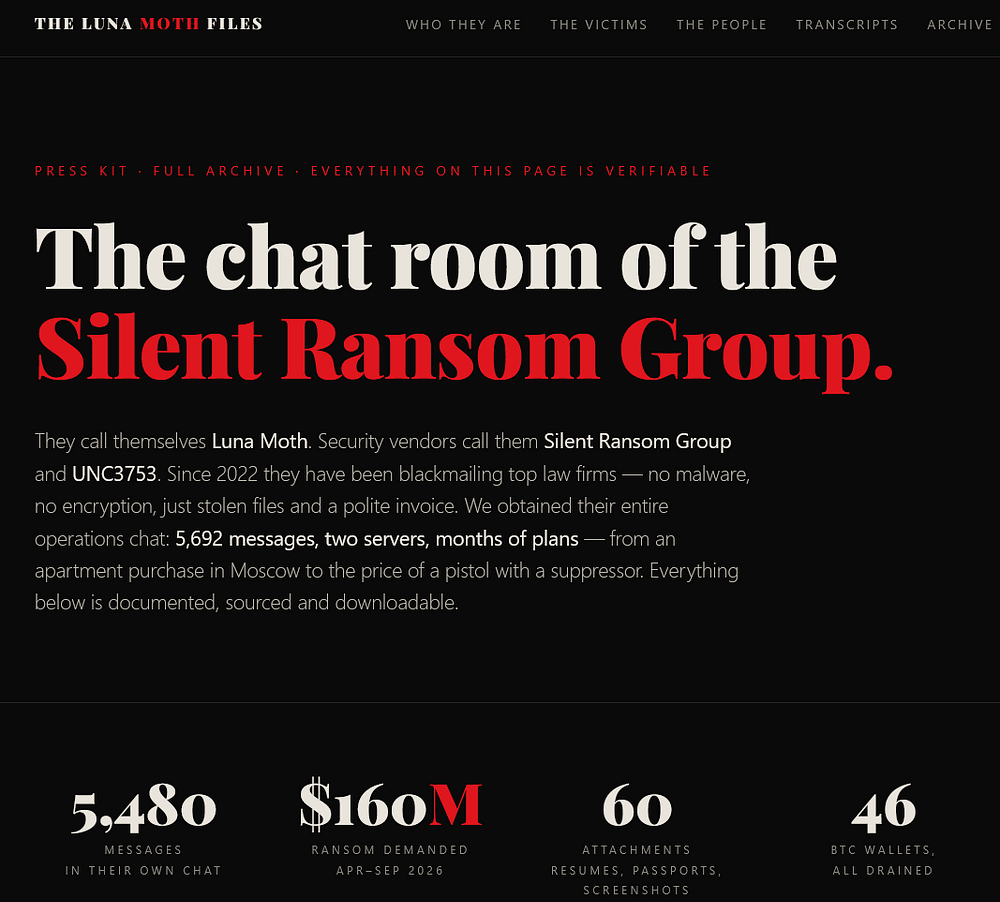
Screenshot of the SRG leak site, served from nginx/1.18.0 (Ubuntu) and live on 2026-10-03.
From the webpage design, it appears that the creator used Claude to create the page using the uploaded leaks.
The webpage is divided into five sections:
WHO THEY ARE: Step-by-step threat actor handbook for operations.
THE VICTIMS: List of law firms extorted, the amount they were extorted for, and payment status.
THE PEOPLE: Short profiles on actors included in the archive, most notably “Henry” and “Adrian”.
TRANSCRIPTS: Direct quotes pulled from the chat export showing operational details and communication styles of the actors.
ARCHIVE: Download links for the leaks including a chat export, fake employee resume template, a call script for vishing, several images and screenshots of communications, and a list of LGBTQ+ bars proximate to [REDACTED] naval bases for finding blackmail targets.
‘WHO THEY ARE’/Operational Methodology
The ‘WHO THEY ARE’ section defines the various steps involved in the operation. Another indication that the website was created using an LLM with few edits is that this section only relays operational methodology as opposed to giving contextual information about the actors, making the section title mostly unrelated to its content.
As noted in the breakdown, SRG frame themselves using sales terminology rather than self-identifying as a ransomware group. Their operational methodology is laid out for actors using specific, straightforward instructions similar to an employee handbook.
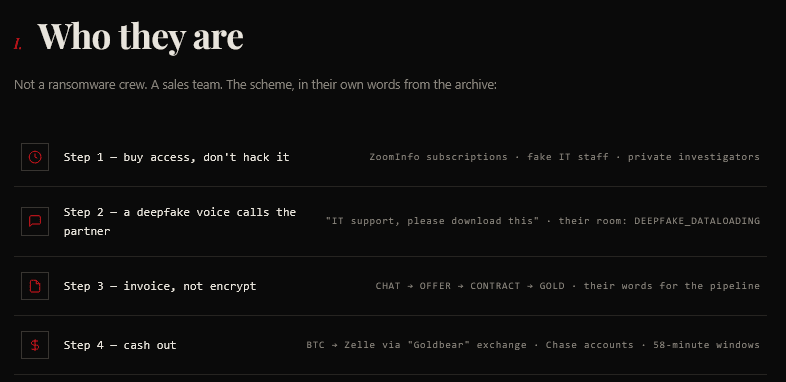
The leak site's “Who They Are” section, outlining the ransomware operation.
‘THE VICTIMS’
This section refers to a list of victims (specifically US law firms) who have allegedly paid the group’s ransom demands.
“GOLD” refers to victims who have paid ransom demands.
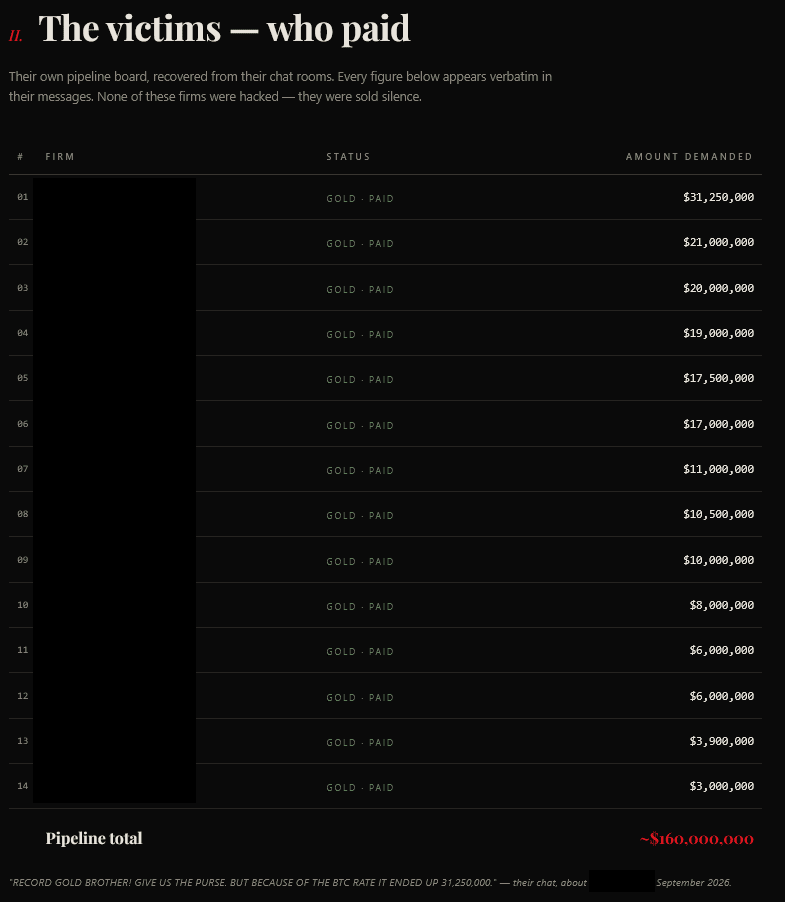
The leak site's “The Victims” section, listing firms recorded as having paid.
‘THE PEOPLE’
This section involves the key persons involved in the operation.
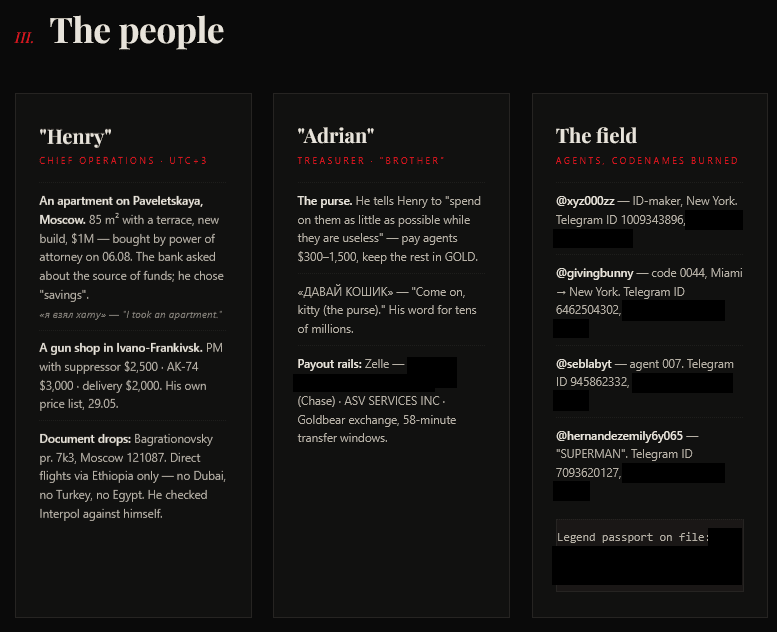
The leak site's “The People” section, naming Henry and Adrian with doxxed detail.
Two people, Henry and Adrian, pilot the project with their doxxed details.
‘IN THEIR OWN WORDS’
This section presents the chat conversation between the team members and affiliates from the Rocket Chat Server.
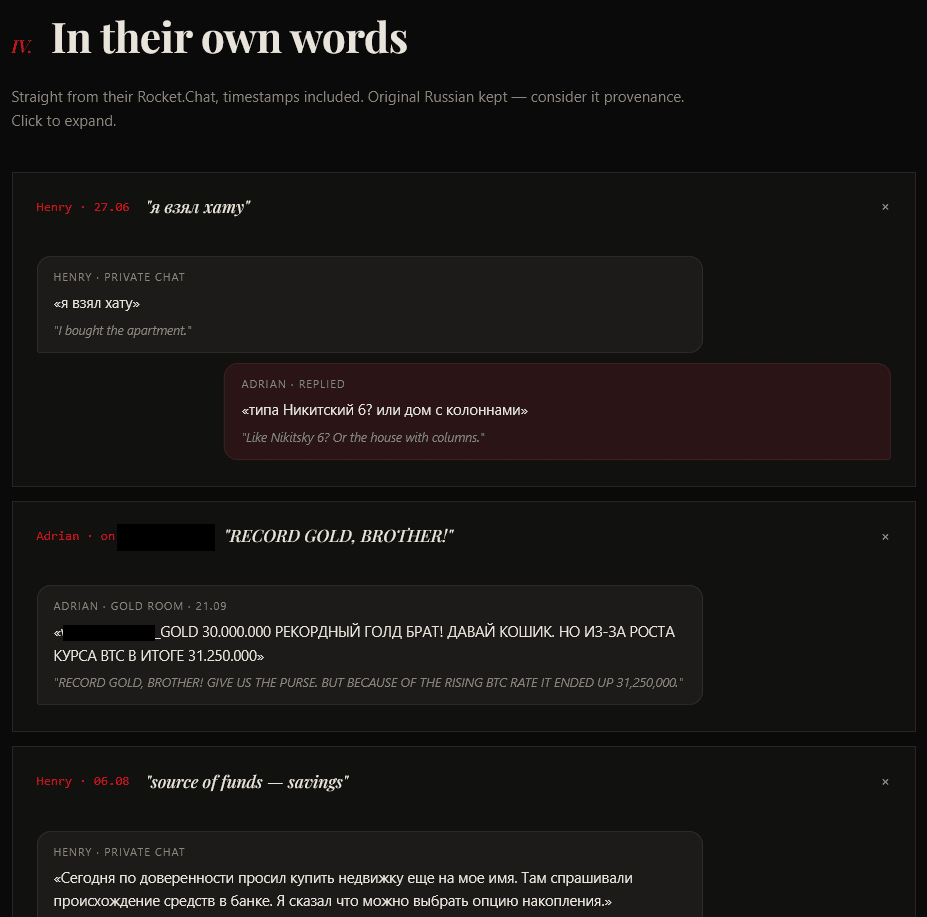
The leak site's “In Their Own Words” section, excerpting the Rocket.Chat logs.
‘THE ARCHIVE’
This section lists the hacked data to be downloaded from the onion service.
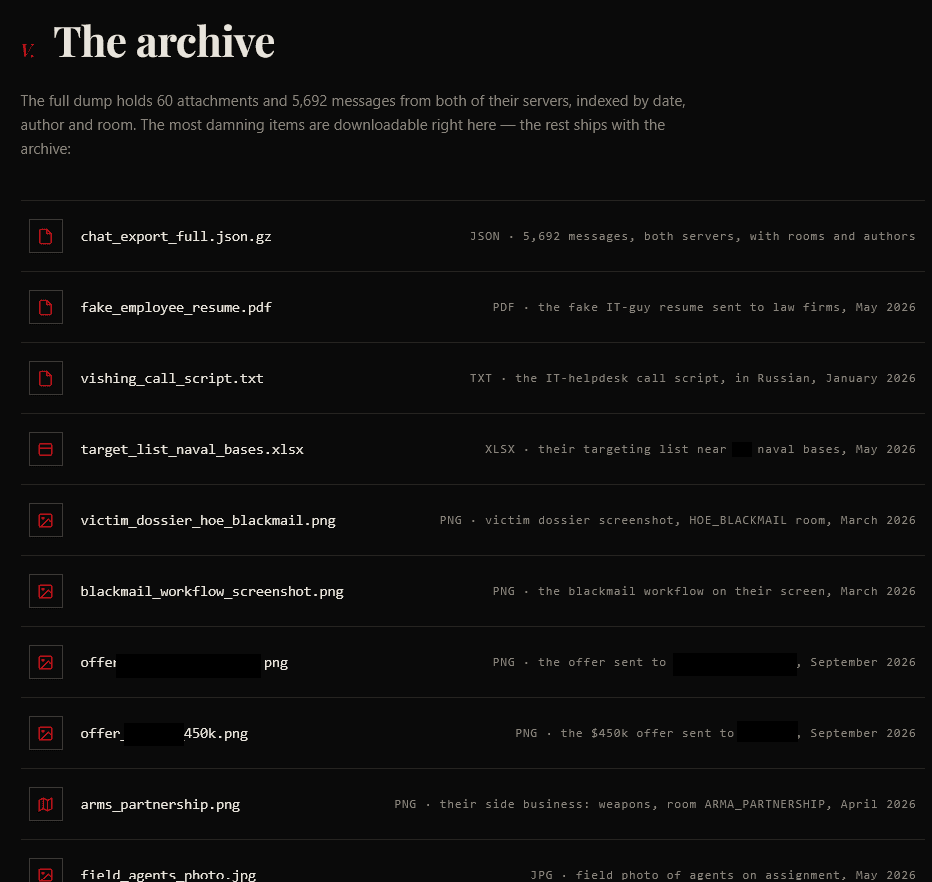
The leak site's “The Archive” section, which lists the stolen data for download.
Attribution: Luna Moth Lineage
Lineage Assessment
Ransom-ISAC has assessed with Probable confidence that the operation falls within the Luna Moth/Silent Ransom Group/Sleepless Threat lineage. This lineage of threat groups is strongly associated with Callback Phishing operations.
For defensive purposes, treat intelligence derived from these leaks as part of active Luna Moth / SRG operations that have escalated beyond data extortion with proposed military and physical infiltration operations.
Limitations
Public SRG and Luna Moth reporting describes a data-theft extortion group, while this extract adds military HUMINT, kidnapping, armed enforcement, and defense contractor infiltration. These are a major escalation beyond documented SRG activity, suggesting the group may be an SRG splinter. Confirmed identity overlap with named SRG operators is not present in the leaked data.
Evidence
| # | Evidence | Significance | Weight |
|---|---|---|---|
| 1 | Self-identification as "Silent Ransom Group" in databreaches.net coverage | The group named itself Silent Ransom Group in press coverage on databreaches.net. This is self-attribution, not a third-party label. | High |
| 2 | Callback phishing (vishing) as the primary initial access method | This is the defining Luna Moth / SRG technique. The full vishing script was recovered in the data. | High |
| 3 | Law firm data extortion as core revenue | SRG is known publicly for stealing data from US law firms, not for encryption. The victim set matches. | High |
| 4 | No encryption locker in the data | Consistent with SRG / Luna Moth, which steals and extorts rather than encrypts files. | Moderate |
| 5 | Russian-speaking operators on a UTC+3 clock | Consistent with the known SRG operator base. See the Operator Timezone section. | Moderate |
Operator Analysis
Organizational & Social Hierarchy
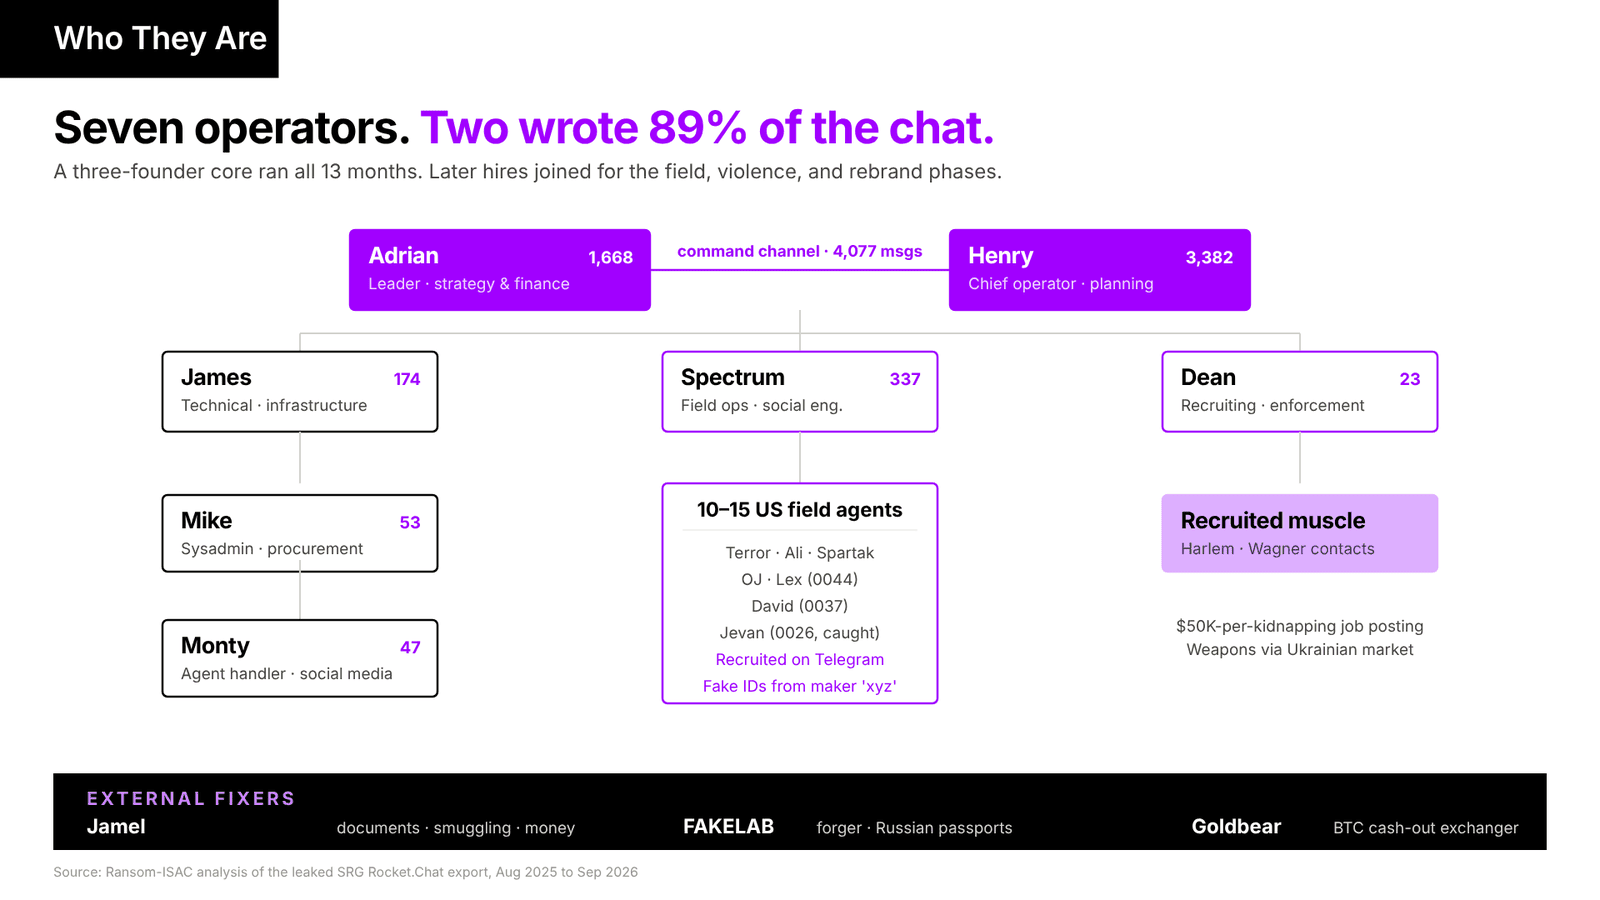
Infographic showing the chat operator hierarchy and message volume. A three-founder core (Adrian, Henry, James) ran all 13 months. Spectrum, Dean, Mike, and Monty joined for the field, violence, and rebrand phases. External fixers sit outside the chat.
The network runs as two handlers under one coordinator. Henry runs the external fixers. Spectrum runs the US field agents. Adrian coordinates both.
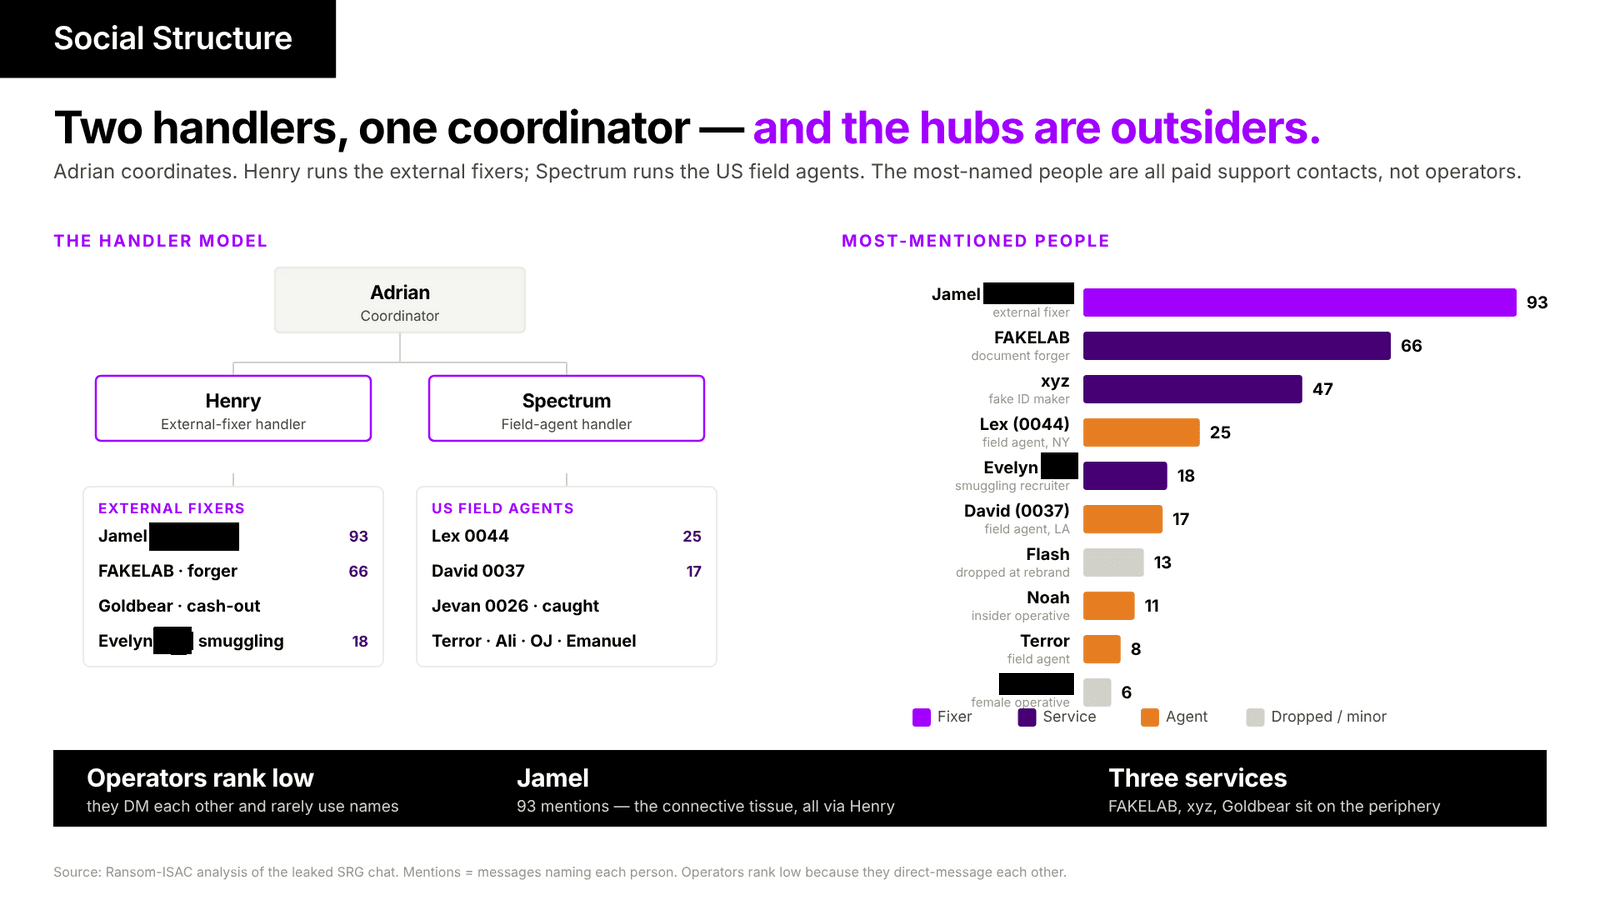
The social structure runs as two handlers under one coordinator. Henry is over the external fixers. Spectrum is over the US field agents. By mention count the hubs are all paid outside contacts. The operators rank low because they direct-message each other.
Threat Actors
Adrian (Leader)
Number of messages: 1,668
Boss of the operation. Sets targets, approves plans, and controls finances. Russian-speaking. Adrian makes all major decisions: extortion amounts, which companies to infiltrate, and military targeting priorities. Adrian selected REDACTED CYBERWARFARE COMPANY and REDACTED CYBERWARFARE COMPANY as fake employee targets. Adrian started the naval base espionage plan.
Henry (Chief Operator)
Number of messages: 3,382
The most active member. Reports to Adrian. Henry replaced a previous operator called "Sam." He handles operational planning for vishing campaigns, kidnapping logistics, military base research, and defense contractor OSINT. Chat describes him as "наш главный опер по майн и супертрг" (our main operator for main and super-targeting). Henry likely lives in Europe or the CIS. He expressed a desire to relocate permanently to Russia.
Spectrum (Field Operations)
Number of messages: 337
US-based field operative. Runs physical operations: building infiltration, agent coordination, and card skimmer deployment. Spectrum proposed pizza delivery cover and spy glasses. He manages 10 to 15 field agents via Telegram. English-speaking.
James (Technical Operator)
Number of messages: 174
IT infrastructure manager. Builds fake domains, manages SSH/RDP servers, and buys corporate network access from underground sellers. James led the SRG-to-ST rebrand and OPSEC overhaul. Bilingual. Built a custom tool called "SpyCo."
Mike (Sysadmin)
Number of messages: 53
Procures infrastructure: Google Drive accounts, SSH shells, and Zoom accounts. Mike built the Sleepless Threat leak site. He provides server credentials and staging resources.
Monty (Agent Handler)
Number of messages: 47
Manages vishing callers ("agents"). Handles the stolen X/Twitter account the group uses for Sleepless Threat PR.
New Telegram handle: woodythedoo.
Dean (Recruiting / Enforcement)
Number of messages: 23 messages
Recruits agents and muscle. Dean posted a $50K-per-kidnapping job listing. He contacted a pimp in NY for the prostitution scheme. Dean replaced a previous member called "Christi/Kristina."
Telegram: @DD_party1
Other Named Individuals
Sam (Henry's predecessor), Flash (agent excluded from ST rebrand), Noah (agent with separate PC), Christi/Kristina (former logistics), Emanuel (field operative, NY), Lex (NY operative, codename 0044), David (LA operative, codename 0037), Jevan (IL operative, codename 0026, caught), Sergii (codename 104, NY), Terror and Ali (field agents), xyz / xyz000zz (fake ID maker on Telegram), a female operative (female operative, paid $1,500 via Zelle), FAKELAB (document forger, produces Russian passports for $3,500).
Operator Communication Network
This graph maps communications between actors in the chat export. The nodes correspond to members and are sized by message volume. Edges are weighted by shared-room activity.
Henry is the hub and is active in every room. Adrian is the co-hub through the Main DM, which carries 4,077 messages. The team splits into an operations cluster and a technical cluster, and Henry and Adrian bridge both. Three service contacts sit on the edge: FAKELAB the forger, xyz the ID maker, and Goldbear the cash-out exchanger.
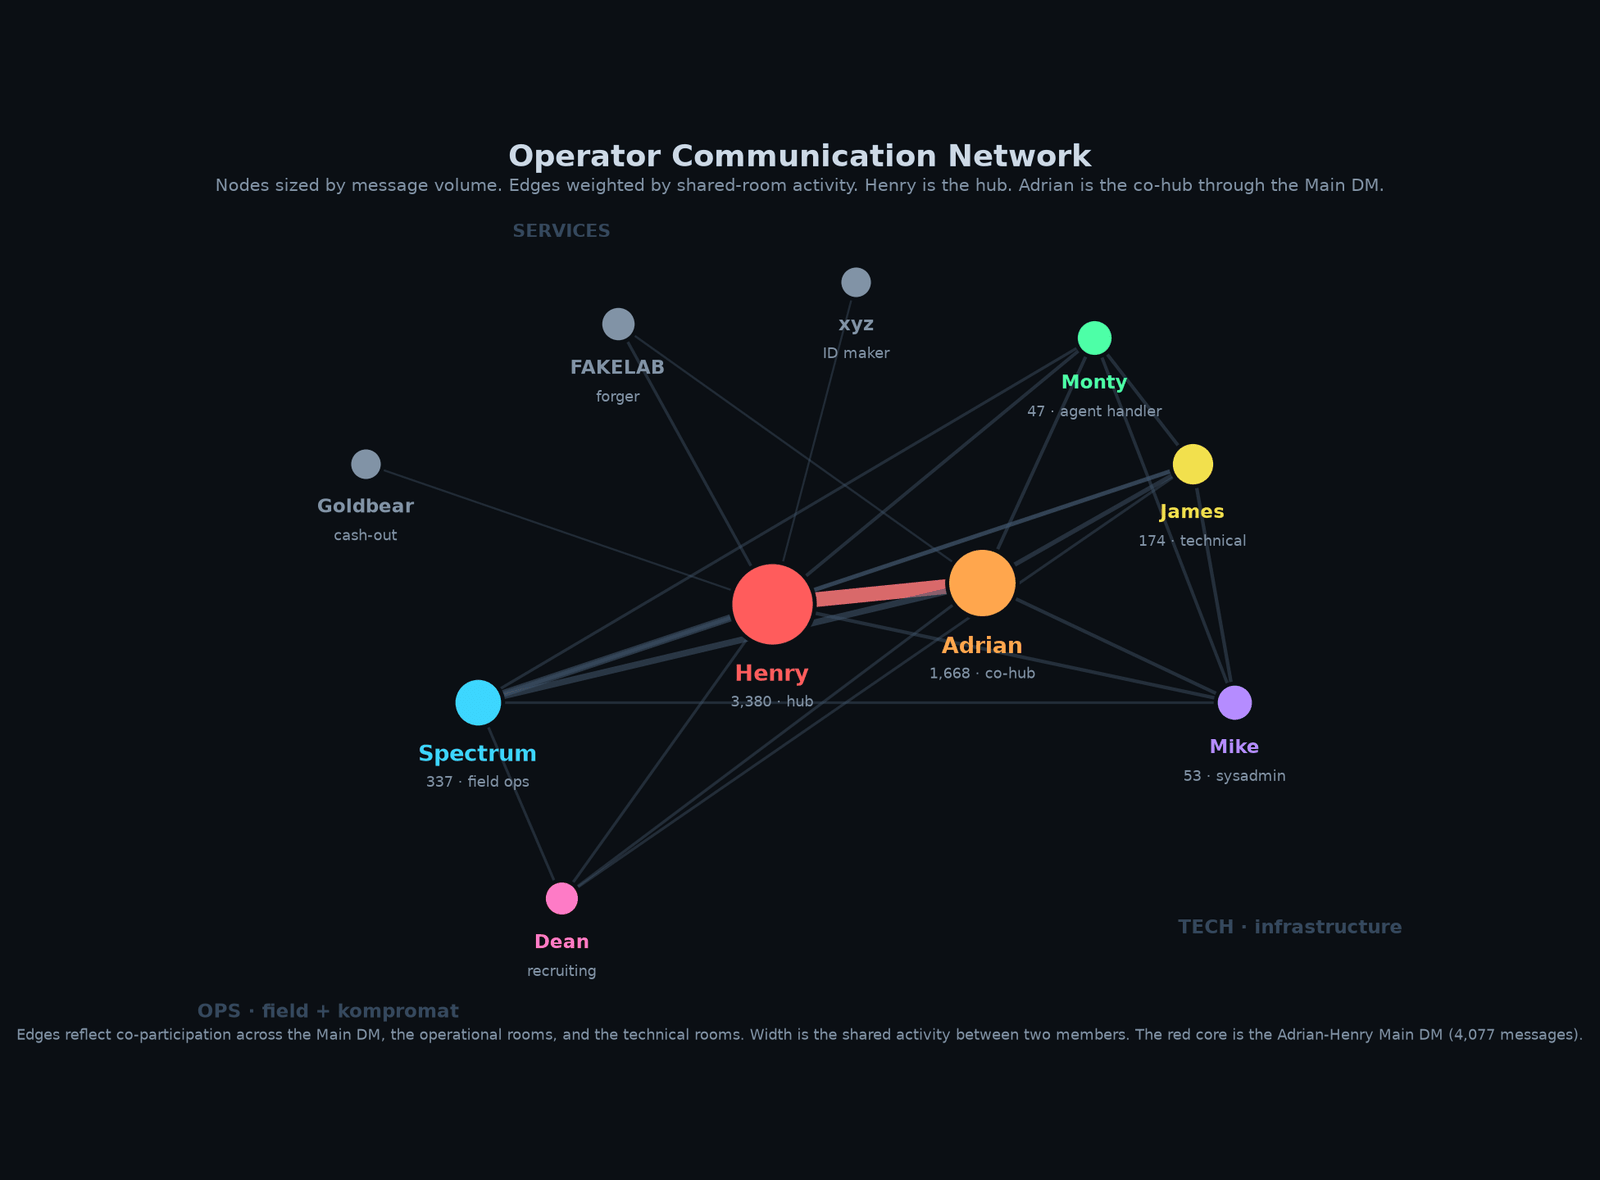
Operator communication network. Henry is the central hub and Adrian is the co-hub through the Main DM. An operations cluster of Spectrum and Dean and a technical cluster of James, Mike, and Monty are bridged by Henry and Adrian. Service contacts FAKELAB, xyz, and Goldbear sit on the periphery.
Most-Mentioned People
| Person | Mentions | Role |
|---|---|---|
| Jamel | 93 | External fixer: documents, smuggling, money |
| FAKELAB | 66 | Document forger |
| xyz | 47 | Fake ID maker |
| Lex (0044) | 25 | US field agent, New York |
| Evelyn | 18 | Smuggling recruiter |
| David (0037) | 17 | US field agent, Los Angeles |
| Flash | 13 | Agent dropped from the rebrand |
| Noah | 11 | Insider-operations operative |
| Terror | 8 | Field agent |
| A female operative | 6 | Female operative |
Operators rank low here because they direct-message each other and rarely name each other. The top nodes are all external support contacts, not internal operators.
Jamel: the Missed Hub
Earlier analysis treated this name as a relayed contact. The data shows he is the most-referenced external node, named 93 times, all through Henry. He is the connective tissue between forgery, smuggling, and cash-out.
рф комплект паспорт, загран, права возможно ли сделать? и можно ли с ними переходить границу
Translation: “RF set, passport, foreign passport, license, can you make it, and can you cross a border with them” Jamel (relayed by Henry), 2026-05-14
He commissions FAKELAB for the smuggling documents, brokers recruits, and coordinates physical movement with the cash-out handler Goldbear. His role is an external fixer for documents, logistics, and recruitment.
Newly Identified Contacts
- Paul: An internal operative on the bribed-cleaner and insider line, working with Noah. Not in the prior analysis. Paul, 2026-05-20, FAKE_CLEANER: "when we already have cleaners in corps we will call oldies from IT and ask them to join zoom".
- Evelyn: A smuggling recruiter. She authored the four-step Mexico plan that Henry relayed on 2026-05-06.
- OJ (
@MoeSolnce1010): A physical-operations coordinator with a work van. He is told when to send people to target addresses. OJ task, 2026-03-13: "@MoeSolnce1010должен быть в курсе когда на адреса отправлять людей" (OJ must know when to send people to the addresses). - Emanuel: A New York scout who worked neighborhoods with Lex and is tied to Spectrum's honey-trap line, Spectrum 2026-03-13: "lets hire some prostitutes."
- A female operative: The operative from the table above. A $1,500 starting salary paid by Zelle. Brought on in September 2026.
- Agent Z: A high-value operative on explicit terms, 10,000 dollars per month with 15,000 dollars owed. His wallet was never funded. See the payroll table below.
Agent Telegram Handles and Codenames
The February 2026 roster in SPR_TRG_TALK gives codenames, Telegram handles, and cities for the US field agents. These harden attribution.
| Agent | Codename | Telegram | City | Notes |
|---|---|---|---|---|
| Lex | 0044 | givingbunny | New York, then Miami | Ready |
| David | 0037 | david_ernand | Los Angeles | Moved to New York |
| Jevan | 0026 | jevan2333 | Chicago | Caught |
| Sergii | 104 | sergiinyvlaso | New York | Group claimed to link this handle to ID maker xyz (unverified) |
| Nick | - | - | New York | ID failed twice |
| Jackonda12 | 0017 | Jackonda12 | Los Angeles | Undecided |
| seblabyt | 007 | seblabyt | Los Angeles | No Response |
| [handle withheld] | 0043 | [handle withheld] | - | entry flagged underage* |
*One roster entry, codename 0043 ([handle withheld]), is flagged in the chat as underage.
Payroll Network
The December 2025 payroll and later payments name a salaried support network behind the operators. The amounts and wallets are from the chat and are verified on-chain in the Technical Infrastructure section.
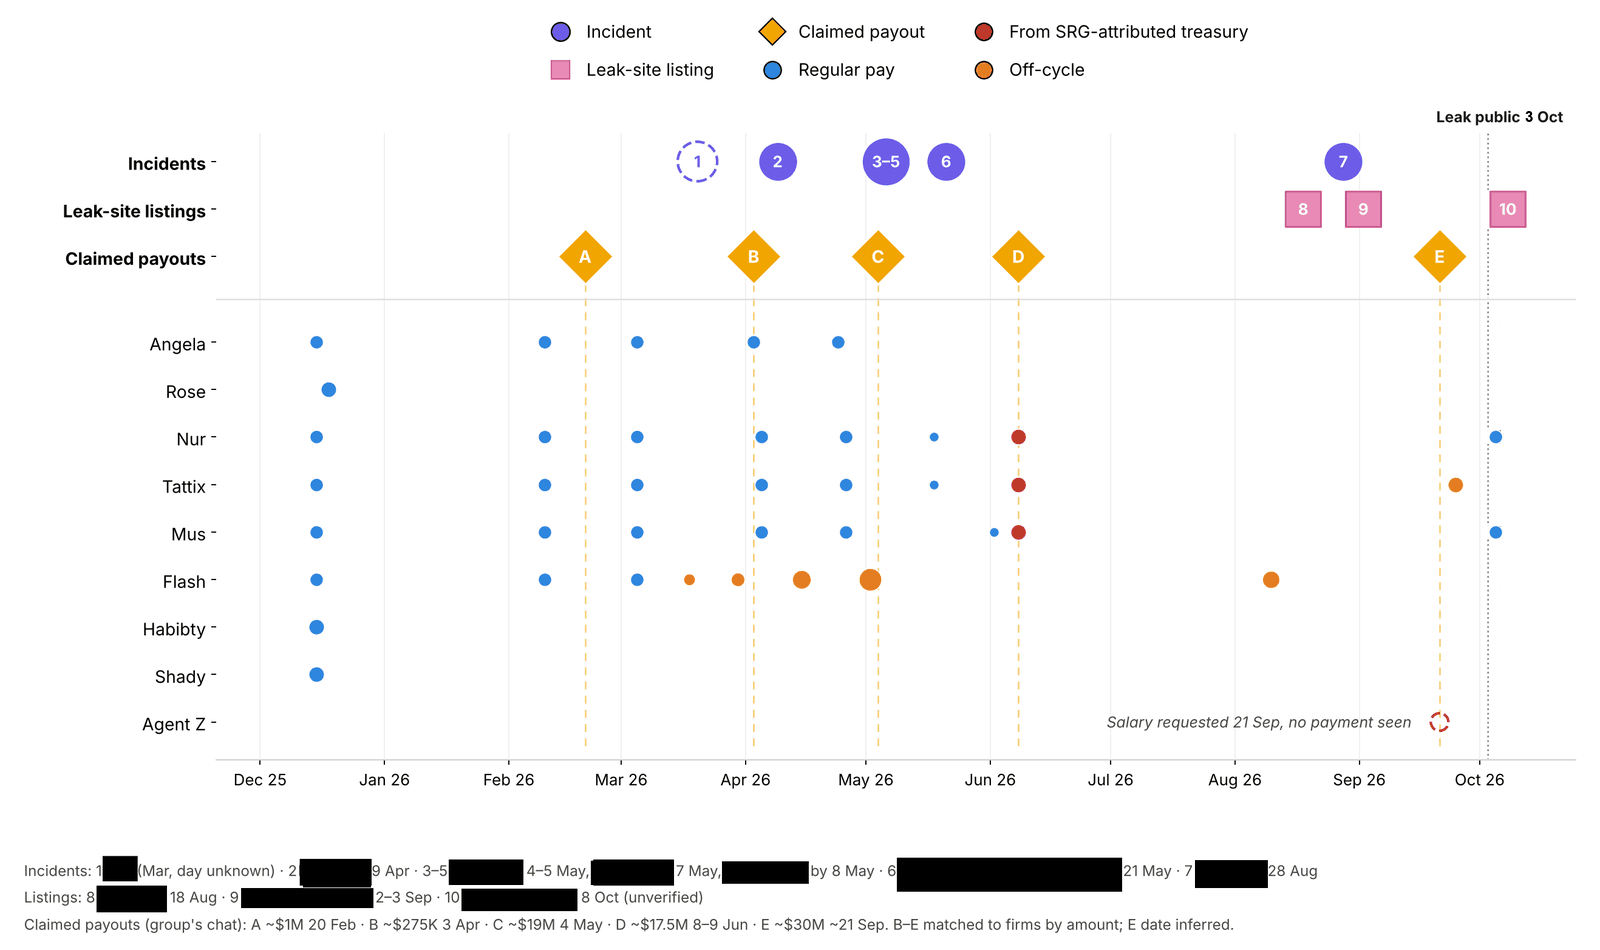
Payroll payments by recipient against incidents, leak-site listings and claimed payouts, December 2025 to October 2026.
| Name | Role | Pay | Wallet |
|---|---|---|---|
| Angela | Mid-level manager, controls the process | 2,000 USD | bc1q6q9ww5ddr7gculnmmqkvg8944f6ecmzqd4m0kd |
| Rose | Back-pay and bonus, Main and SPR TRG | 3,000 USD | bc1qyw5m89wz49k5gddlssu9gu6n8njxyw06rqx9fn |
| Nur | Network agent | 2,000 USD | 19A5zQ4YCUw8TMJBpFdyTT3DbKv6XFLN42 |
| Tattix | Main agent | 1,000 USD | 15HP3kzUGTFQQuDfSqz85gvLz2h6si2evY |
| Mus | Network agent | 500 USD | 15hm9UAGeAmq9f8itDMKg1b8BKwwzJnAUu |
| Habibty | Network member | 1,000 USD | bc1qsr6zp3wflsh8s53xkjz57rc0gh5qc2myfkpx72 |
| Shady | Network member | 1,000 USD | bc1qgnzynkd42ltj9e55hc8ssfga7ecsptzcx43qsw |
| Flash | Agent, dropped at the rebrand | 1,000 USD | 12Vk8p7nKXPLcKtaPMZ5dW6e12AoyECQW8 |
| Agent Z | High-value operative, 10,000 USD per month, 15,000 owed | Unpaid | bc1q62pxr8sgc4jzhxsrw2f709d7ldfadhflrvwywz, never funded |
Angela stands out here as a manager who controls the process as opposed to a mere wallet, and her wallet took 79 deposits, the most of any in the set. Agent Z is the opposite case, a high-value operative who was never paid and is a strong cooperating-witness lead.
Analysis
We traced payments to the nine people the chats name as paid staff. Eight of the nine received 52 payments totalling about $72,000 between October 2025 and October 2026. The manager averaged $2,021 per payment and the caller Flash $2,096 ($892 on regular pay days).
The managing staff member averaged $949, the “main agent” $886, an operator $784 and two one-off members $1,001 each, and one coordinator received a $3,502 bonus. The ninth, Agent Z, a US-based task-setter, is recorded as owed $15,000 but was has not been identified on-chain. The chats claim that 27 firms paid about $207 million. The payroll is 0.035% of that figure, or $1 for every $2,871, and 0.015% for the 3 April to 24 September period in which the payouts were claimed. Public reporting puts one in-person visit to a law firm at $500, and one principal’s $380,000 share of a single $19 million payout was 5.3 times the entire payroll.
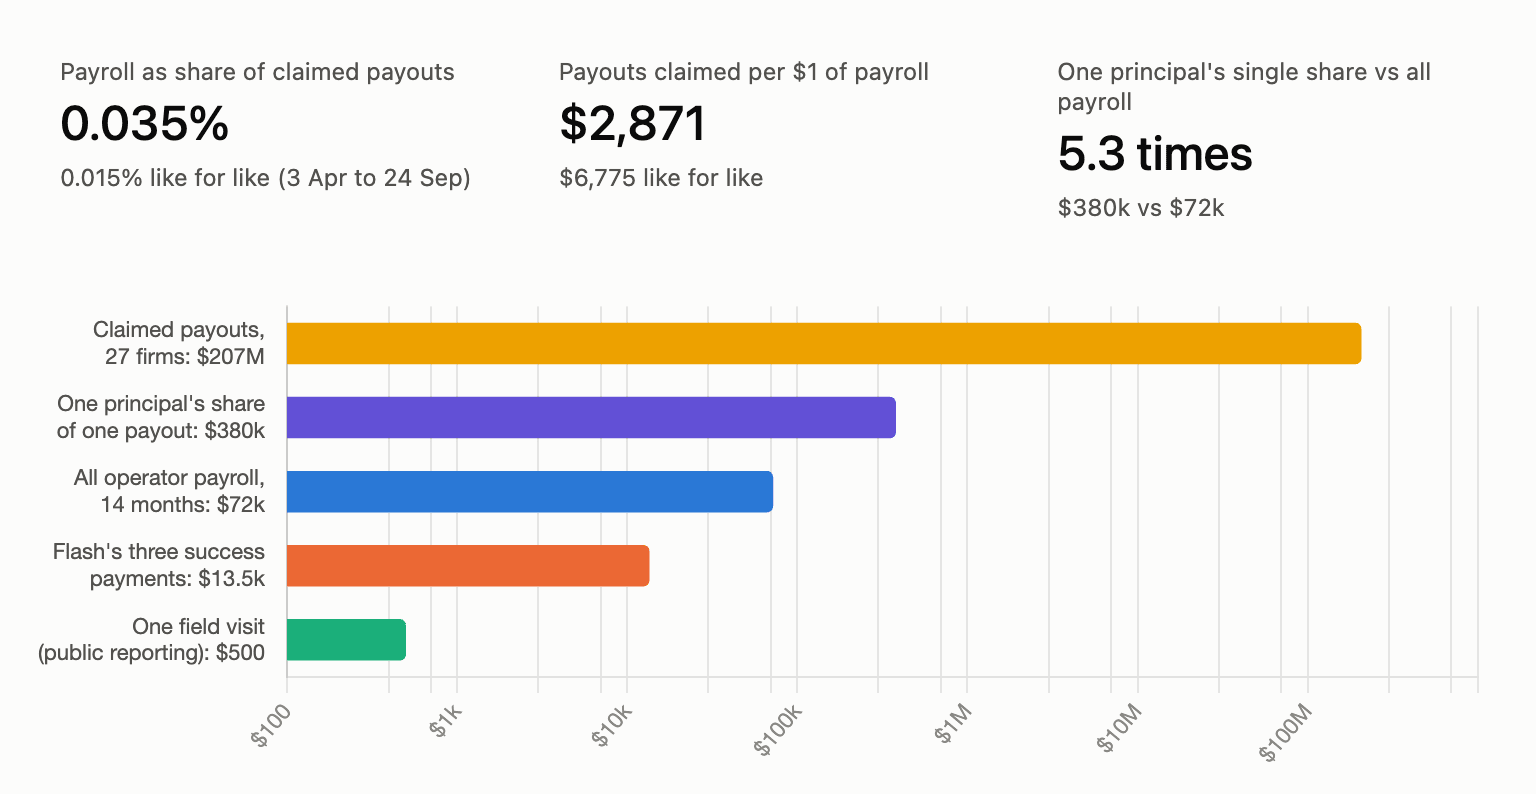
Operator payroll against claimed payouts: all payroll over 14 months was 0.035% of the $207M the group claimed.
Pay followed rank and tenure for most staff, but Flash was paid for results. The chats credit him with three separate firms. He received $2,500 on 30 March, $5,002 on 9 April (the day after one firm was marked paid at $700,000) and $6,005 on 24 April (the day one firm’s first offer was posted, before it was marked paid at $10 million on 1 May). The principals’ remarks track the same weeks: “Flash is making lots of successes” on 24 April, “Flash did that” on 29 April and “he’s the best so far” on 4 May. The three payments total $13,507, about 0.13% of the $10.7 million claimed for the two firms. The largest equals 84% of a month of New York’s median household income ($85,820 a year), while a regular $900 payment is 13% of that month and about 30% of a full-time New York City minimum-wage month at $17 an hour.
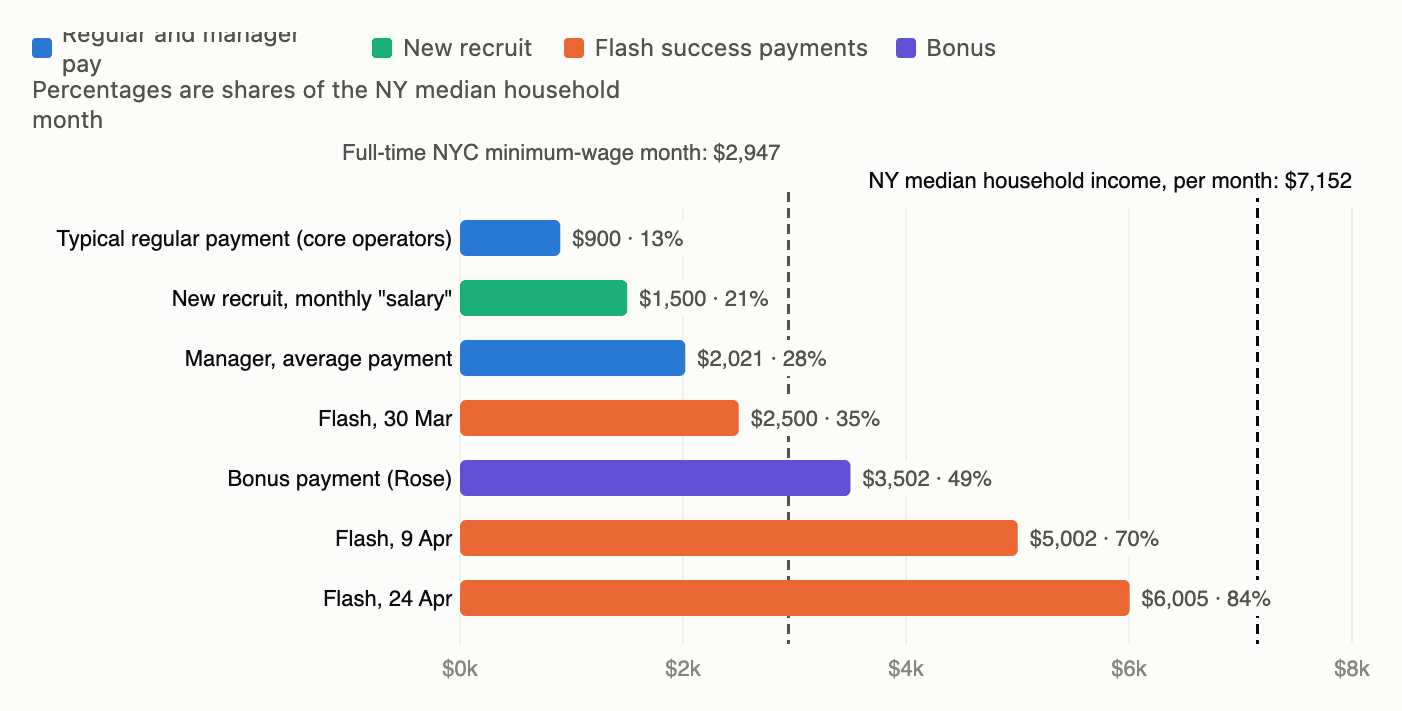
Individual payments compared with New York monthly income benchmarks.
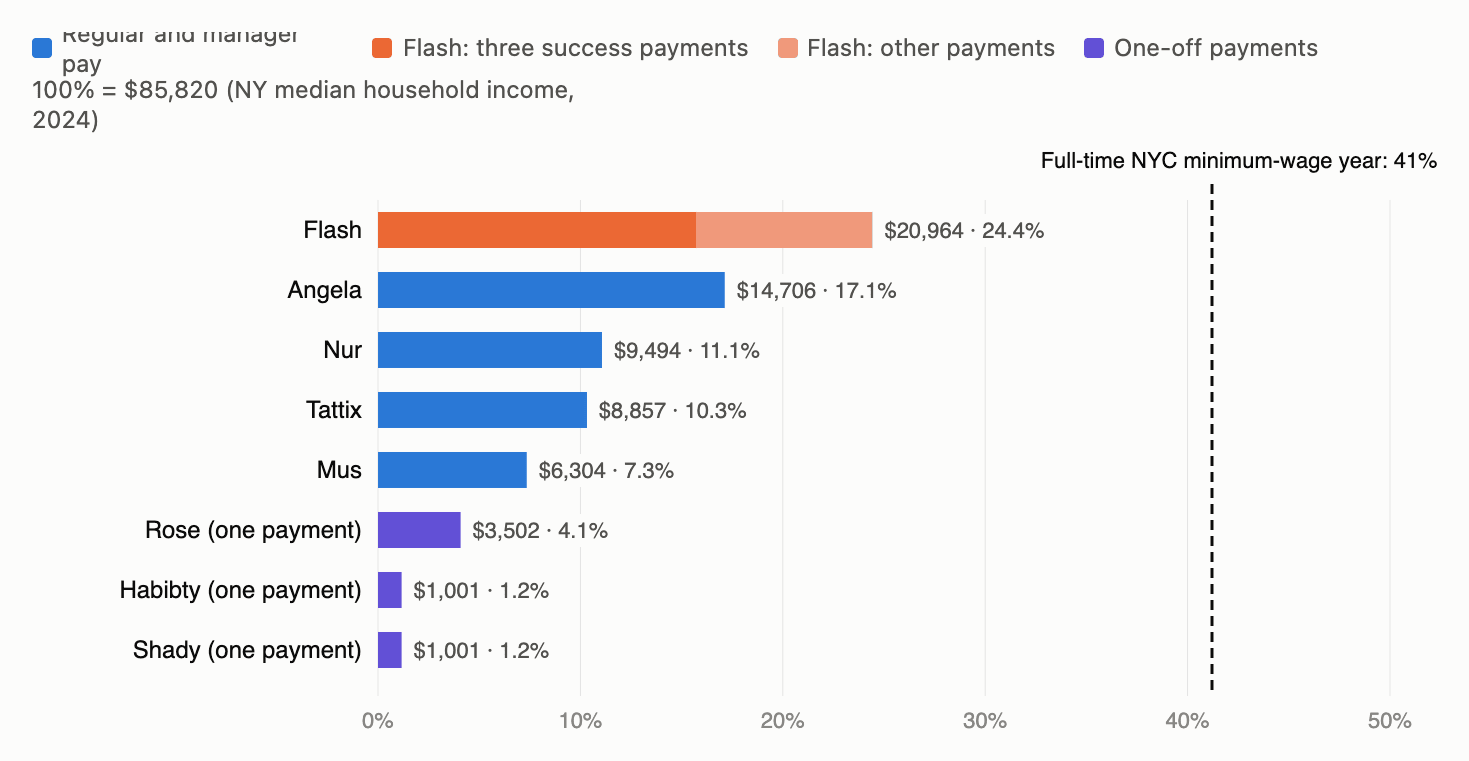
Total payments per recipient as a share of New York median household income (2024).
The chats show recruitment through Russian-language adverts for nightclub “promoters” in Miami, Orlando and New York at $300 or more a night, a plan to approach groups of ‘refugees’ - most likely referring to Russian diaspora - and a man described as having gone to the war from prison, deserted and been living illegally in Brazil.
One September payee received $1,500 as a “salary so she can start working”, and $3,400 went to a forged-document vendor the same day.
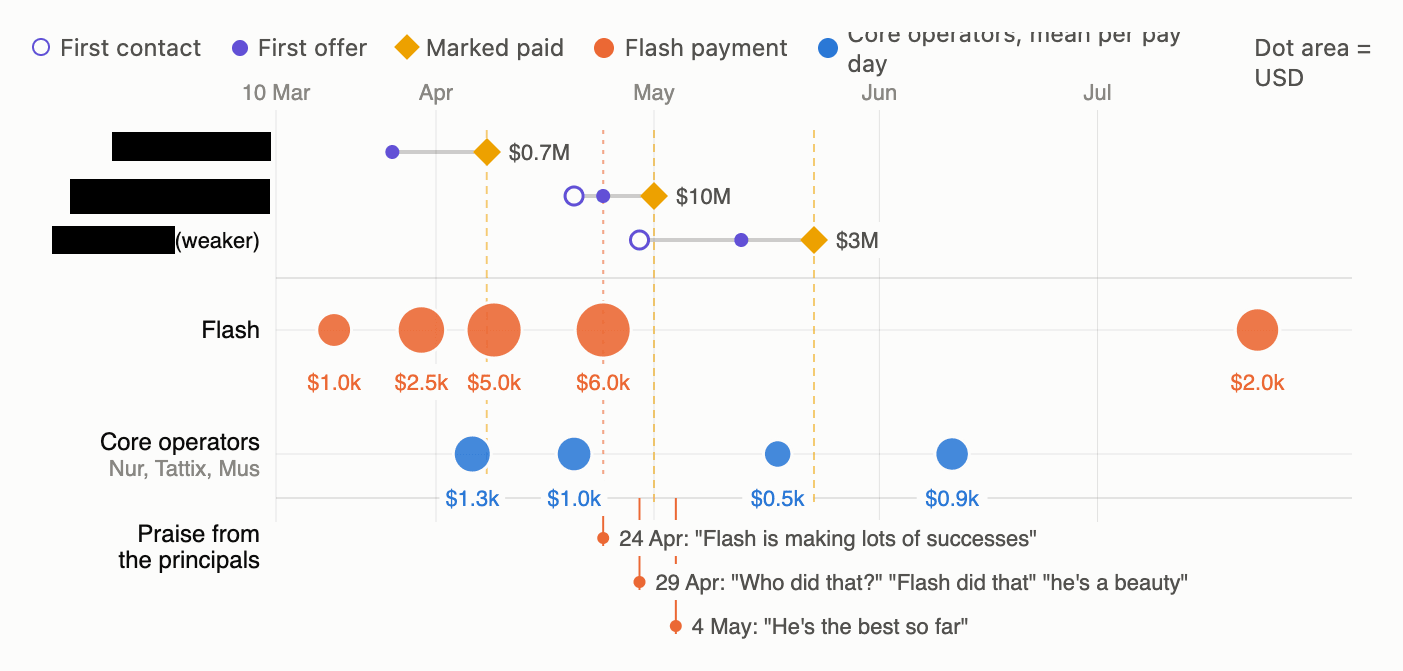
Negotiation timelines for three redacted firms against payments to Flash and the core operators, March to July 2026.
This recruitment pattern is documented elsewhere as the “disposable agent” model used in Russian sabotage/influence operations in Europe: people recruited online for single tasks and paid hundreds to thousands of euros, often in cryptocurrency, through small amounts and fragmented payment chains that are difficult to detect.
The SRG chats show the same features: adverts with cover stories, small crypto and peer to peer payments, fake IDs provided “just to reassure the agents”, and a principal’s description on 20 February of the field programme as a conveyor belt in which many agents drop out and some enter a building only once. Other cases linked to China and Saudi Arabia involve recruits with a national connection but payment for access. A US survey finds nationality is a predictive factor in Chinese espionage recruitment, and in a Saudi-linked case at Twitter one recruited employee received at least $300,000 and a $20,000 luxury watch, compared with $350 to $6,000 in the SRG payroll.
FAKELAB’s own cash-out is low in volume but methodical. The forger appears to move its proceeds through drop accounts on the HitBTC exchange rather than cashing out under its own name.
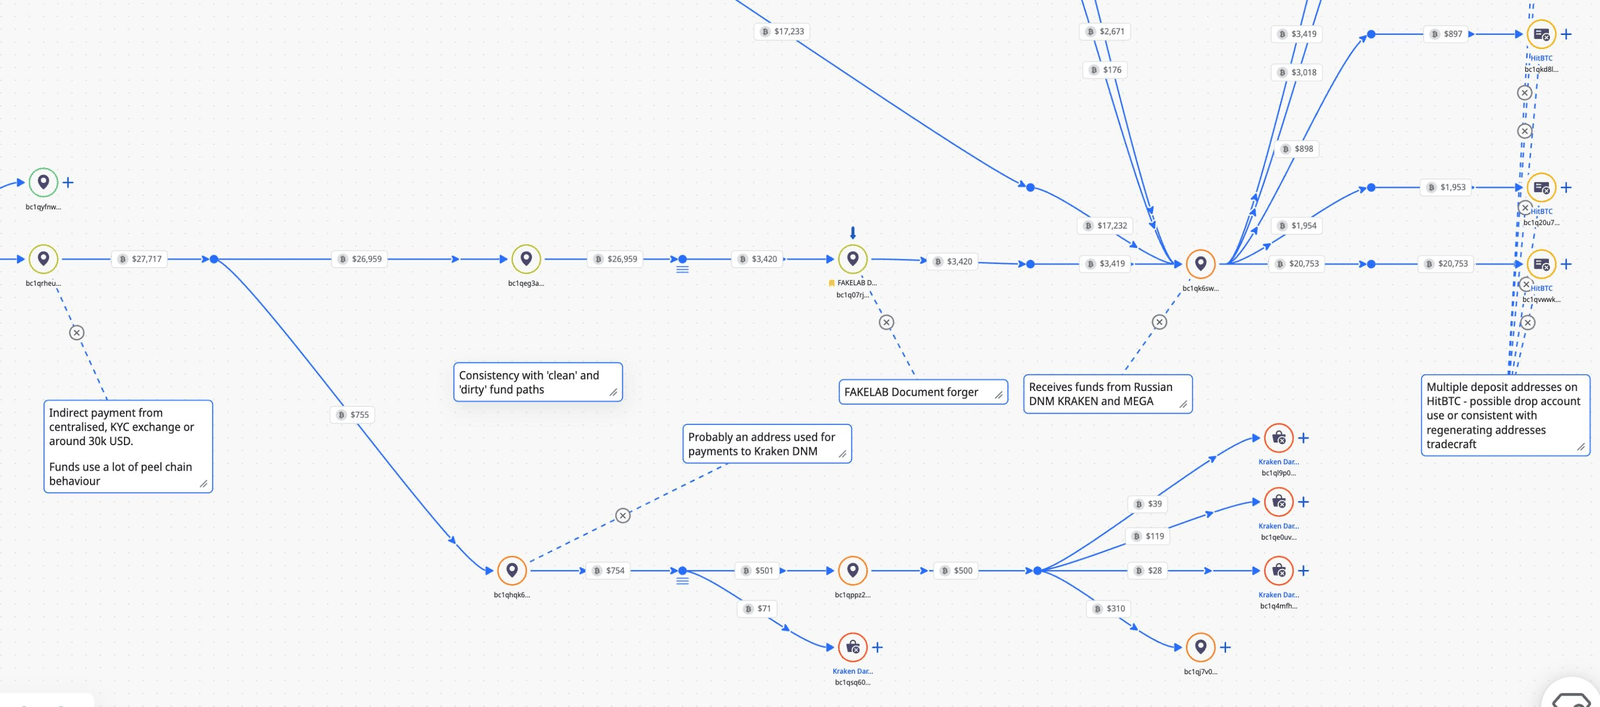
On-chain tracing of payroll funds through the FAKELAB document forger, the Kraken darknet market and HitBTC deposit addresses.
A large share of FAKELAB’s funds also routes through Kraken Darknet Market, split across two separate paths. That split spreads risk and limits exposure on any single route. This is the mark of an operator who manages funds deliberately, not an amateur.
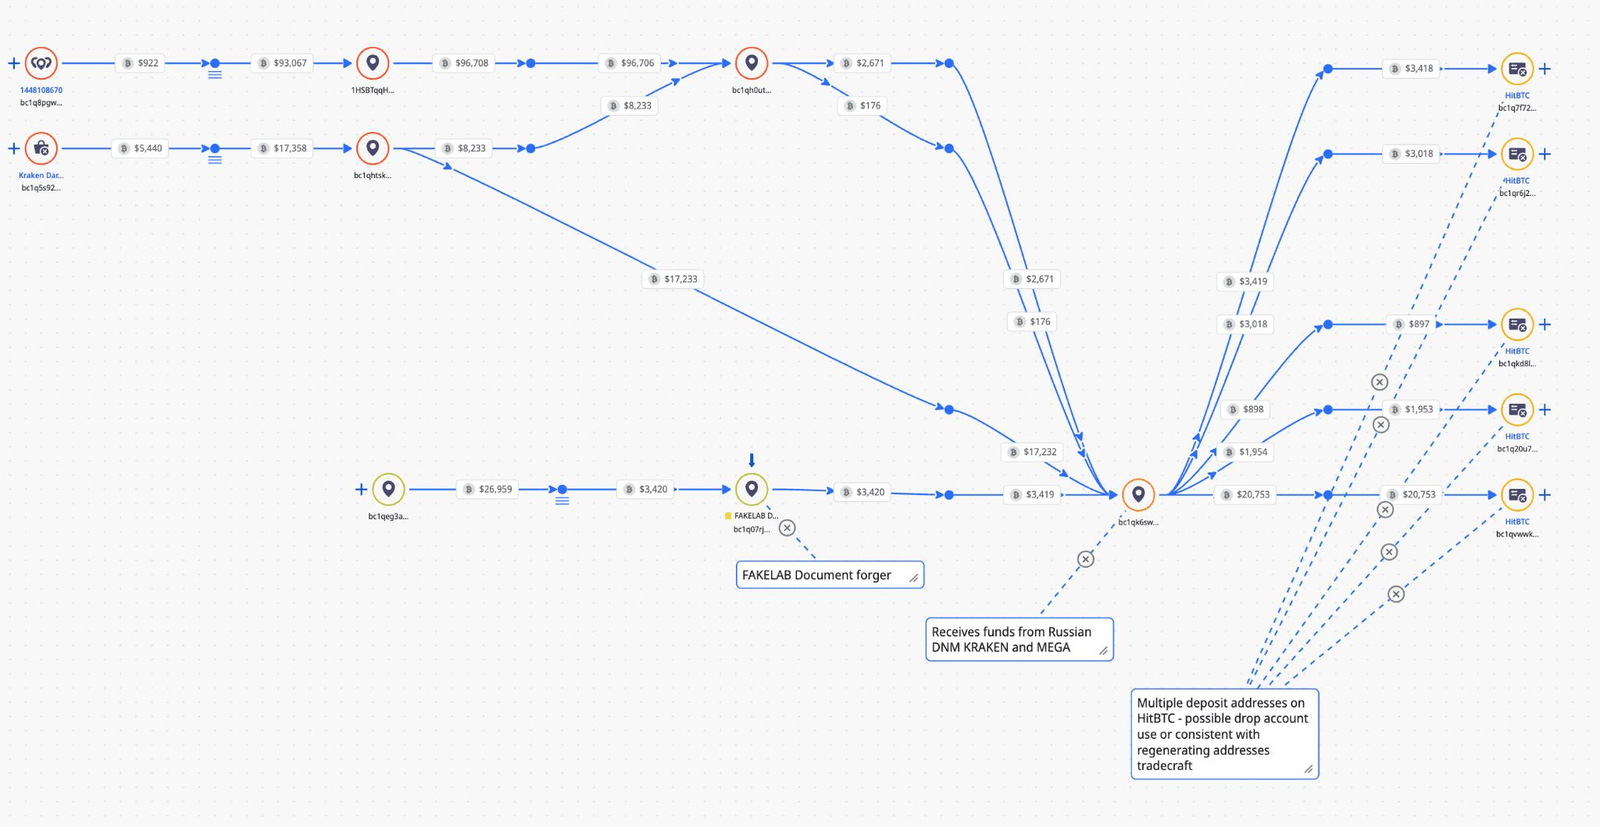
The FAKELAB-linked wallet cluster and its HitBTC deposit addresses.
Operator Activity Analysis
Regular messaging times can help to triangulate where the threat actors are located. Rocket.Chat buckets every message by its UTC hour: On 2026-05-18, Adrian tells the team to be online "с 11 утра мск по ua" (from 11am Moscow time, by Ukraine time). 11:00 Moscow time is 08:00 UTC. The group morning activity starts at 08:00 UTC, solidifying this. The active window is read against the quiet window to approximate working times.
Operator Clocks
| Operator | UTC active window | Peak (UTC) | Compatible offset | Confidence | Notes |
|---|---|---|---|---|---|
| Adrian | 10 to 22 | 17 | UTC+3 (Moscow/Kyiv) | Confirmed | Explicit "11 утра мск" scheduling message |
| Henry | 10 to 22 | 17 | UTC+3 | Probable | Pattern identical to Adrian. Shares the group clock. States intent to move to Russia. |
| Spectrum | 11 to 13, 17 to 23 | 22 | UTC-4 to -7 (US) | Probable | US daytime pattern. Inverted from the core pair. Runs US field operations. |
| James | 13 to 22 | 17 | UTC+2 to +4 | Possible | Loosely tracks the core evening. Few messages (174). |
| Dean | Scattered | 09 | Indeterminate | Insufficient | Too few messages (23) |
| Mike | Scattered | 21 | Indeterminate | Insufficient | Too few messages (53) |
| Monty | 14 to 19 | 19 | Indeterminate | Insufficient | Too few messages (47) |
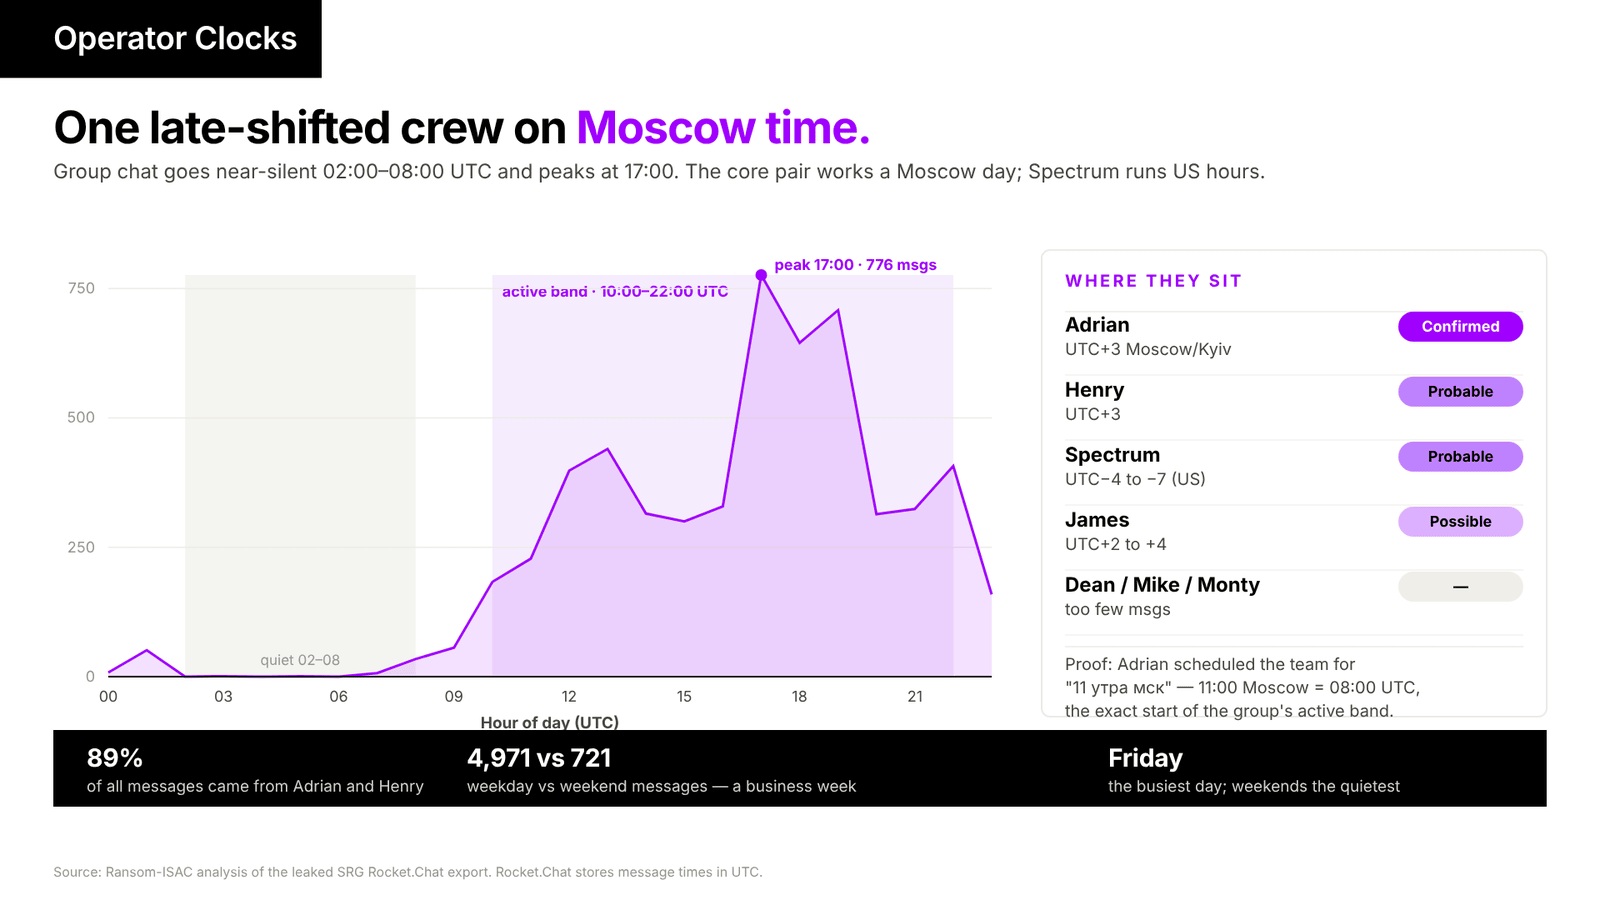
Group message volume by hour of day in UTC. The active band runs 10:00 to 22:00 and peaks at 17:00. Near silence falls 02:00 to 08:00. The attribution panel places Adrian and Henry on Moscow time and Spectrum on US hours.
Hourly Activity by Operator
The chart below plots message count against the UTC hour, one line per operator. The core pair, Henry and Adrian, drive one evening peak at 17:00 UTC. Spectrum runs an inverted clock and peaks at 22:00 UTC, which fits a US daytime operator.
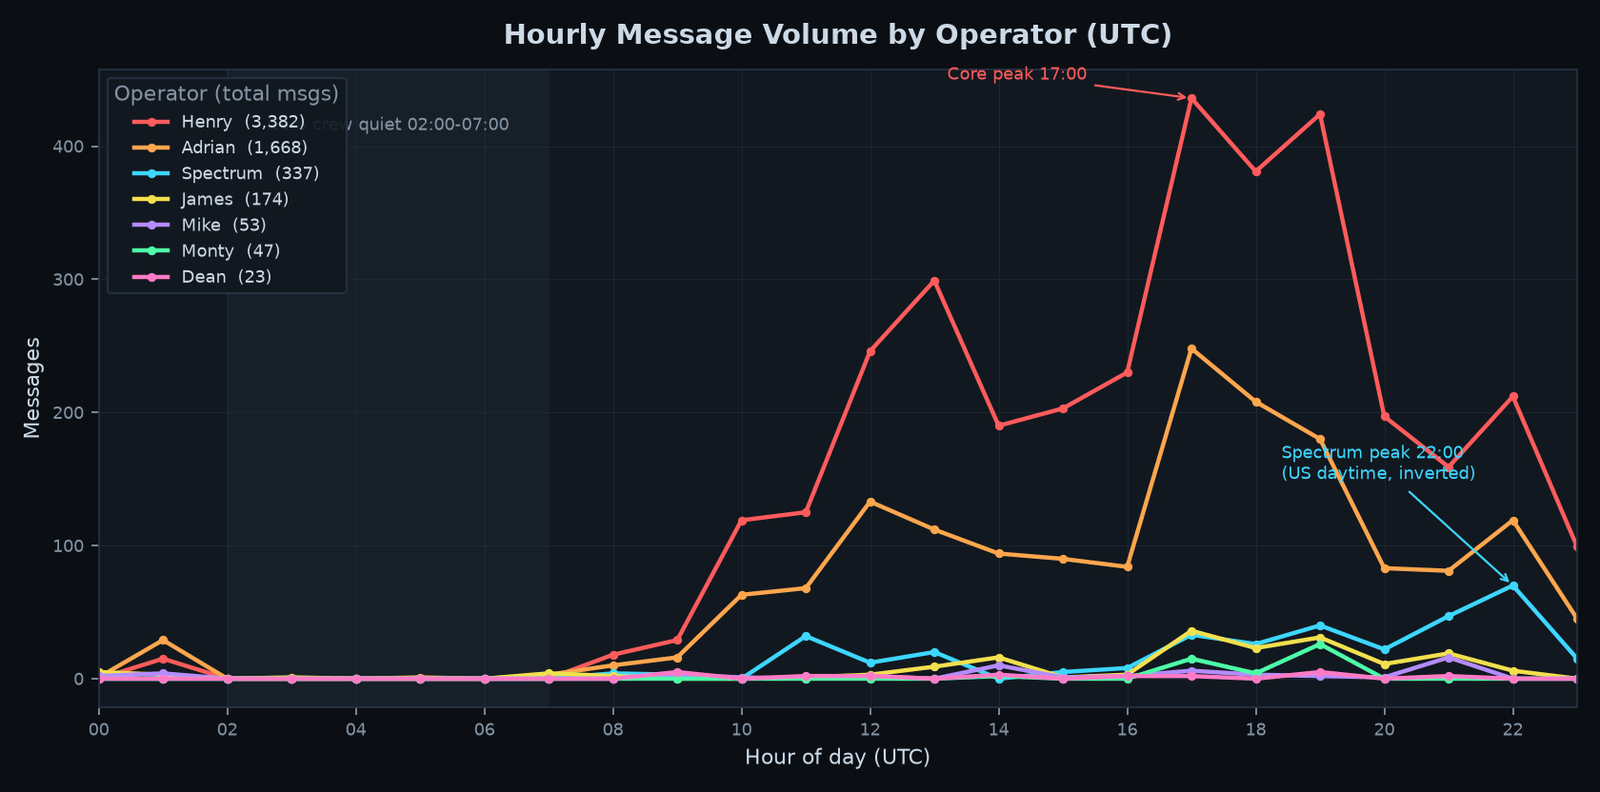
Hourly message volume by operator in UTC. Henry and Adrian peak at 17:00. Spectrum peaks at 22:00.
The next panel scales each operator to their own busiest hour, so the shape shows the clock and not the volume. It separates the UTC+3 crew from the US-side operators even for the low-volume accounts.
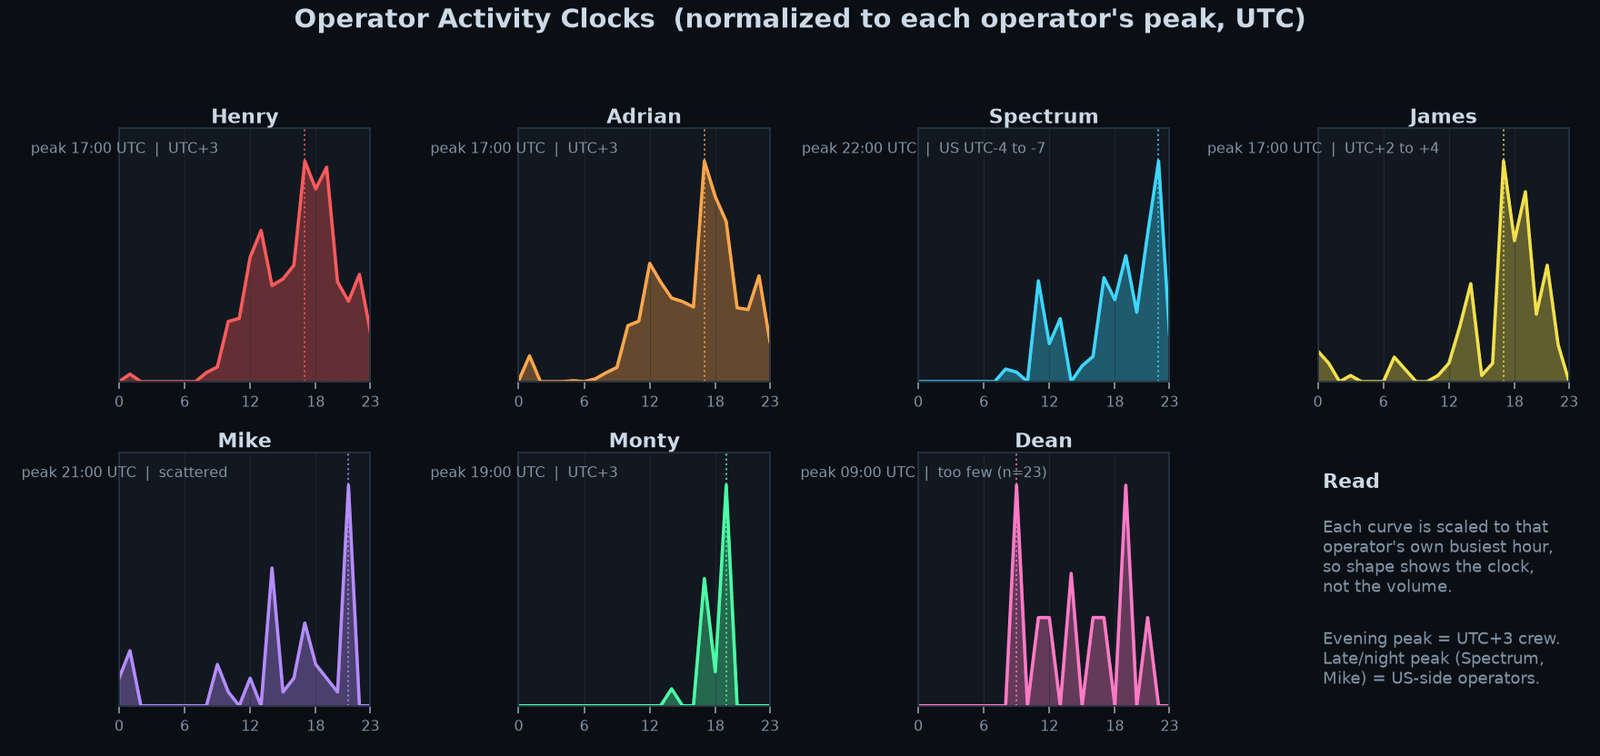
Operator activity clocks, each curve normalized to its own peak hour, UTC.
Analysis
The core pair, Adrian and Henry, appear to share one clock. Both go silent from 23:00 to 09:00 UTC and peak at 17:00 UTC. In Moscow time, that is a work day of 13:00 to 01:00 with a peak of activity at 20:00, aligning with a relatively normal late-shift.
Spectrum runs on a different clock. His activity sits in the US daytime and inverts the core pair. This matches his role as the US field operations lead.
The pasted agent logs inside the chat carry their own timestamps and cluster in US Eastern (UTC-5) and US West (UTC-7) time.
Working Rhythm
The group works a conventional week. The chat averages about 40 messages per weekday and about 29 on weekends.
Friday is the busiest day, and Saturday and Sunday are the quietest. The Friday peak may reflect end-of-week extortion deadlines or payroll.
Operational Activity Curve
The milestones below mark the shape of the operation across 13 months.
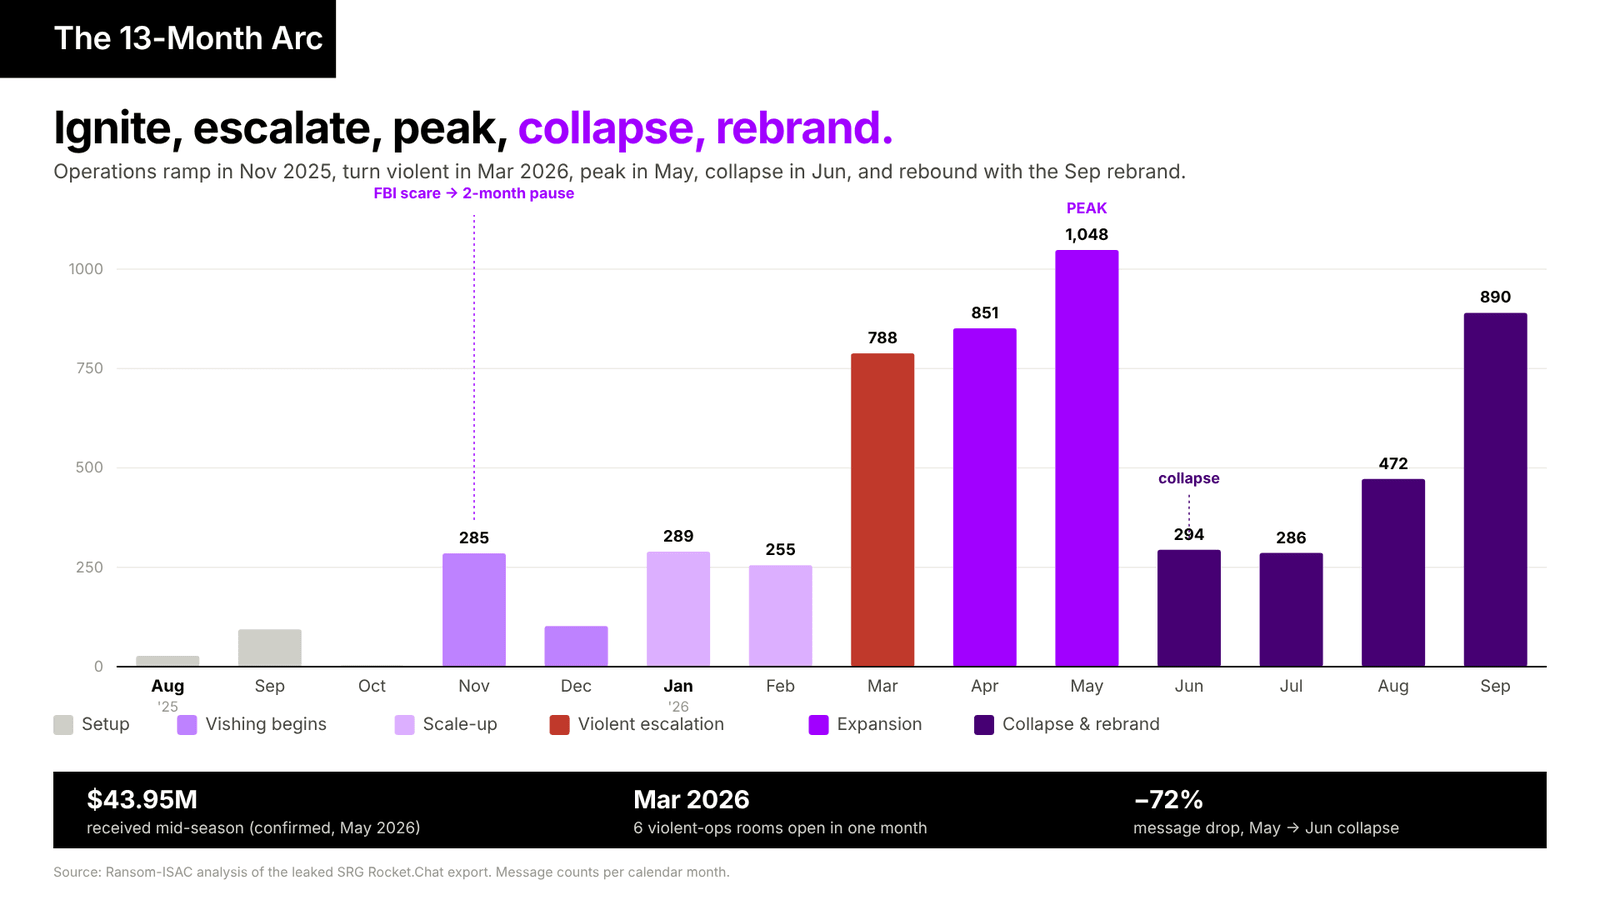
Monthly message volume across the operation, colored by phase. Operations ramp in Nov 2025, turn violent in Mar 2026, peak in May, collapse in Jun, and rebound with the Sep rebrand.
Chat activity ignites in November 2025. It pivots to violence in March 2026, peaks in May 2026, then collapses in June 2026, a near-total three-month drop. It then rebounds in September 2026 with the Sleepless Threat rebrand.
Activity by Hour (UTC)
The group runs on a single late-shifted clock. The busiest hour is 17:00 UTC with 776 messages. The active band runs from 10:00 to 22:00 UTC. Near silence runs from 02:00 to 08:00 UTC. In Moscow time, which the Operator Timezone section confirms as the group clock, the peak is 20:00 and the quiet hours fall in the early morning.
UTC hour   00  01  02  03  04  05  06  07  08  09  10  11  12  13  14  15  16  17  18  19  20  21  22  23
Messages    8  51   0   1   0   1   0   7  34  56 183 228 398 440 315 300 329 776 645 708 314 324 407 159
The per-operator hour histograms, the day-of-week split, and the timezone attribution are in the Operator Timezone and Working-Hours Analysis section above.
Message Volume Overview
These two charts show who talked and where. The command channel is a two-person desk.
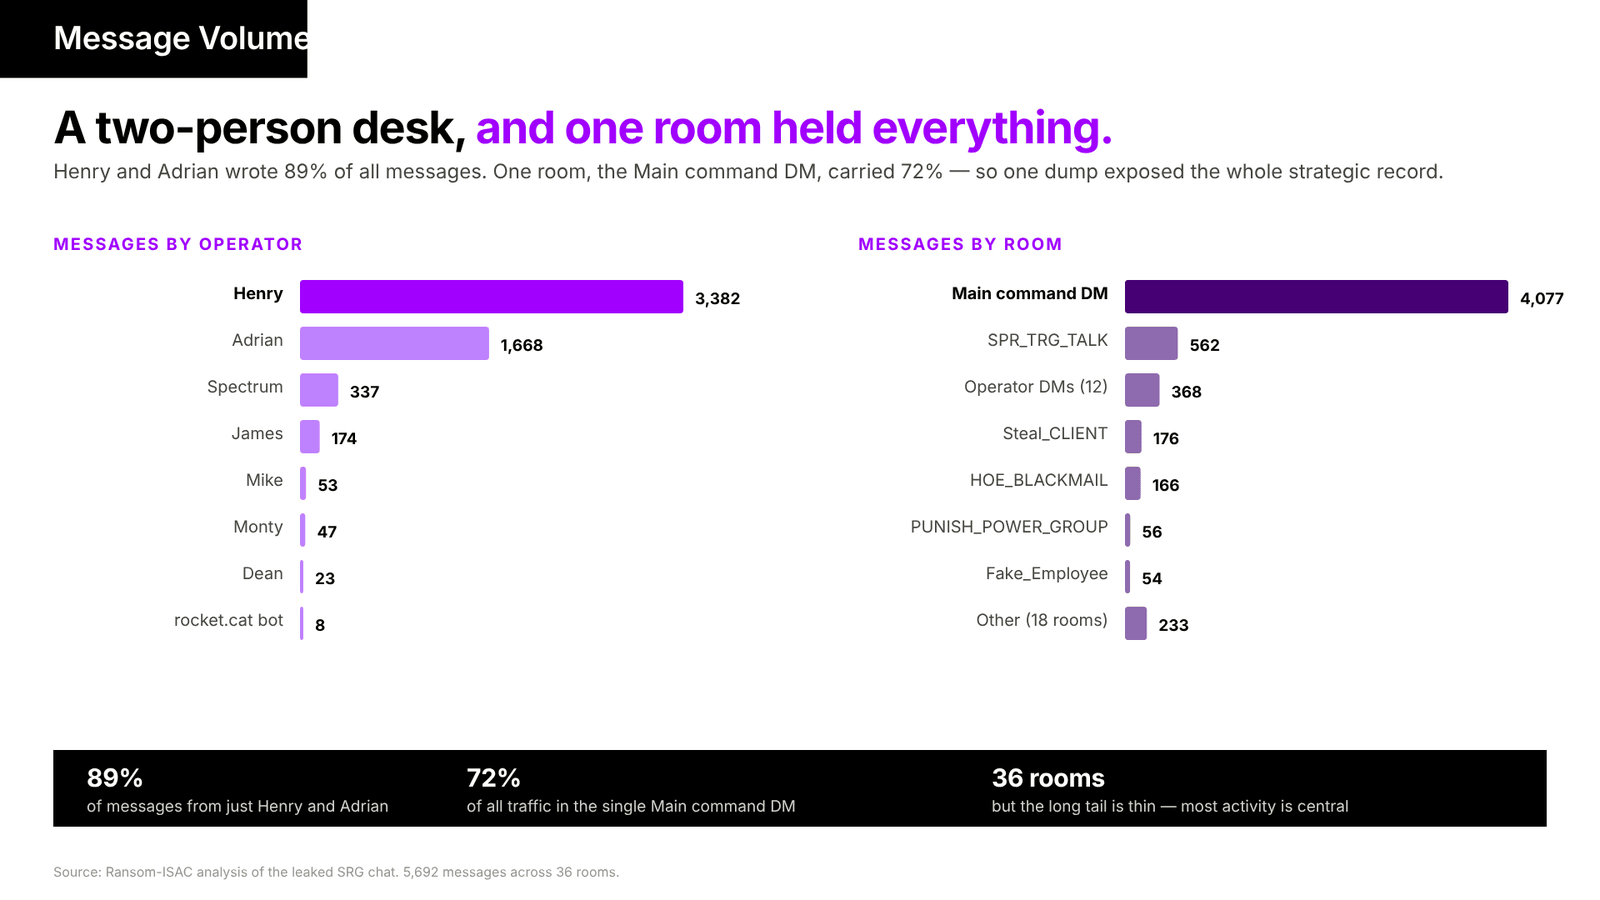
Message volume by operator and by room. Henry and Adrian wrote 89% of all messages, and the single main command DM carried 72%, so one dump exposed the whole strategic record.
Henry and Adrian wrote 89 percent of all messages. One room, the Main command DM, holds 4,077 of 5,692 messages, which is 72 percent.
Operational Phases
The room creation dates and the operator tenures fall into six phases.
| Phase | Period | What marks it |
|---|---|---|
| Setup | Aug to Oct 2025 | Only the Main DM and the infrastructure DMs are active. Founders Adrian, Henry, and James. |
| Vishing begins | Nov 2025 | SPR_TRG_TALK opens. An FBI scare on 2025-11-24 triggers a two-month pause. December is dormant. |
| Scale-up | Jan to Feb 2026 | Operations resume. Vishing volume returns. |
| Violent escalation | Mar 2026 | Six rooms ignite in one month: kompromat, kidnapping, armed enforcement, and physical infiltration. Dean joins on 2026-03-13. |
| Expansion | Apr to May 2026 | Fake employee placement, naval HUMINT, deepfake planning, and private investigators. May is the peak month at 1,048 messages. |
| Collapse and rebrand | Jun to Sep 2026 | A June collapse, then the Sleepless Threat rebrand in September on a new server. Mike and Monty join for the rebrand. |
Campaign Activity Windows
Each operation has a clear active window, with espionage lines planned in tight bursts, not continuously.
| Operation (Room) | Active Window | Peak | Notes |
|---|---|---|---|
| Main DM | Aug 2025 to Sep 2026 | Sep 2026 | The command channel. Live every month (4,077 messages). |
| SPR_TRG_TALK (vishing, infiltration) | Nov 2025 to Jun 2026 | Mar 2026 | The core operations room |
| Steal_CLIENT (kidnapping) | Mar to Jul 2026 | May 2026 | Peaks during the expansion phase |
| HOE_BLACKMAIL (kompromat) | Mar 2026 | Mar 2026 | Single-month burst |
| PUNISH_POWER_GROUP (armed) | Mar 2026 | Mar 2026 | Single-month burst |
| Fake_Employee (sleeper agents) | Apr to May 2026 | May 2026 | The defense contractor placement push |
| GAY_MARINES_PUBS (naval HUMINT) | May to Jul 2026 | May 2026 | The submarine base targeting |
| DEEPFAKE_DATALOADING | May 2026 | May 2026 | Single-month burst |
| Sep victim rooms and ST OPSEC DMs | Sep 2026 | Sep 2026 | The rebrand, on the secondary server |
Operator Tenure Windows
| Operator | First | Last | Messages | Read |
|---|---|---|---|---|
| Adrian | 2025-08-27 | 2026-09-28 | 1,668 | Founder, present throughout |
| Henry | 2025-08-27 | 2026-09-29 | 3,382 | Founder, present throughout. Sent the last message in the data. |
| James | 2025-08-27 | 2026-09-28 | 174 | Founder, present throughout. Infrastructure. |
| Spectrum | 2025-11-12 | 2026-05-07 | 337 | Field-ops era only. Goes silent three weeks before the June collapse. |
| Dean | 2026-03-13 | 2026-06-26 | 23 | Joined for the violence phase. Gone by the collapse. |
| Mike | 2026-09-02 | 2026-09-29 | 53 | Rebrand hire. Secondary server only. |
| Monty | 2026-09-21 | 2026-09-28 | 47 | Rebrand hire. Secondary server only. |
Charting the tenure windows confirm the operational phases outlined above. The three founders (Adrian, Henry and James) were present for all 13 months. Spectrum joined in November 2025 and went silent three weeks before the June collapse. Dean entered when his services were most needed, during the escalation phase in which the group discussed in-person operations such as kidnapping and infiltrations, and was gone by the collapse in June.
Activity Heat Map by Operator and Month
The heat map shows each operator's message count per month across the full date range. The operation builds from November 2025, turns violent in March 2026, peaks in May 2026, collapses in June, and rebounds with the September 2026 rebrand. The rebrand hires Mike and Monty appear only in the final column.
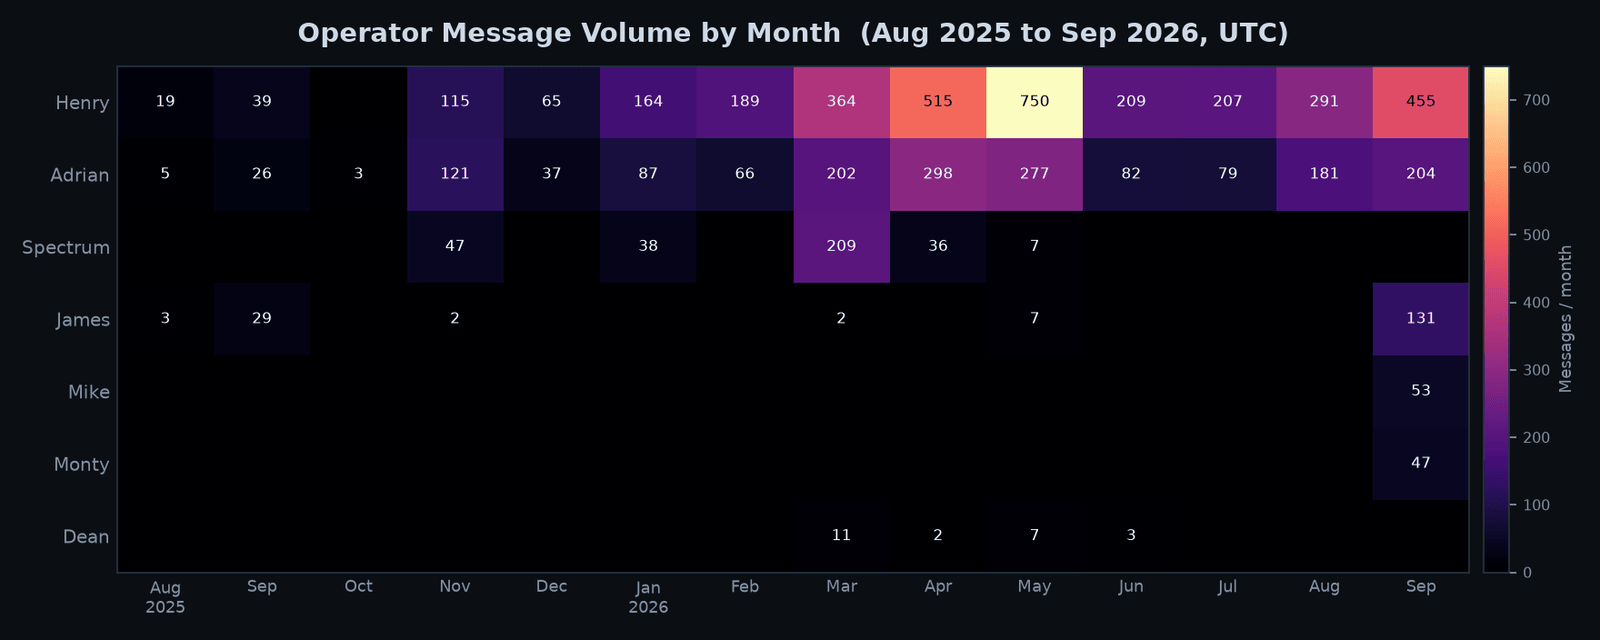
Operator message volume by month, August 2025 to September 2026. Henry peaks at 750 messages in May 2026.
Notable Periods
Chat Timeline
Show table (40 rows)
| Date | Event |
|---|---|
| 2025-01-04 | Fake resume PDF created via Canva (cover ID "Juan Diego Sanchez") |
| 2025-08-27 | Rocket.Chat server established on aim6umein3kee[.]com. Earliest messages. |
| 2025-08-28 | Henry directs James to build fake law firm domain (sokolovsky-law[.]com) |
| 2025-09-03 | Adrian orders 3CX PBX VPS in Netherlands for vishing phone system |
| 2025-09-05 | 3CX servers online: 87.251.67[.]222, 87.251.67[.]223 |
| 2025-11-12 | SPR_TRG_TALK channel created. Vishing operations begin. |
| 2025-11-24 | Adrian warns: "FBI has really gotten onto us." 2-month pause follows. |
| 2026-01-23 | Spectrum proposes card skimmers for building access |
| 2026-03-03 | Illinois operative (Jevan, 0026) caught |
| 2026-03-13 | HOE_BLACKMAIL created. Prostitution kompromat scheme launched. |
| 2026-03-15 | Steal_CLIENT created. Kidnapping operations planned. |
| 2026-03-21 | PUNISH_POWER_GROUP created. Armed enforcement unit organized. |
| 2026-04-04 | Henry details kidnapping plan: van, gun, fake HIV syringe |
| 2026-04-10 | REDACTED data leak reported on databreaches.net |
| 2026-04-10 | Fake_Employee channel created. Placement begins. |
| 2026-05-01 | Adrian lists defense targets: REDACTED, REDACTED, REDACTED, REDACTED |
| 2026-05-09 | DEEPFAKE_DATALOADING created. Deepfake Teams call plan. |
| 2026-05-13 | Henry meets Wagner Group veteran in person |
| 2026-05-20 | GAY_MARINES_PUBS created. Adrian orders naval base recon. |
| 2026-05-26 | target_list_naval_bases.xlsx last modified |
| 2026-05-29 | Adrian confirms: "The addresses are ready." XLSX completed. |
| 2026-05-04 | REDACTED FIRM GOLD $19M confirmed |
| 2026-05-23 | REDACTED FIRM $17M, REDACTED FIRM $11M, REDACTED FIRM $6M, REDACTED FIRM $3M GOLD in single day |
| 2026-05-29 | Baltics gun-transport idea floated via drone, called not needed |
| 2026-05-30 | REDACTED FIRM $17.5M GOLD, REDACTED FIRM $8M GOLD confirmed |
| 2026-06-27 | Adrian confirms active placement at REDACTED CYBERWARFARE COMPANY and REDACTED CYBERWARFARE COMPANY |
| 2026-09-02 | Secondary server activated. "Sleepless Threat" rebrand begins. |
| 2026-09-04 | Mike delivers 4 Google Drive exfil accounts, 2 SSH shells |
| 2026-08-05 | Henry posts [.]onion leak site URL |
| 2026-08-12 | REDACTED FIRM 2 targeting begins. Executive target list with 10 names compiled. |
| 2026-08-25 | REDACTED FIRM 2 CONTRACT $21M. REDACTED FIRM CONTRACT $1.004M. |
| 2026-08-26 | Mass vishing campaign: 15+ firms targeted simultaneously with dedicated GV numbers and Gmail accounts |
| 2026-09-02 | REDACTED FIRM first offer $5M. Same day: REDACTED FIRM $465K, REDACTED FIRM $500K, REDACTED FIRM$4M, REDACTED FIRM $500K. |
| 2026-09-21 | REDACTED FIRM GOLD $30M. Adrian: "RECORD GOLD BRO!" Adjusted to $31.25M for BTC rate. |
| 2026-09-22 | All agents migrate to Sleepless Threat brand with new OPSEC |
| 2026-09-24 | REDACTED FIRM $20M, REDACTED FIRM $10M, REDACTED FIRM $8M GOLD confirmed |
| 2026-09-23 | Henry researches NY military bases and drone manufacturers |
| 2026-09-23 | James purchases REDACTED INSURANCE and REDACTED INSURANCE access ($4,100 each) |
| 2026-09-24 | Stolen X/Twitter set up as ST PR: "like it's not us but it's us" |
| 2026-09-29 | Latest message in the export |
Busiest Individual Days
Aside from outlier events such as the GOLD record on 2026-05-04 and the complications with the Mexico operative on 2026-06-27, these “activity bubbles” would often occur during brainstorming sessions when the actors would bounce ideas off one another in rapid succession interspersed with jokes and commentary.
| Date | Messages | Dominant Room | Notes |
|---|---|---|---|
| 2026-03-13 | 312 | SPR_TRG_TALK | Violent escalation day. Kompromat, kidnapping, and armed rooms created. Dean joins. Spectrum lists their crimes. |
| 2026-09-02 | 259 | Main DM | Sleepless Threat rebrand kickoff, secondary server stood up. |
| 2026-05-01 | 216 | Main DM | Adrian names the defense targets, fake employee push. |
| 2026-09-24 | 170 | Main DM | Agents migrate to the ST brand, X/Twitter set up. |
| 2026-05-04 | 156 | Main DM | Internal accounting: 43.95 million dollars received here, GOLD confirmations. |
| 2026-06-27 | 134 | Main DM | Mexico operative stuck in Tijuana, Main channel is reported broken. |
| 2026-04-04 | 128 | Steal_CLIENT | Henry's full kidnapping plan outlined. |
| 2026-06-08 | 119 | Main DM | Mexico operative reaches Mexico City, Adrian frets about an FBI wire. |
November 2025 FBI Pause
On 2025-11-24, Adrian ordered a stop due to suspicion of FBI surveillance:
работать только с теми агентами что сейчас есть, FBI хорошенько взялось видимо за нас)
Translation: “work only with the agents we already have, the FBI has clearly gotten seriously onto us” Adrian, 2025-11-24
Adrian also flagged compromised chats, stating "чаты куда добавлены были FBI люди состоящие в нем автоматически считаются не надежными" (chats where FBI people were added, the members are automatically considered unreliable). December then went dormant. This matches the stated two-month pause.
June 2026 Collapse/Rebrand
Message volume dropped from 1,048 in May to 294 in June. The working-hours view flagged this as a possible pause or scare. The data now gives the cause, and it is mostly technical, not a raid.
The Main targeting channel broke. Henry, 2026-06-02:
Main is stalling due to spam related issues. We keep trying different options.
Henry, 2026-06-02
Key people went dark at the same time. Spectrum sent his last message on 2026-05-07, three weeks before the collapse. Agents went offline. Dean, 2026-06-26:
Jamal is offline! We will need to pay money to our agents, so they will work with us... such as XYZ and Mexico guy, who is going to cross the border
Dean, 2026-06-26
The collapse ran as a dead stretch of near-zero days from 2026-06-10 to 2026-06-25. It overlapped with the stalled Mexico crossing and steady FBI anxiety. Adrian, 2026-06-08, on the Mexico operative:
нужно... понять может он уже носит прослушку от фбр и позади два агента
(need to figure out whether he is already wearing an FBI wire with two agents behind him) Adrian, 2026-06-08
So the collapse was a broken Main channel, plus Spectrum and the agents going dark, during a stalled smuggling operation. It was not one scare event.
Operator Behavioral Heat Map
Keyword coverage scores each operator against eight functional themes. A message counts toward a theme when its text contains a stem from that theme. A message can match several themes, so rows do not sum to 100 percent. The interactive console is embedded below. Use the tabs for the topic profile, the specialization (lift) view, and the keyword groups.
Notes on Methodology
- The first pass used raw substring matching. That pass over-counted, because short Russian stems match unrelated words.
- The stem код matched QR codes, the stem крипт matched crypto-money, the stem тор matched тормозить, and the stem след matched следующий. A precision audit tightened the keyword set with word-boundary matching and removed the false-positive stems.
- The audit cut Development by 57 percent and OpSec by 62 percent. All numbers below use the cleaned set.
- Absolute coverage is low because most chat is operational narrative without these exact stems. The map shows relative emphasis, not share of total content.
Analytic Notes
- Henry sent the most messages and had an even spread across topics.
- He sent 59 percent of all messages, so his high raw counts are volume. His lift sits near 1.0 on most themes, with only a mild lean to Development (1.3). He touches every workstream and specializes in little.
- Adrian handles operational oversight, over-indexing across the board.
- His subject tilt is Law Enforcement awareness (2.1), then Exfiltration (1.7), Negotiation (1.6), OpSec (1.6), Money (1.5), and Management (1.4).
- James and Mike are access specialists.
- James lifts 11.4 on Access and 4.8 on Exfiltration. Mike lifts 18.8 on Access. Their message volume is small but concentrated on technical access, so lift makes them stand out where the raw share buried them.
- Spectrum’s field, physical, and vishing work is not captured by the standard financial and technical vocabulary.
- Initial analysis of his keyword use indicated inaccurate tilting that was corrected by a broader analysis of his general language.
- Finance stays with the leads.
- Adrian and Henry account for almost all Money and Management talk. No other operator registers on money.
Operator Topic Profile
Each cell is the share of that operator's own messages that touch the theme. This shows what each operator spends time on. It is evidence for a role, not an automatic role label. The strongest theme per operator is in bold.
| Operator | Money | Access | Dev | Negotiation | Exfil | Mgmt | OpSec | Law Enf |
|---|---|---|---|---|---|---|---|---|
| Adrian | 4.7 | 0.6 | 0.5 | 2.5 | 1.3 | 2.6 | 0.6 | 0.7 |
| Henry | 2.9 | 0.3 | 0.9 | 1.2 | 0.4 | 2.0 | 0.2 | 0.1 |
| Spectrum | 0.0 | 0.0 | 0.0 | 1.2 | 0.0 | 0.0 | 0.0 | 0.9 |
| James | 0.0 | 8.0 | 1.1 | 1.7 | 3.4 | 0.0 | 1.1 | 0.0 |
| Dean * | 4.3 | 0.0 | 0.0 | 4.3 | 0.0 | 4.3 | 4.3 | 0.0 |
| Mike * | 0.0 | 13.2 | 0.0 | 1.9 | 1.9 | 0.0 | 0.0 | 0.0 |
| Monty * | 0.0 | 0.0 | 0.0 | 0.0 | 0.0 | 0.0 | 0.0 | 0.0 |
Values are percentages. A star marks an operator whose row rests on single-digit message counts.
Specialization Profile
The topic profile above is confounded by volume. Adrian and Henry sent about 89 percent of all messages, so a raw share of any theme mostly measures who talks most. Lift removes that bias. For each operator and theme, lift is the operator's share of the theme divided by the operator's share of all messages. A value near 1.0 means the operator engages the theme as much as their volume predicts. A value above 1.0 means a real specialty. A value below 1.0 means they avoid it. A genuine specialty on a solid sample is in bold.
| Operator | Money | Access | Dev | Negotiation | Exfil | Mgmt | OpSec | Law Enf |
|---|---|---|---|---|---|---|---|---|
| Adrian | 1.5 | 0.9 | 0.7 | 1.6 | 1.7 | 1.4 | 1.6 | 2.1 |
| Henry | 0.9 | 0.4 | 1.3 | 0.7 | 0.5 | 1.0 | 0.6 | 0.4 ~ |
| Spectrum | 0 | 0 | 0 | 0.7 ~ | 0 | 0 | 0 | 2.8 ~ |
| James | 0 | 11.4 | 1.5 ~ | 1.1 ~ | 4.8 | 0 | 3.1 ~ | 0 |
| Dean * | 1.4 ~ | 0 | 0 | 2.7 ~ | 0 | 2.2 ~ | 11.8 ~ | 0 |
| Mike * | 0 | 18.8 | 0 | 1.2 ~ | 2.6 ~ | 0 | 0 | 0 |
| Monty * | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 |
Capability by Operator
| Operator | Vishing | Kompromat | HUMINT | Fake Emp | Weapons | Fake IDs | Kidnap |
|---|---|---|---|---|---|---|---|
| Adrian | 38 | 7 | 13 | 6 | 2 | 7 | 2 |
| Henry | 38 | 11 | 11 | 12 | 14 | 9 | 10 |
| Spectrum | 8 | 6 | 0 | 0 | 0 | 0 | 2 |
| James | 0 | 0 | 0 | 0 | 0 | 0 | 0 |
| Dean | 1 | 0 | 0 | 0 | 0 | 0 | 0 |
| Mike | 0 | 0 | 0 | 0 | 0 | 0 | 0 |
| Monty | 0 | 0 | 0 | 0 | 0 | 0 | 0 |
Group Theme Totals
| Theme | Messages | Percentage of chats |
|---|---|---|
| Money | 178 | 3.1% |
| Management | 111 | 2.0% |
| Negotiation | 90 | 1.6% |
| Development | 43 | 0.8% |
| Exfiltration | 41 | 0.7% |
| Access | 40 | 0.7% |
| OpSec | 21 | 0.4% |
| Law Enforcement | 18 | 0.3% |
Domain Mentions
These are the domains the operators type into messages. The primary server tops the list with 575 hits, all from pasted room links (477 of them are /direct/ message references).
Show table (14 rows)
| # | Count | Domain | Type |
|---|---|---|---|
| 1 | 575 | aim6umein3kee[.]com | Primary server (pasted links) |
| 2 | 62 | gmail.com | Burner mail |
| 3 | 34 | hotmail.com | Burner mail |
| 4 | 24 | chatgpt.com | OSINT tool |
| 5 | 19 | redacted | Victim law firm |
| 6 | 17 | redacted | Victim law firm |
| 7 | 16 | rocket.chat | Platform |
| 8 | 15 | slplsskdj2836v2jjsx[.]com | Secondary server |
| 9 | 11 | redacted | Victim law firm |
| 10 | 11 | redacted | Victim law firm |
| 11 | 11 | redacted | Victim law firm |
| 12 | 10 | zoominfo.com | OSINT tool |
| 13 | 8 | drive.google.com | Exfiltration staging |
| 14 | 8 | t.me | Telegram |
The list below the server is almost entirely victim law firm domains, burner mail providers, and exfiltration infrastructure. The presence of chatgpt.com at number four confirms the group used ChatGPT as a research tool.
Top Operational Terms
These are the group's most-used working terms.
Show table (15 rows)
| # | Term | Count | Meaning |
|---|---|---|---|
| 1 | брат | 190 | brother |
| 2 | бро | 128 | bro |
| 3 | братик | 102 | little brother |
| 4 | offer | 81 | extortion offer stage |
| 5 | partner | 70 | law firm partner (target) |
| 6 | fakelab | 63 | the document forger |
| 7 | officer | 60 | law firm or target role |
| 8 | data | 58 | stolen data |
| 9 | agents | 47 | field agents |
| 10 | jamel | 46 | relayed contact (one name) |
| 11 | сша | 45 | USA |
| 12 | xyz | 44 | the fake ID maker |
| 13 | gold | 39 | closed and paid deal |
| 14 | мейн / main | 40 | main targeting |
| 15 | кош | 68 | wallet (BTC) |
What the Vocabulary Shows
- The three most common terms are forms of the word “brother”: брат (190), бро (128), and братик (102). Together these are about 420 brother address forms. The group runs on a fraternal, trust-based tone.
- The top terms map straight to the attack lifecycle: “Offer” and “gold” are the extortion pipeline, “partner”, “officer”, and “law” are the targeting of senior law firm staff, “agents”, “fakelab”, and “xyz” are the field agent and forgery apparatus, and “data”, “отправил”, and “кош” are exfiltration and payment.
- Operators write English tradecraft terms in Cyrillic: мейн (main), трг (targeting), айди (ID), кош (wallet).
- кош (wallet) appears in 68 messages, far ahead of any spelling of btc. This matches the finance-centralized picture from the heat map.
- The name "Jamel" appears 46 times at the token level and 93 times as a person reference. He is a major external fixer who bridges forgery, smuggling, and cash-out and the volume of messages containing his name show he was a major part of the operations.See the People Network section.
Chat Room Directory
Server Footprint
The primary Rocket.Chat server is the single most common string in the whole dataset. It sits in the metadata of every message on that server, and operators also paste the full server link when they share a room.
| Server | Messages | Role |
|---|---|---|
aim6umein3kee[.]com | 5,458 | Primary Rocket.Chat |
slplsskdj2836v2jjsx[.]com | 234 | Secondary (Sleepless Threat) |
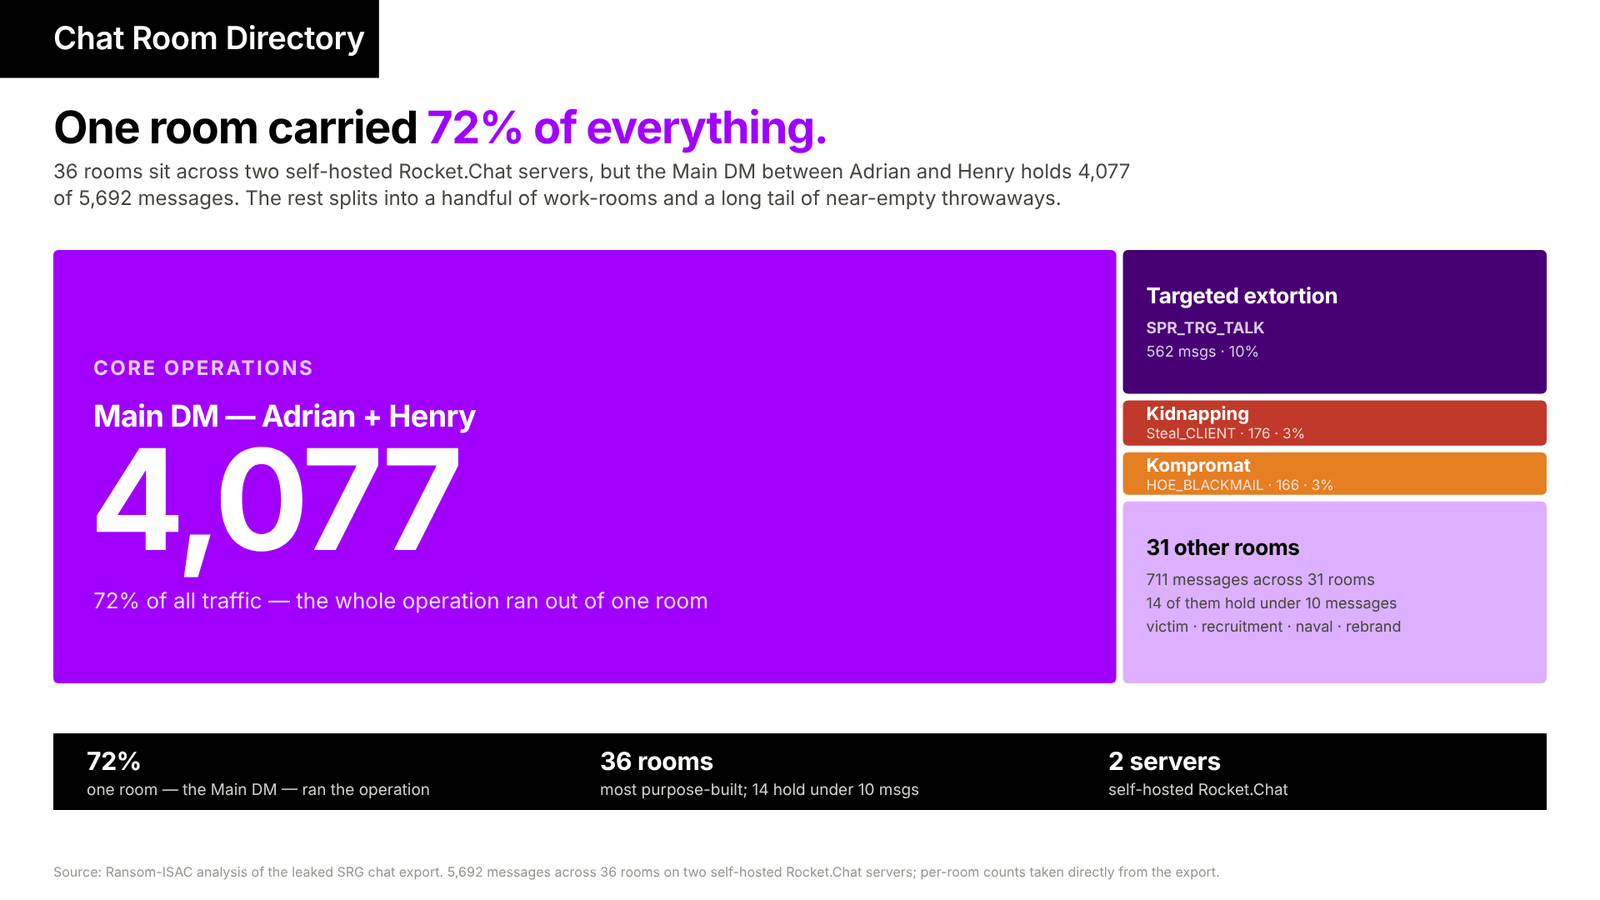
Chat Room Directory: one room carried 72% of everything.
Show table (27 rows)
| Room | Msgs | Period | Users | Purpose |
|---|---|---|---|---|
| Main DM | 4,077 | Aug 25 to Sep 26 | Adrian, Henry | Strategic coordination |
| SPR_TRG_TALK | 562 | Nov 25 to Jun 26 | Adrian, Dean, Henry, Spectrum | Vishing + physical infiltration |
| Steal_CLIENT | 176 | Mar to Jul 26 | Adrian, Dean, Henry, Spectrum | Kidnapping planning |
| HOE_BLACKMAIL | 166 | Mar 26 | Adrian, Dean, Henry, Spectrum | Sextortion / kompromat |
| James+Mike DM | 102 | Sep 26 | James, Mike | Sleepless Threat rebrand |
| James+Monty DM | 79 | Sep 26 | James, Monty | OPSEC + X/Twitter |
| Henry+James DM | 71 | Aug to Sep 25 | Henry, James | Fake domains setup |
| Adrian+James DM | 68 | Aug 25 to May 26 | Adrian, James | C2 + 3CX PBX |
| PUNISH_POWER_GROUP | 56 | Mar 26 | Adrian, Dean, Henry, Spectrum | Armed enforcement |
| Fake_Employee | 54 | Apr to May 26 | Adrian, Henry, Spectrum | Insider infiltration |
| Adrian+Spectrum DM | 38 | Nov 25 to Mar 26 | Adrian, Spectrum | Field coordination |
| FAKE_CLEANER | 32 | Mar to Jul 26 | Adrian, Henry, Spectrum | Physical infiltration |
| ARMA_PARTNERSHIP | 24 | Apr to May 26 | Adrian, Henry | Fake defense contractor SE via Zoho portals (REDACTED) |
| LEX_0044_NY | 21 | Mar to May 26 | Adrian, Henry, Spectrum | NY operative |
| [REDACTED]_CHAT | 19 | Sep 26 | James, Monty | Victim: REDACTED FIRM |
| PRIVATE_INVESTIGATOR | 18 | May to Jun 26 | Adrian, Dean, Henry | Counter-surveillance |
| [REDACTED]_CHAT | 17 | Sep 26 | James, Monty | Victim: REDACTED FIRM |
| GAY_MARINES_PUBS | 14 | May to Jul 26 | Adrian, Henry | Naval HUMINT targeting |
| DAVID_0037_LA | 14 | Mar 26 | Adrian, Henry, Spectrum | LA operative |
| general | 13 | Aug 25 to Sep 26 | All | Announcements |
| FAKE_CLIENT | 12 | Mar to May 26 | Adrian, Henry, Spectrum | Client impersonation |
| TRG_GIRLS_LOVE_OLDIES | 10 | Jun to Jul 26 | Adrian, Henry | Honey trap: female operators + prostitutes for kompromat |
| VAN_SPR | 9 | Mar to May 26 | Adrian, Henry | Work van infiltration |
| DEEPFAKE_DATALOADING | 9 | May 26 | Adrian, Henry | Deepfake video calls |
| [REDACTED]_LOADING | 8 | Sep 26 | James, Monty | Victim: REDACTED FIRM |
| JEVAN_0026_IL_CAUGHT | 7 | Mar to Apr 26 | Adrian, Henry | IL operative (caught) |
| [REDACTED]_EMAIL | 2 | Sep 26 | James | Victim: REDACTED INSURANCE AGENCY |
Assessment
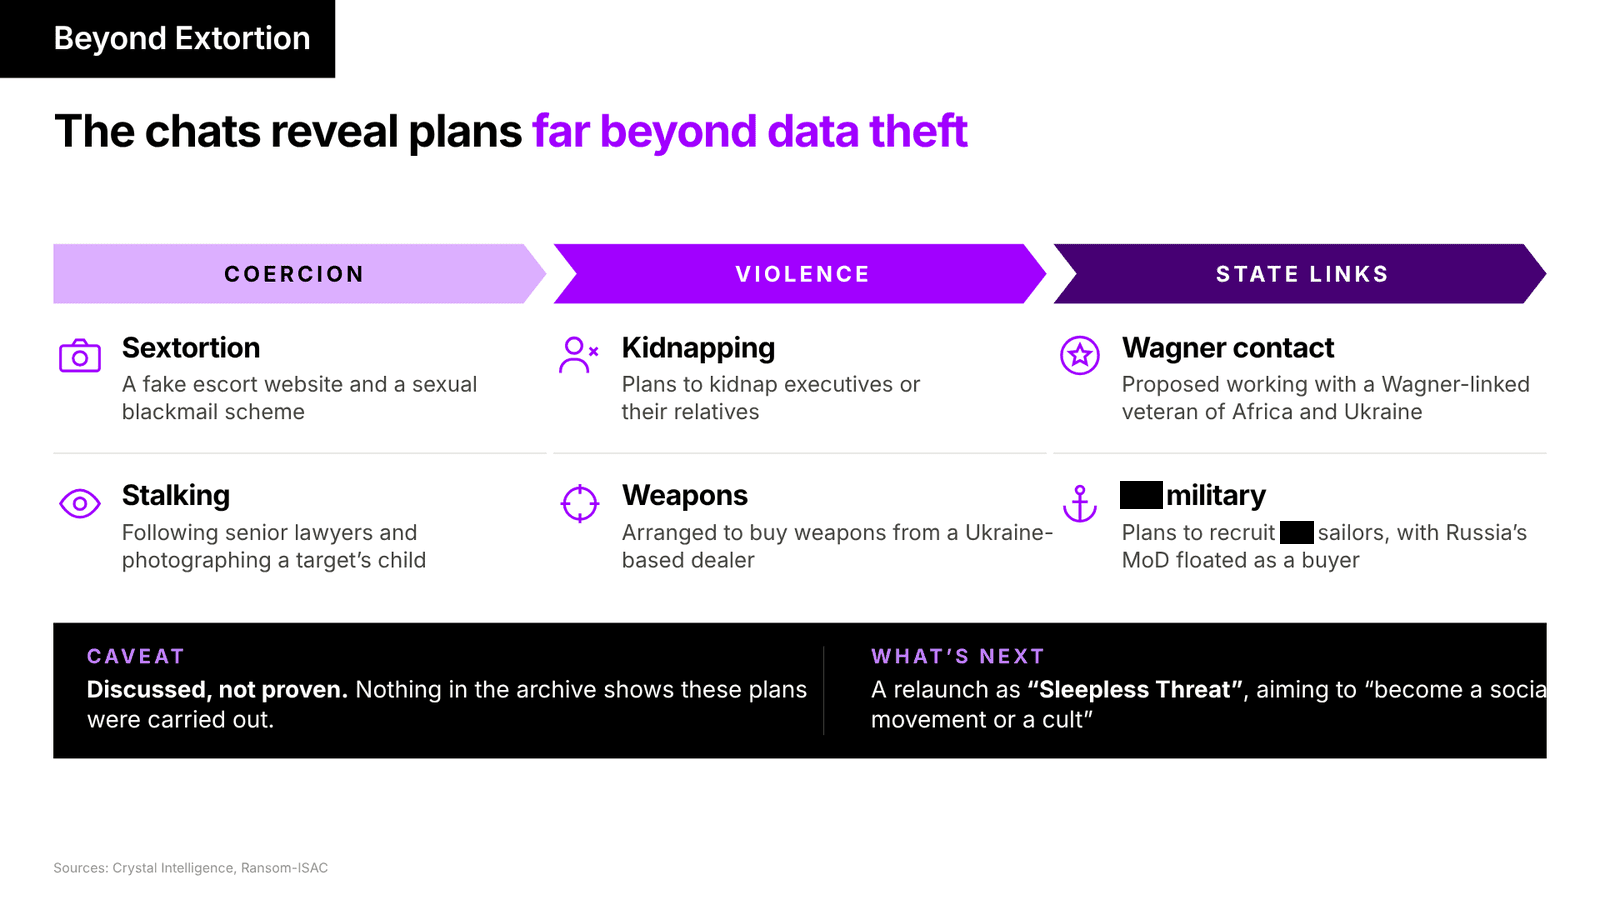
Escalation summary. Three details on this slide come from Crystal Intelligence, not from the leaked chat: the fake escort website, the photographing of a target's child, and Russia's MoD as a buyer for sailor intelligence.
This operation is a hybrid criminal-espionage threat. It escalated over 13 months. The group started with law firm data extortion. It then expanded into six additional areas:
- Military espionage targeting the [REDACTED] nuclear submarine deterrent
- Defense contractor infiltration (REDACTED CYBERWARFARE COMPANY, REDACTED, REDACTED, REDACTED)
- Physical violence (kidnapping, armed enforcement)
- Intelligence tradecraft (kompromat, deepfakes, fake identities)
- HUMINT recruitment near military installations
- Prostitution-based blackmail of law firm partners
Reading the threats of violence and escalation:
- Much of the register is performance. The chat runs on bravado and an anti-American pose, so some "plans" sit closer to venting than to operational steps. Weight each claim by its artifacts, not by how loudly it is stated.
- But not all of it is talk. The naval target spreadsheet, the fake resume, and the on-chain extortion payments are real artifacts. The rhetoric around them may be posturing. The artifacts are not.
The group is Russian-speaking with a KyivBTC financial nexus. It operates a network of 10 to 15 US-based field agents. One recruit was moved toward the US via Mexico, but the crossing is not confirmed. Others arrived on work visas. The group is aware of FBI attention.
Their September 2026 rebrand to "Sleepless Threat" with new infrastructure, OPSEC hardening, and continued victim negotiations shows that the operation is ongoing and adapting.
The group calls itself "Silent Ransom Group" in press coverage on databreaches.net. It uses callback phishing (vishing) as a primary initial access vector. This is consistent with public reporting on the group also tracked as Luna Moth / Callback Phishing. The military targeting, physical operations, and Wagner Group connections are a significant escalation beyond previously documented activity.
OpSec Analysis
The group is disciplined on paper and sloppy in practice. The actors understand operational security in theory, but don’t execute well in practice. The disparity between the two is documented below:
Security Practices
- Ephemeral and encrypted comms: The actors use Privnote for one-time secrets, whereas victims are forced onto ProtonMail followed by SimpleX.
- James to REDACTED FIRM 4, 2026-09-04: "We're giving you until Tuesday to figure out how simpleX works."
- Clean-wallet discipline
- Adrian, 2026-02-20: "смотри что бы чистый кош был что бы никак не были связаны старые моенты с теми что я сейчас отправлю" (”make sure it is a clean wallet, so the old coins are not linked to the ones I send now”.)
- Rebrand: New domains and the Sleepless Threat name change.
- James, 2026-09-02: "размыть наше сходство с SRG" (”dilute our resemblance to SRG”).
- Kit rotation: New laptops and new Telegram accounts for the second season.
- Monty, 2026-09-22: "i will tell noah to buy a new laptop and make new tg."
- Counter-surveillance: The PRIVATE_INVESTIGATOR room successfully hired New York detectives to surveil agents and to identify the ID maker xyz.
- Henry, 2026-06-09: "i think we found xyz."
- FBI controls: Adrian treated any chat that had FBI members added as unreliable and ordered a two-month pause.
- Adrian, 2025-11-24: "FBI хорошенько взялось видимо за нас" (”the FBI has clearly gotten onto us”).
Failures
- Plaintext credentials in chat. Server, VPN, and cloud credentials sit in the messages. Mike, 2026-09-04 pasted SSH root logins for two servers. All of it is now in the leak.
- Wallet reuse. The clean-wallet rule failed on the receive side. The On-Chain section shows Angela's wallet with 79 deposits, Henry's salary wallet with 19, and the December 2025 payments forming a peel chain back to one CoinJoin source.
- The leak itself. The full internal Rocket.Chat corpus, every credential and wallet, was dumped to a Tor site.
- Single-channel concentration. One Main DM room carried 4,077 messages, so one dump exposed the entire strategic record.
Room-by-Room Analysis
Main DM: Adrian + Henry (4,077 messages)
The primary command channel. This room spans 13 months and covers every part of the operation.
Law Firm Extortion
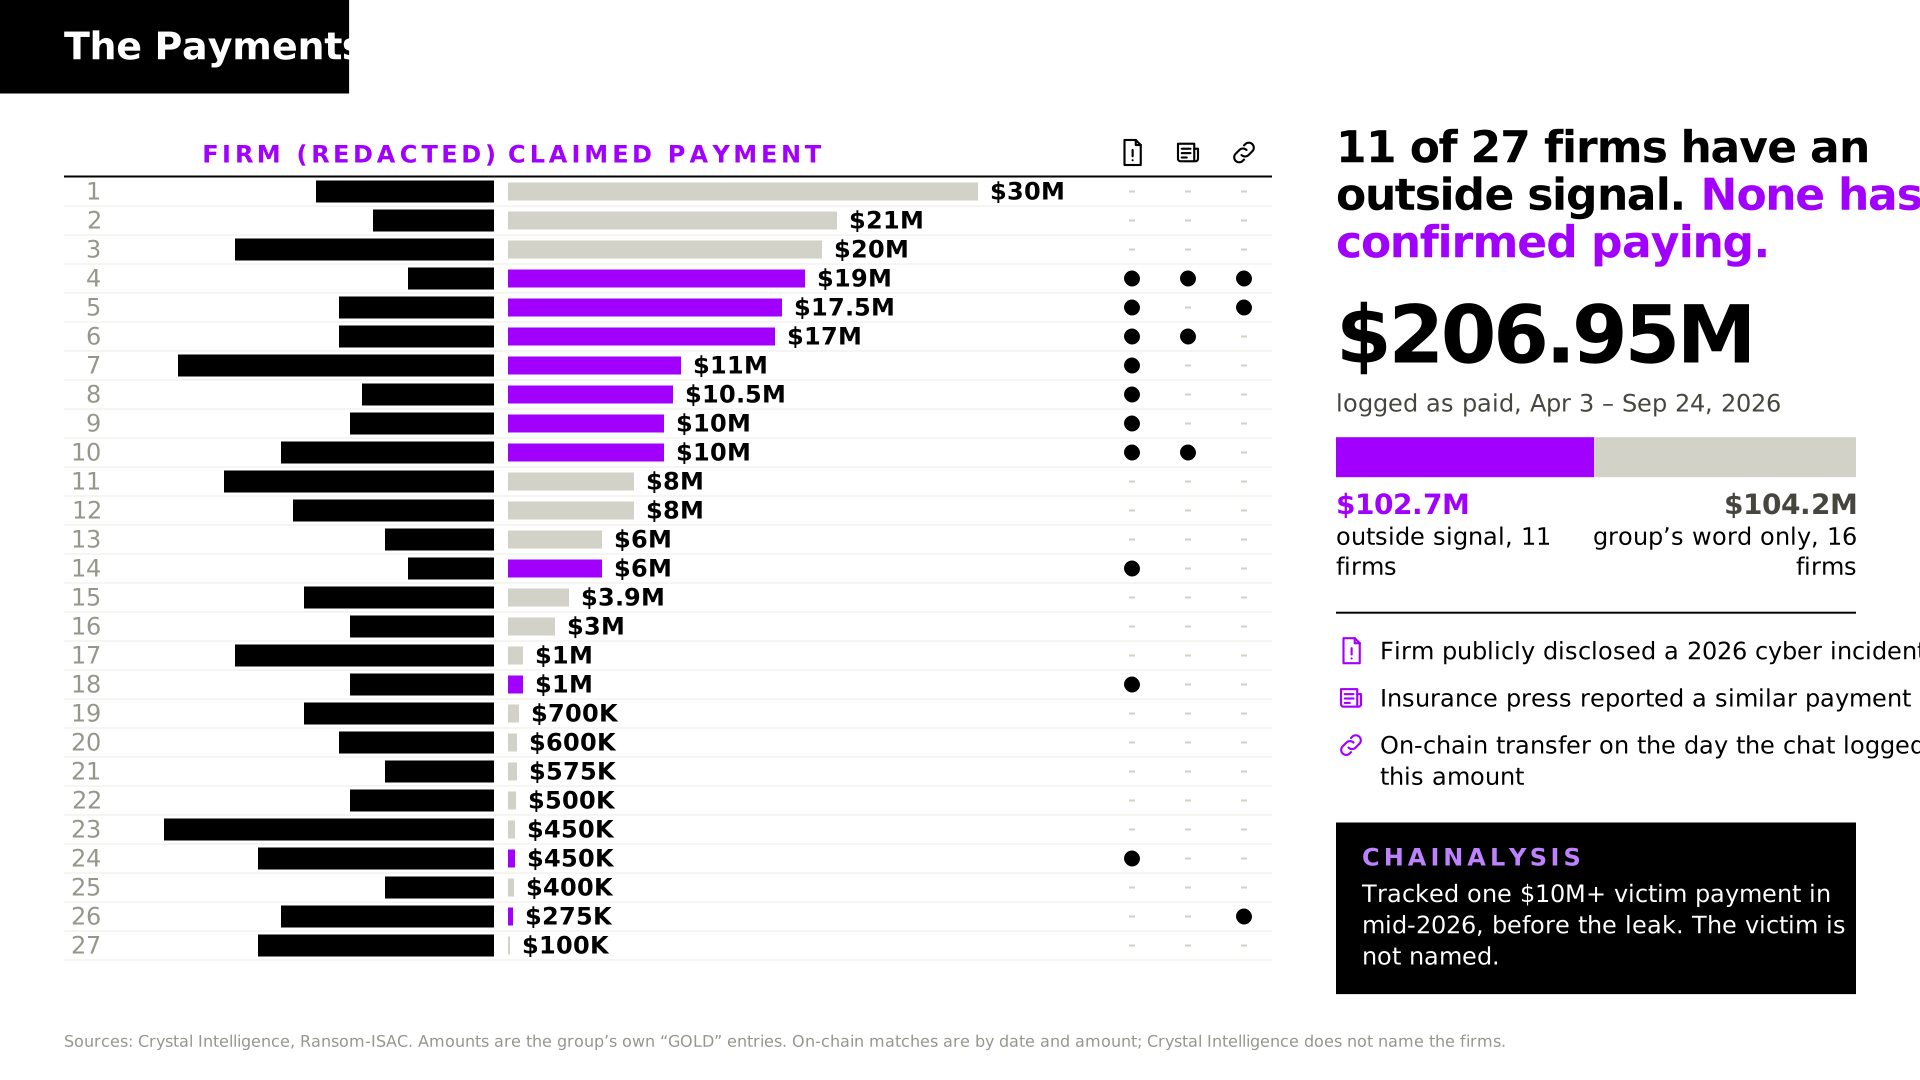
The 27 GOLD entries against outside signals. The $43.95M received figure above comes from the group's own accounting. No victim firm has admitted a payment in public. Outside signals come from Crystal Intelligence.
Data theft and ransom is the group's core revenue stream. The group steals corporate data via vishing and AnyDesk, then demands payment in BTC.
Total known ransom demands confirmed paid (GOLD): ~$206,950,000 across 27 victim organizations.
Show table (40 rows)
| Target Firm | Status | Amount | Date |
|---|---|---|---|
| REDACTED | GOLD | Escalated: $5M → $9.365M → $18.73M → $30M GOLD (adjusted to $31.25M for BTC rate) | Sep 21 |
| REDACTED | GOLD | $21,000,000 | Aug 26 |
| REDACTED | GOLD | $20,000,000 | Sep 24 |
| REDACTED | GOLD | $19,000,000 | May 04 |
| REDACTED | GOLD | $17,500,000 | Jun 08 |
| REDACTED | GOLD | $17,000,000 | May 23 |
| REDACTED | GOLD | $11,000,000 | May 23 |
| REDACTED | GOLD | $10,500,000 | May 29 |
| REDACTED | GOLD | $10,000,000 | May 01 |
| REDACTED | GOLD | $10,000,000 | Sep 24 |
| REDACTED | GOLD | $8,000,000 | Jun 08 |
| REDACTED | GOLD | $8,000,000 | Sep 24 |
| REDACTED | GOLD | $6,000,000 | Apr 30 |
| REDACTED | GOLD | $6,000,000 | May 23 |
| REDACTED | GOLD | $3,900,000 | Apr 30 |
| REDACTED | GOLD | $3,000,000 | May 23 |
| REDACTED | CONTRACT | $1,500,000 | May 30 |
| REDACTED | CONTRACT | $1,004,000 | Aug 25 |
| REDACTED | GOLD | $1,000,000 | May 15 |
| REDACTED | GOLD | $1,000,000 | May 13 |
| REDACTED | GOLD | $700,000 | Apr 08 |
| REDACTED | GOLD | $600,000 | Apr 20 |
| REDACTED | GOLD | $575,000 | Apr 07 |
| REDACTED | GOLD | $500,000 | Apr 24 |
| REDACTED | GOLD | $450,000 | Apr 13 |
| REDACTED | GOLD | $450,000 | Apr 21 |
| REDACTED | GOLD | $400,000 | May 01 |
| REDACTED | GOLD | $275,000 | Apr 03 |
| REDACTED | GOLD | $100,000 | Apr 17 |
| REDACTED | Offer | $2,000,000 | Sep 02 |
| REDACTED | Offer | $550,000 | Feb 17 |
| REDACTED | Offer | $1,000,000 | Jun 08 |
| REDACTED | Offer | $465,500 | Sep 02 |
| REDACTED | Offer | $500,000 | Sep 02 |
| REDACTED | Offer | $4,000,000 | Sep 02 |
| REDACTED | Offer | $140,000 | Feb 13 |
| REDACTED | Active | $450,000 | Sep 26 |
| REDACTED | Active | $250,000 | Sep 26 |
| REDACTED | Loading | TBD (staging) | Sep 26 |
| REDACTED | Active | TBD | Sep 26 |
Terminology: GOLD = payment received. CONTRACT = agreement to pay. SPOOF = caller spoofed identity. SPYCO = James's custom tool used for the attack.
РЕКОРДНЫЙ ГОЛД БРАТ! ДАВАЙ КОШИК
(RECORD GOLD BRO! GIVE ME THE WALLET) Adrian, on the REDACTED FIRM $30M target
The group leaked REDACTED data publicly. Adrian references their own press coverage on databreaches.net.
Financial Operations
- BTC payments: 50+ unique wallet addresses for salary, ransom, and agent payments
- RUB withdrawal: Via "KyivBTC." "надеюсь Kyivbtc работает все еще на вывод руб"
- Henry salary: $1,500 per month
- Agent "Z" salary: $10,000 to $15,000 per month
- a female operative: $1,500 via Zelle
- Fake document lab: $3,400
- SpyCo: Custom tool built by James. Adrian references "у SPYCO первый CONTRACT 3.000.000" ($3M contract)
- Targeting directive: "берем в счет только UK и US" ("We only count UK and US")
Rebrand: SRG to Sleepless Threat (September 2026)
In September 2026 the group renamed itself. James wrote the reason in chat:
нужно разбавить наше сходство с SRG
(Need to dilute our resemblance to SRG) James, 2026-09-02
Key details of the rebrand:
- Considered domains:
sleepless[.]co($18,410),ThreatActorsNeverSleep[.]com,sleeplessthreat[.]com - All agents (except "Flash") migrate to the ST brand
- New laptops ($1,500 each) and new Telegram accounts for OPSEC separation
- The group set up a stolen X/Twitter account as a PR channel with plausible deniability
like it's not us but it's us)
James, on the X/Twitter strategy
SPR_TRG_TALK: Vishing and Physical Infiltration (562 messages)
The operational room for "super targeting." This room combines phone vishing with physical building infiltration. It manages a network of 10 to 15 field agents in the US. The agents are coordinated via Telegram.
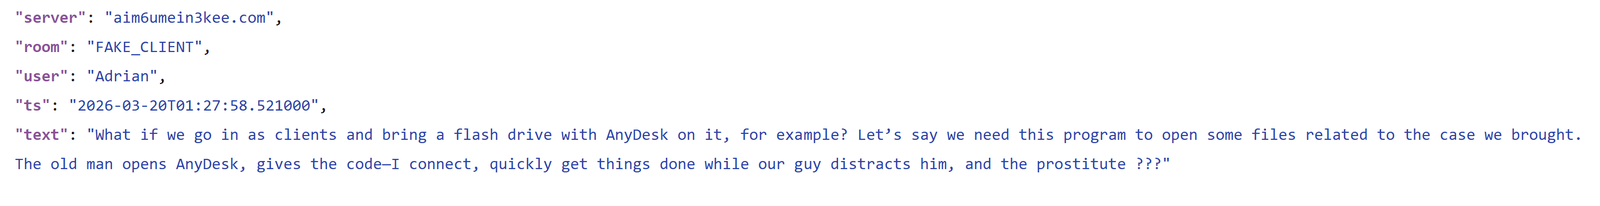
Translated chat log from Adrian suggesting methodology for infiltration scam.
Agent Network
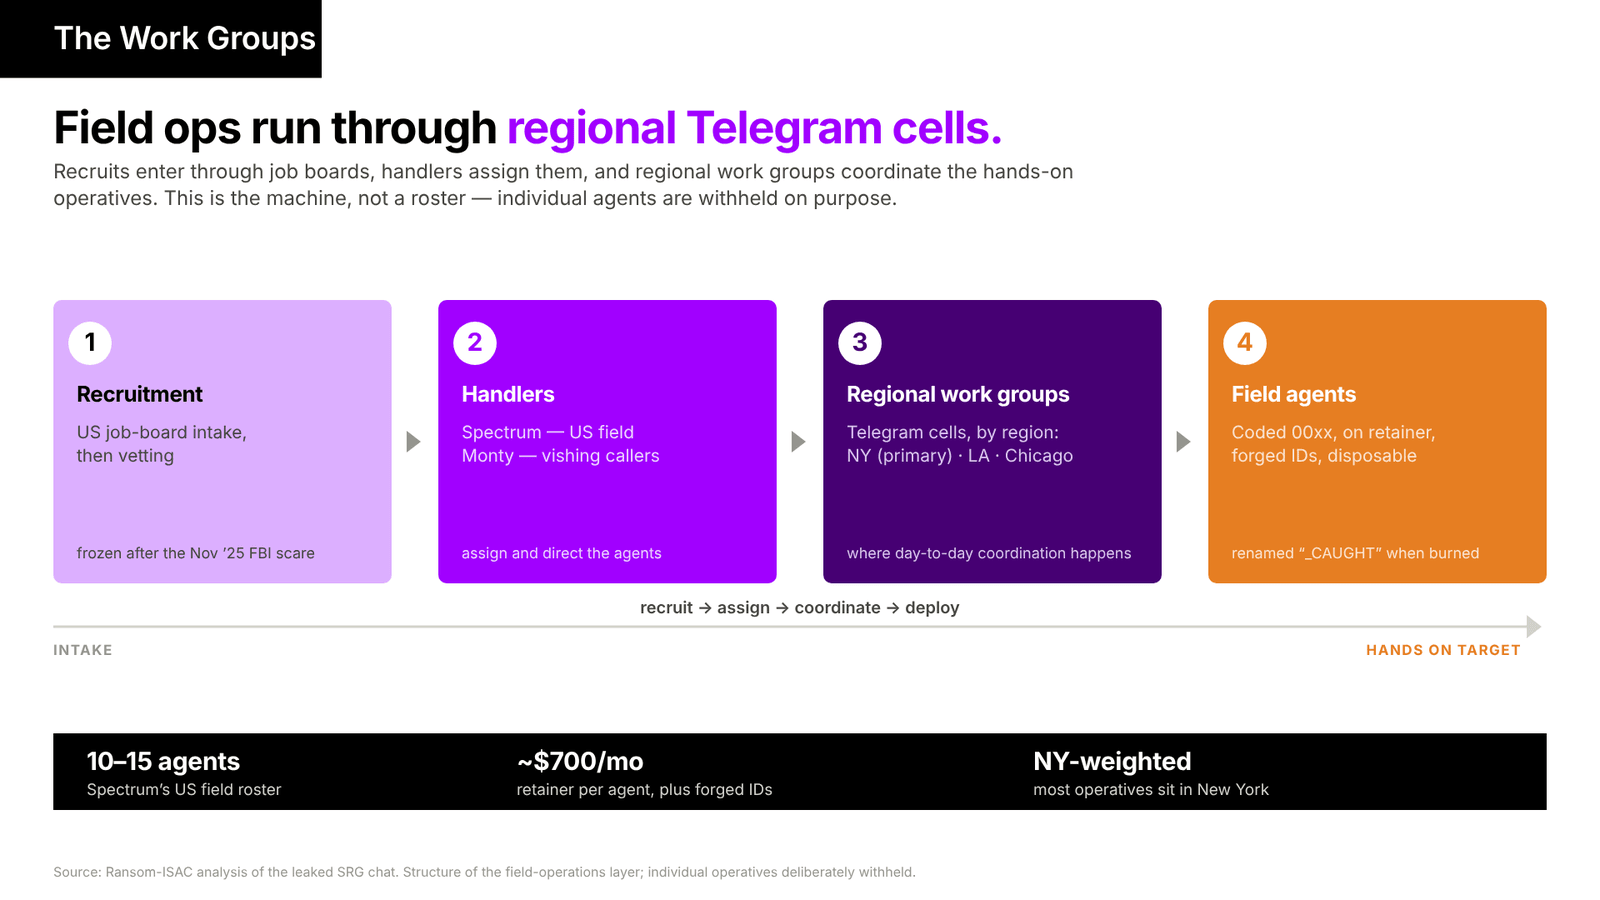
The Work Groups: field ops run through regional Telegram cells.
The field layer runs as a separate operation from the command chat. Where Adrian and Henry coordinate strategy, finance, and extortion in the Rocket.Chat servers, the hands-on work (building access, card skimming, scouting, and the physical-coercion tasks) is pushed down to US-resident agents who are organised into regional work groups and run over Telegram.
Two operators run this layer: Spectrum handles US field operations directly, and Monty manages the vishing callers. Dean sits upstream of both as the recruiter, sourcing and vetting new agents. The separation is deliberate: the people giving orders and the people carrying them out sit on different platforms, which is why the leaked command chat exposes the leadership in full but leaves the field roster largely in the dark.
Recruitment feeds the work groups through US-facing job adverts, after which candidates pass through a vetting step before they are trusted with tasks. The pipeline is not continuous. After the group came to believe the FBI had taken an interest in late November 2025, hiring froze.
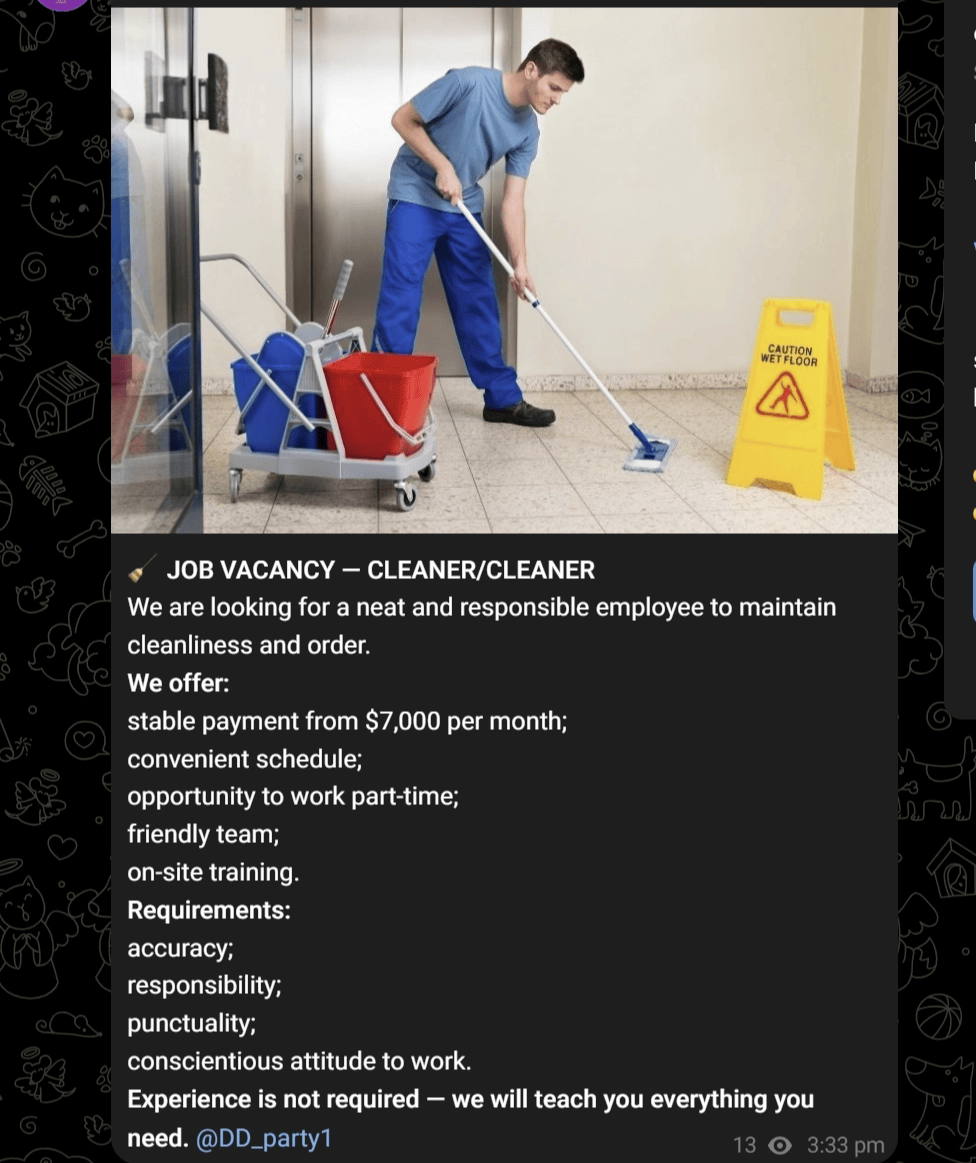
A cleaner job advert posted on Telegram by @DD_party1.
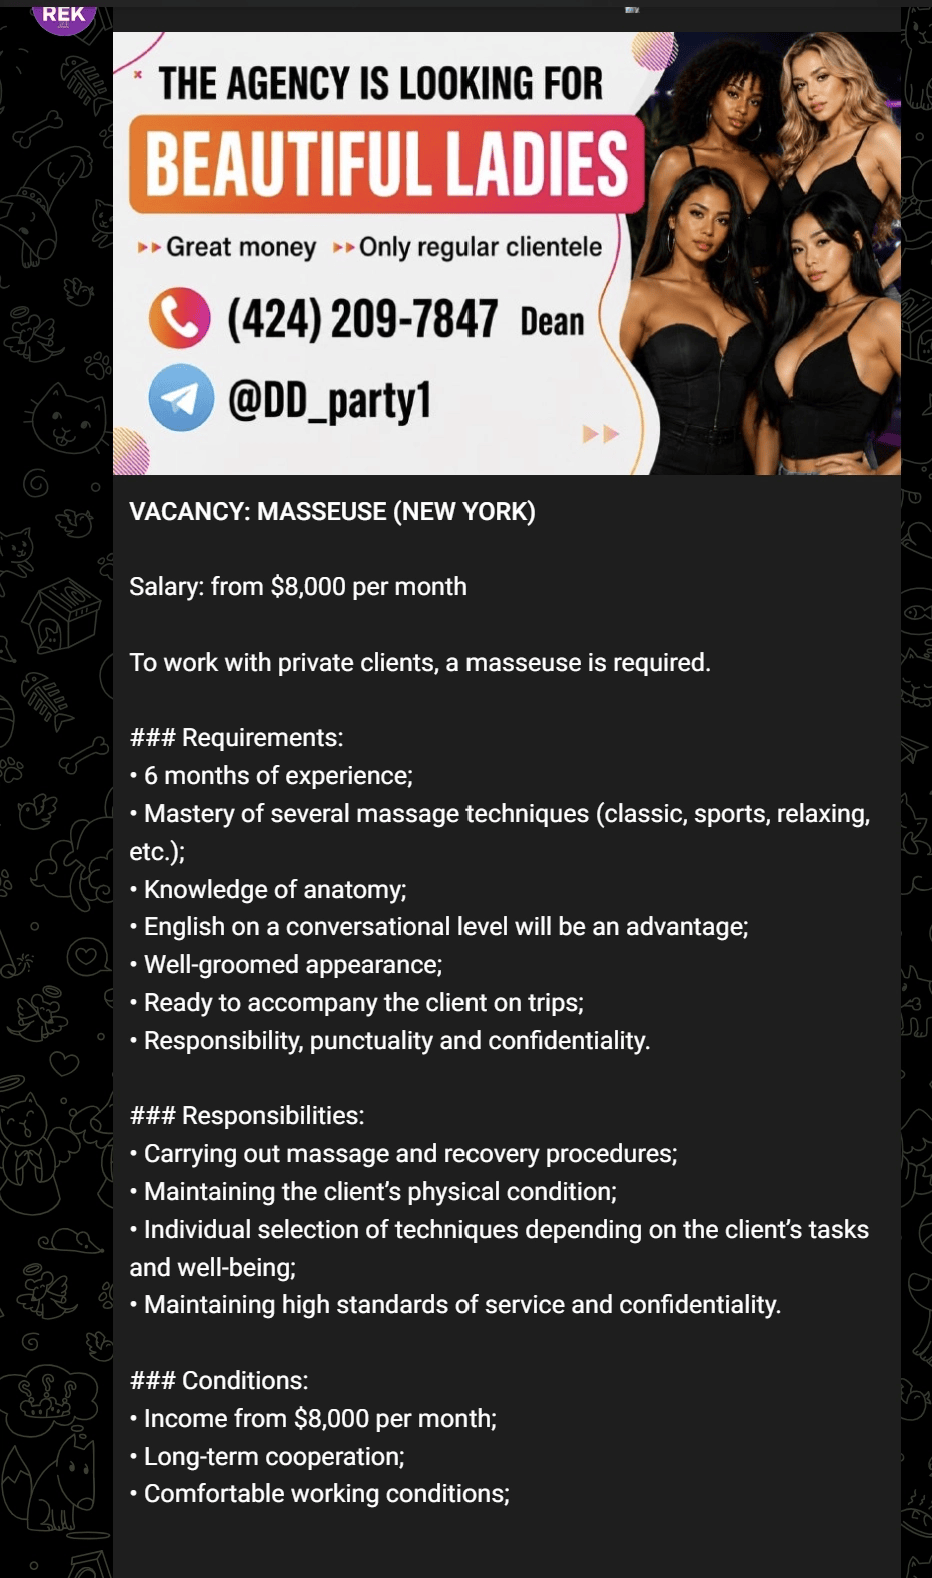
Screenshots of job listings believed to be used for agent recruitment, made by @DD_party1, the account linked to the SRG chat.
The operation’s own OpSec reflexes show in how it handles a compromised agent: when one was believed burned, the associated channel was renamed with a “_CAUGHT” tag rather than quietly retired. Spectrum’s own estimate put the field roster at roughly ten to fifteen agents, including those still under vetting.
The agents themselves are treated as interchangeable and disposable. They operate under numeric codenames rather than names, draw a retainer of about $1,500 a month, and receive forged identity documents from the group’s document vendor to support cover identities and physical access. The footprint is weighted toward New York, which holds the largest concentration of operatives, with smaller presences in Los Angeles and Chicago. This is a logistics model, not a loyalty one: agents are paid to be present and compartmentalised enough that losing one, to arrest or to distrust, costs the operation a channel rename rather than the operation itself.
For analysts, the significance is less about any individual and more about the shape. The command layer concentrates knowledge and money in a handful of people, while the field layer is broad, regional, and deliberately kept at arm’s length on a separate platform. That design is why the on-chain and chat evidence is rich on leadership and thin on the operatives: the work groups were never meant to touch the servers that leaked. The numbered groups and their membership live in the Telegram side of the operation, outside this export, and are not reconstructed here.
- Agents receive fake IDs from maker xyz (Telegram:
xyz000zz) - Agent codenames: Terror, Ali, Spartak, Lex (0044), David (0037), Jevan (0026)
- Agents receive a $1500 per month retainer to keep them from leaving
- One agent was recruited from Sochi, Russia and moved toward the US via Mexico. The crossing is not confirmed.
- Colombian agents arrived via work visa and are stationed in New Jersey
The Trusted and the Disposable
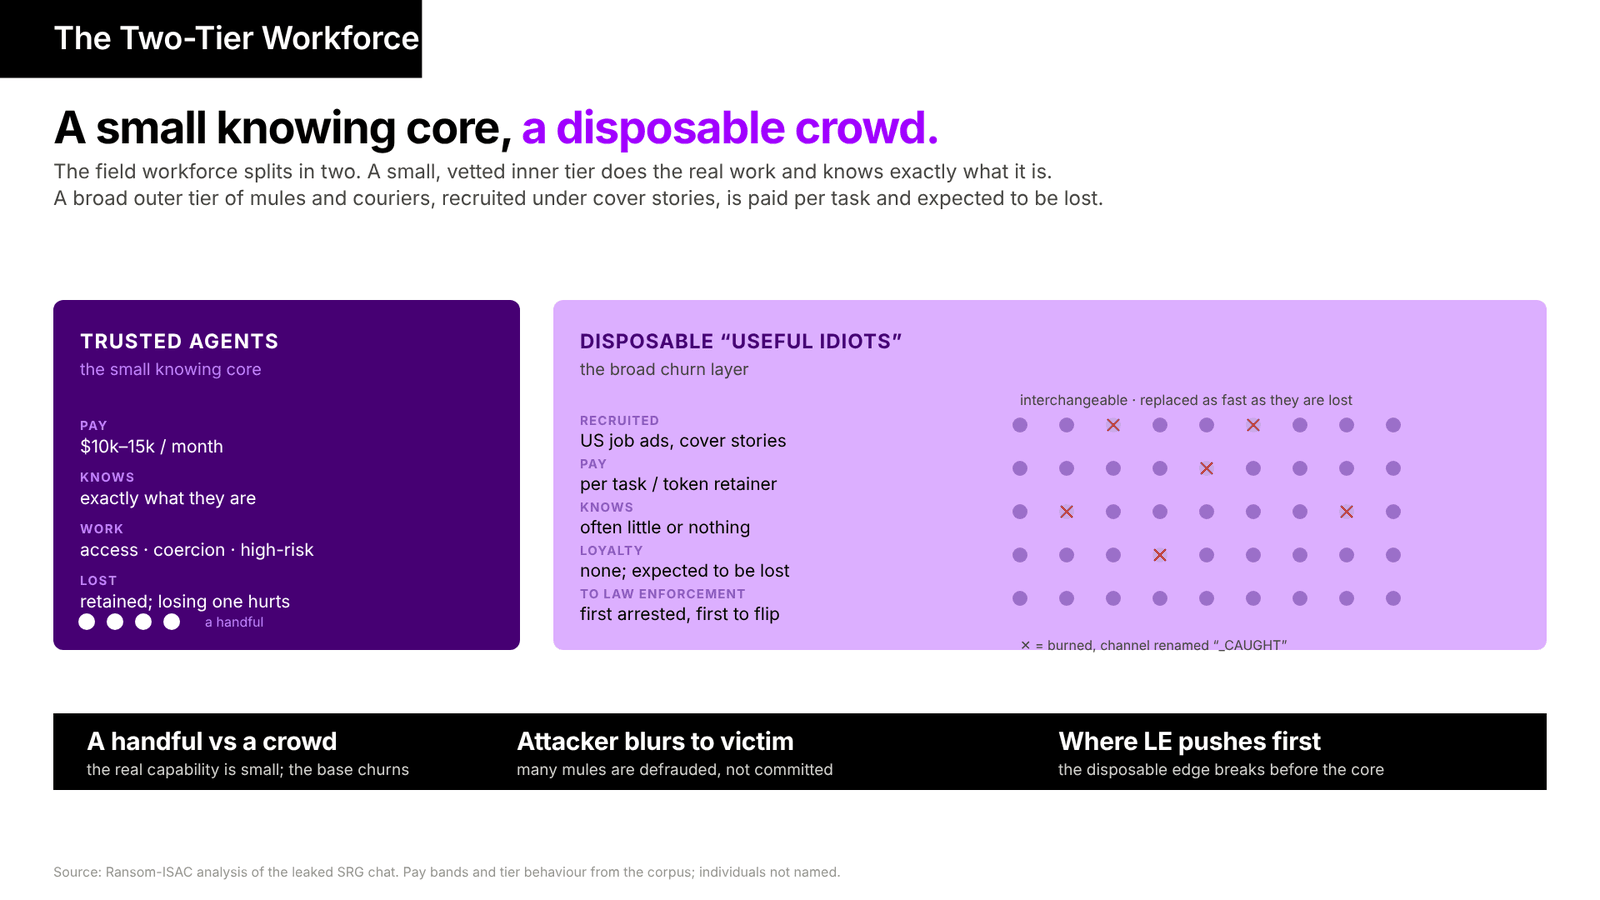
The Two-Tier Workforce: a small knowing core, a disposable crowd.
The field workforce divides into a trusted inner tier and a disposable outer one, and the group recruits, pays, and treats the two in entirely different ways.
At the top sit the agents the operation actually relies on: vetted, knowingly complicit, and paid accordingly. The clearest case is the operative the chat calls Agent Z, taken on under explicit terms at $10,000 to $15,000 a month. These are the people trusted with the sensitive, high-risk work: building access, the coercion tasks, anything that would collapse the operation if it went wrong. They know exactly what they are part of, they hold codenames and forged identities, and their retention matters to the group.
Below them is a churn layer of disposable labour: money mules, reshipping couriers, and one-off field bodies pulled off US job boards under cover stories. A courier advert offering a few hundred dollars a day to “deliver equipment,” or a vague payment-processing role, is not hiring a criminal. It is harvesting a useful idiot. Many in this tier do not know, or do not allow themselves to know, that they are moving extortion proceeds or servicing a ransomware crew. They are paid per task or on a token retainer, they are interchangeable, and they are expected to be lost, whether to arrest, to distrust, or simply to walk away. When one is burned the group renames a channel and moves on, such as in the case of the operative Jevan, who was caught in Chicago.
The distinction matters for two reasons. Operationally, the disposable tier is the group’s soft edge: the people most exposed, least loyal, and most likely to be the first arrested or the first to cooperate, which makes them the natural entry point for law enforcement rather than the core. Analytically, it is also the tier where attacker blurs into victim. A mule recruited under a false pretext may be closer to a defrauded participant than a committed member. That ambiguity is exactly why the lower tier is best understood as a population and a recruitment pattern, not catalogued as a list of named individuals. Many of them may not even know whose side they are on.
Profile of a Useful Idiot
The “useful idiot” is not persuaded into the operation, rather they are selected for a systemic weakness or one of character and then exploited by the threat group. The recruiting pool is narrow: almost none are American, with the group sourcing from the Russian-, Ukrainian- and Georgian-speaking diaspora in the US, who are approached in their own language, and within that pool a recruit almost always fits one of four profiles. Some fit two at once, which makes them easier still to turn.
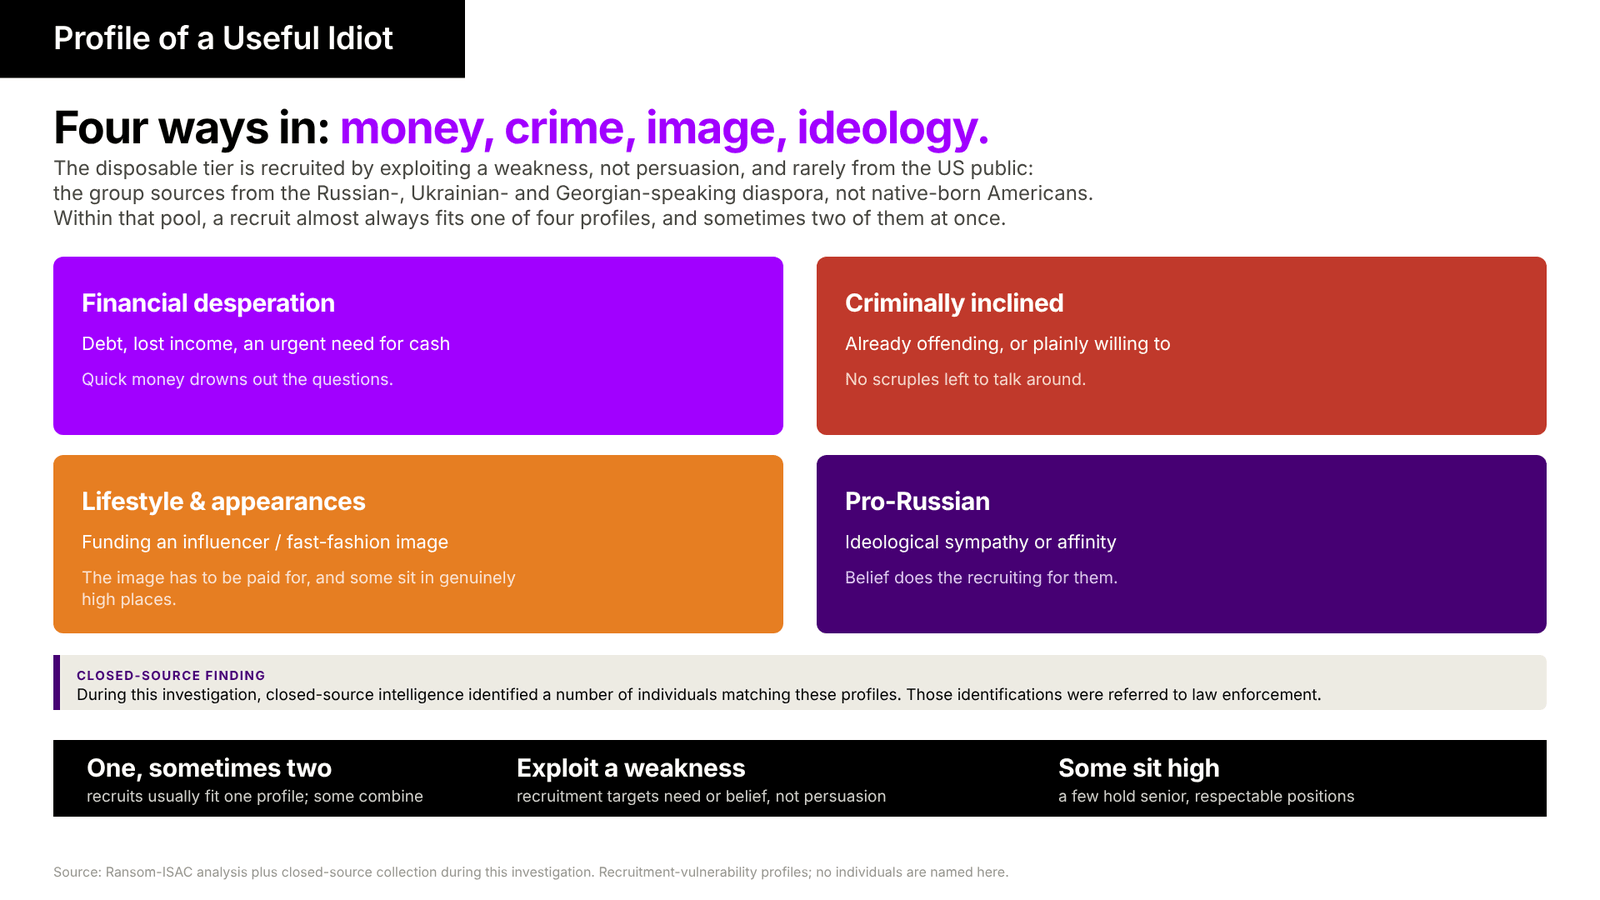
Profile of a Useful Idiot: four ways in, money, crime, image, ideology.
Financial desperation: The most common profile is simple need. Debt, lost income, or a sudden bill creates urgency, and the group offers fast cash for tasks that sound harmless: a courier run, a payment to forward, a package to collect. The desperation does the work the recruiter would otherwise have to. It drowns out the obvious questions about who is paying and why. These recruits rarely ask what they are part of, because asking risks the money.
Criminal Tendencies/History: These recruits may have a record, an existing hustle, or simply no objection to illegal work when it pays. For them, there is nothing to talk around. The group does not need a cover story so much as a rate. They are quicker to deploy and more willing to take physical risk, but they are also less controllable and more likely to freelance or skim.
Lifestyle and Image: These are people funding a visible lifestyle, often in creative, influencer, or fast-fashion circles, where the appearance of money has to be maintained whether or not the money is real. The group’s payments subsidise the image. What makes this profile notable is that some of the people in it are not marginal at all. A number sit in genuinely respectable or senior positions, which is exactly what makes them useful and what makes them hard to spot.
Pro-Russia: Recruits with a pro-Russian outlook, whether political, cultural, or personal, require no financial hook and little persuasion. They treat the work as a contribution rather than a job. This profile is smaller but more committed, and it blurs the line between the disposable tier and the trusted one, since ideology can earn a recruit more responsibility over time.
Closed-source finding. During this investigation, closed-source intelligence identified a number of individuals matching these profiles. None were of American origin. Those identifications were referred to law enforcement. Consistent with the treatment of the disposable tier throughout this report, they are not named here.
Physical Infiltration Methods
Card Skimmer. Buy card skimmers and send an agent to steal employee access cards from law firm workers. "we buy card skimmer, we send terror agent to steal cards for us from someone in that corp" (Spectrum, 2026-01-23)
Pizza Delivery Cover. Buy Dominos uniforms and insulated bags. The agent enters a building as a delivery driver, changes clothes in the bathroom, and poses as IT staff to steal data.
HVAC Technician Cover. Use HVAC maintenance access to enter major office buildings. Henry notes that this grants access to most corporate buildings.
Work Van. Buy a company work van at auction and copy the branding. Agent "OJ" (TG: MoeSolnce1010) uses it to access Manhattan towers.
Spy Glasses. Buy glasses with hidden cameras for agents to record inside law firm offices.
FBI Awareness
FBI хорошенько взялось видимо за нас
(FBI has really gotten onto us) Adrian, 2025-11-24
This warning led to a 2-month operational pause. Adrian ordered the group to stop recruiting and use only trusted agents.
now we have fraud, prostitution, tresspassing, and using illegal imigrants
Spectrum, 2026-03-13, listing their own crimes
Steal_CLIENT: Kidnapping Operations (176 messages)ShowHide
This room contains detailed planning to kidnap lawyers and corporate employees. The purpose is to force data extraction.
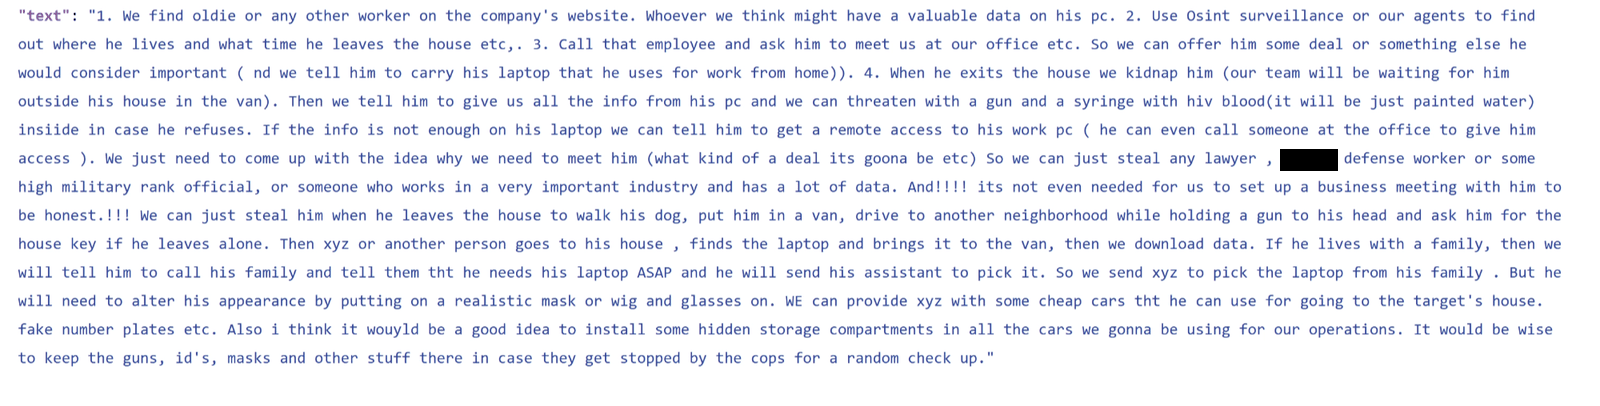
Translated message from “Henry” from 2026-04-04 detailing a kidnapping proposal.
Henry's Kidnapping Plan (2026-04-04)
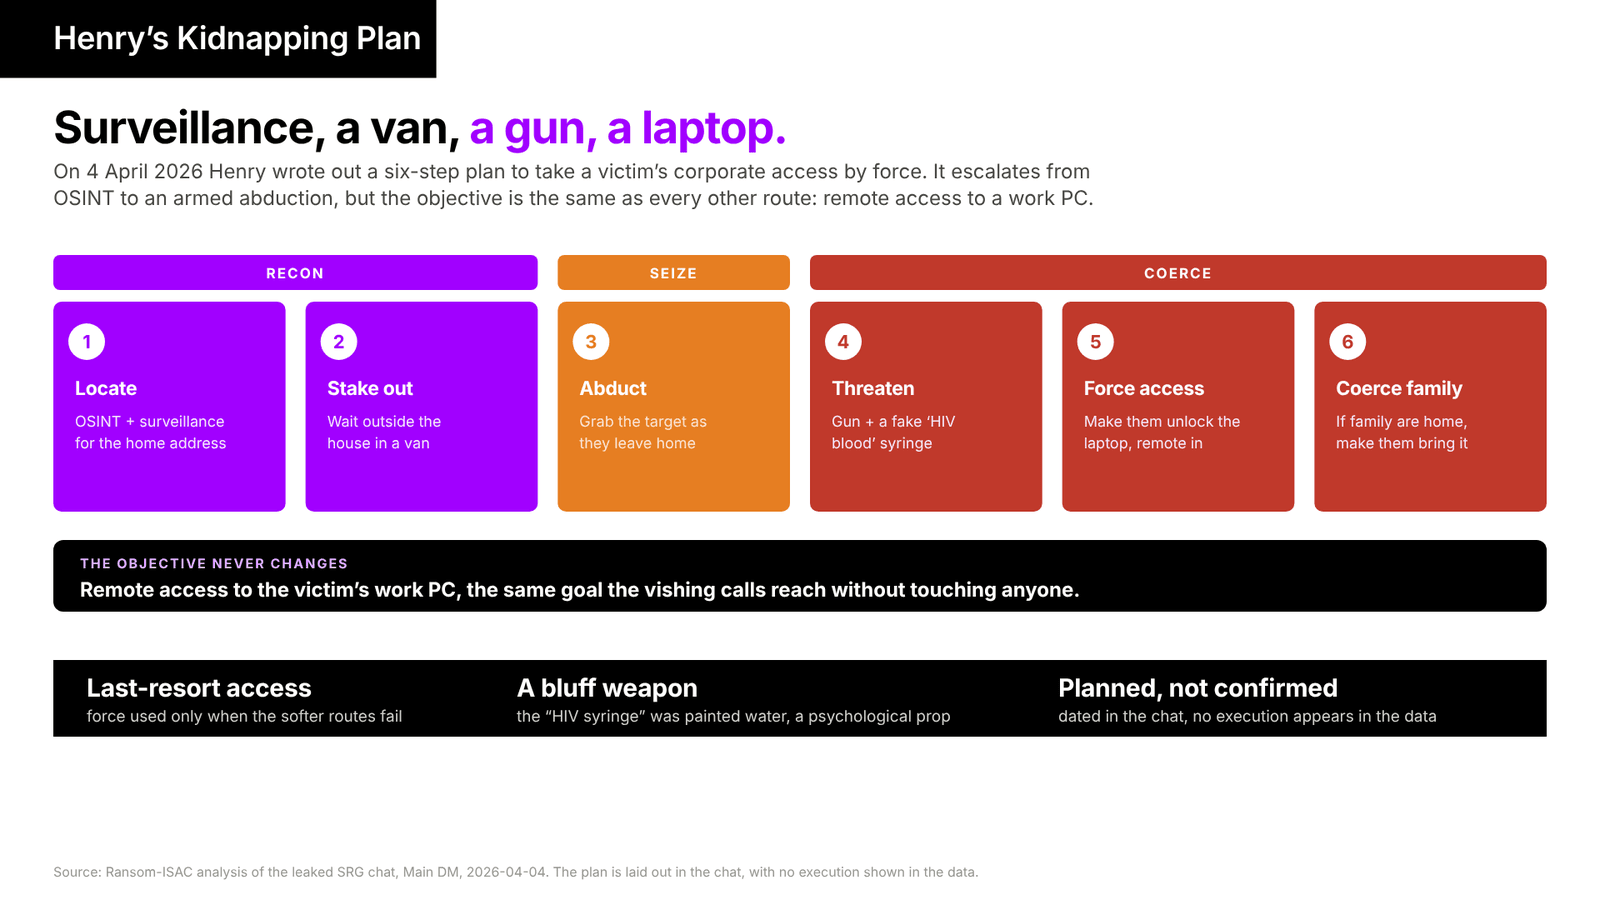
Henry's Kidnapping Plan: surveillance, a van, a gun, a laptop.
- Use OSINT and surveillance to find the target's home address
- Wait outside the house in a van
- Kidnap the target when they leave
- Threaten the target with a gun and a "syringe with HIV blood" (actually painted water, a psychological weapon)
- Force the target to unlock their laptop and give remote access to their work PC
- If the target lives with family, force them to call the family to bring the laptop
Recruitment and Targets
- Lex recruits muscle in Harlem
- Henry contacted someone with Wagner Group (Russian paramilitary organization) connections (he met a Wagner member who fought in Africa and Ukraine)
- Dean posted a job listing: $50,000 per kidnapping
- Named targets: lawyers, REDACTED AVIATION/DEFENSE workers, "high military rank officials"
we aint gonna stop till we destroy america
Spectrum
the ultimate goal is to become a social movement or a cult so americans believe in our idea and steal important data for us without being asked
Henry
Operative Infiltration: The Mexico Route
The group moved a recruited operative from Russia toward the United States through Mexico. The route is traceable step by step. Most of it is confirmed as executed. The US border crossing is the one step the data does not confirm.
The Recruit
Henry identified the operative on 2026-05-06 in the Steal_CLIENT room: "found a guy from sochi)", to be moved "through mexico", and noted "he is in armenia for work now." The operative is a Russian national from Sochi, staged in Armenia.
The Smuggling Plan
Henry relayed a four-step plan on 2026-05-06:
1. летит в мексику 2. добирается до тихуанны на границе 3. пересечет границу нелегально 4. начнет работать в сша на нас
(1. flies to Mexico 2. reaches Tijuana at the border 3. crosses the border illegally 4. starts working in the USA for us) Henry (relayed), 2026-05-06
The plan names the method for the crossing: "наша задача найти койотов которые перевезут через границу" (our task is to find coyotes to carry him across the border). The group planned to use human smugglers, not a cartel partnership.
The Document Pipeline (FAKELAB)
The forger FAKELAB set the exit route and the papers. Henry relayed the consult on 2026-05-14:
Из рф только по внутреннему пасу в Армению / На чужие данные / От туда по заграну дальше
(out of Russia on an internal passport to Armenia, on someone else's identity, then onward on a foreign passport) FAKELAB (relayed by Henry), 2026-05-14
FAKELAB described this as the same route used to move draft evaders: "Сво так вывожу" (this is how I move the war-draft cases out). The route ran Smolensk to Minsk to Yerevan. On 2026-05-29 FAKELAB priced premium documents at "1200$ с доставкой" (1,200 dollars with delivery), sewn into real diplomas and shipped by express courier.
FAKELAB forgery price list. UV-security photos of blank Russian passports with prices. Internal passport on a real blank 4000 USD, with a donor identity cloned from databases and full backstopping. SNILS 200 USD. Foreign passport 3500 to 4500 USD. This is the document pipeline behind the smuggling route.
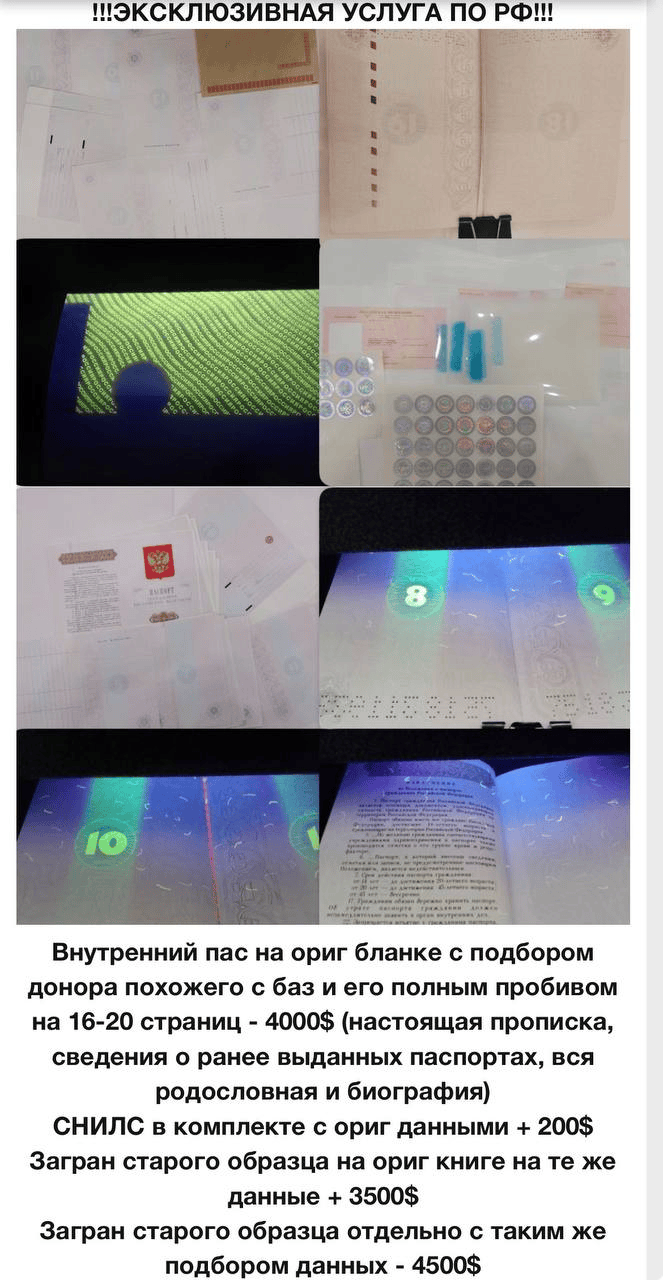
FAKELAB's forged-document price list, recovered from the chat.
The Journey (Confirmed Steps)
| Date | Step | Evidence |
|---|---|---|
| 2026-05-21 | Ticket bought | Henry: "bought ticket to mexico for our agent from Ru" |
| 2026-06-08 | Arrived in Mexico City | Henry: "он доехал на них из армении до гостиницы в мехико" (he traveled on the documents from Armenia to a hotel in Mexico City) |
| 2026-06-27 | Moved to Tijuana | Henry: "он пошел через тихуанну" (he went via Tijuana) |
| 2026-06-27 | Crossing stalled | Henry: "русских нету уже в тихуанне. все поуезжали после того как трамп отменил убежище" (no Russians left in Tijuana, they all left after Trump cancelled asylum) |
A San Diego pickup to New York was the next planned step. Henry, 2026-05-14: "хуз встретит его в сан диего после перехода границы... и отвезет в нью йорк" (will meet him in San Diego after the border crossing and drive him to New York). The data does not confirm the operative entered the US.
Colombian Agents (Separate, Confirmed Arrival)
A separate group entered the US on work visas. Henry, 2026-05-21: "several guys from COLOMBIA arrived to the usa... by Monday they will be headed to the house in NEW JERSEY." These operatives arrived legally and moved to a New Jersey safehouse. This route is separate from the Mexico smuggling.
Wagner Transport Idea (Aspirational)
Henry discussed moving Wagner Group mercenaries to the US via Mexico after he met a Wagner veteran who fought in Africa and Ukraine. This is an idea in chat, not a confirmed operation.
On the Cartel Claim
The chat contains two offhand wishes about cartels. Spectrum, 2026-03-13: "work with mexican cartels for human trafficking through panama jungle." Henry, 2026-04-13: "надо какимто образом дать идею о важности инфы какимто челам из картелей" (somehow pitch the value of the data to cartel guys). Neither wish led to action. The real smuggling relied on coyotes and the FAKELAB document pipeline.
HOE_BLACKMAIL: Prostitution-Based Kompromat (166 messages)ShowHide
This room describes a scheme to blackmail law firm partners. The method uses prostitution and hidden cameras.
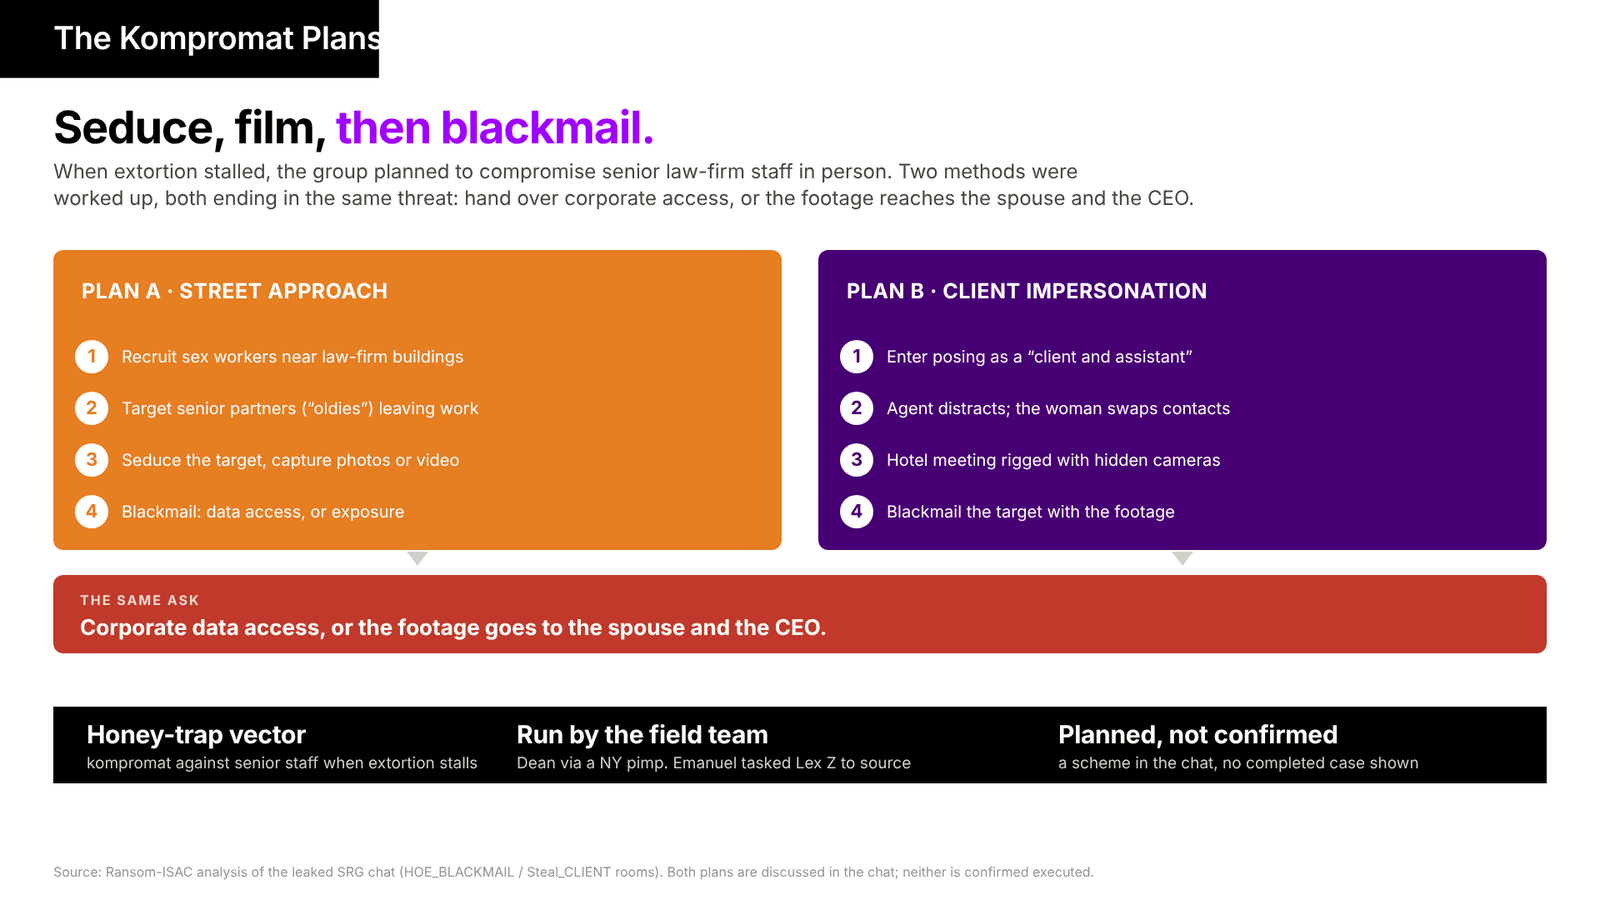
The Kompromat Plans: seduce, film, then blackmail.
Plan A: Street Approach
- Recruit prostitutes near law firm buildings
- Target senior lawyers ("oldies") as they leave work at end of day
- The prostitute seduces the target and obtains compromising photos or video
- Blackmail: provide corporate data access or face exposure to spouse and CEO
Plan B: Client Impersonation
- Send an agent and an attractive woman to a law firm as a "client and assistant"
- The agent distracts while the woman flirts and exchanges contacts with a partner
- Arrange a hotel meeting with hidden cameras
- Blackmail the target with the footage
Проститутка в конце рабочего дня караулит у билдинга... Далее знакомится берет контакт... ведем до момента получения компромата... связываемся и говорим что у нас есть на него
(Prostitute waits at building at end of work day... Gets acquainted, gets contact... We lead to the moment of getting kompromat... We contact and say we have something on him) Adrian
Dean contacted a pimp in New York for recruitment. Emanuel asked "Lex" to find street prostitutes in NY.
TRG_GIRLS_LOVE_OLDIES: Honey Trap Kompromat (10 messages)ShowHide
A scheme that combines female vishing operators with prostitution for blackmail:
- Female operators call senior law firm employees ("oldies").
- The operator flirts with the target during the call. If vishing fails, she escalates to a personal meeting.
- Hire a prostitute in the US to meet the target at a motel room with hidden cameras.
- Film the encounter.
- Blackmail: hand over all company data or the video goes to the CEO.
the girl operator flirts with oldie, tries to make him get us SUCCESS. Then if he refuses, continue flirting and set up a date
Henry, 2026-06-02
Adrian endorsed the scheme for law, military, and "other super important operations." Henry was assigned to find operators and prostitutes in the US.
Status: Active as of July 2026.
PUNISH_POWER_GROUP: Armed Enforcement (56 messages)ShowHide
Internal enforcement squad. The purpose is to control agents and punish defectors.
- Adrian proposes arming 5 people with Glocks (real or fake)
- Spectrum suggests recruiting Mexicans as muscle
- Plan: follow agents in secret, find home addresses, threaten or beat those who scam the group or go to the FBI
- Weapons sourced from the Ukrainian black market
- Henry mentioned a contact who could move guns from Russian border regions to the Baltics, possibly by drone. He called it expensive and not needed at the time, and it was not acted on. Separately, the group discussed an air-dropped weapons cache in a forest in Ivano-Frankivsk oblast, Ukraine
Fake_Employee: Insider Placement (54 messages)ShowHide
This room explains the fake_employee_resume.pdf file. The group runs a plan to place its own people inside US companies as hired employees. The goal is long-term access from the inside, for theft without a traditional network breach.
Placement Plan
Henry sets out the full plan on 2026-04-10:
We find some people with good english (can be anywhere). Tell them to apply for remote jobs in american companies. If they get a job, we tell them to infiltrate deeper and try to get the info. We make them fake documents and even diplomas or fake linkedin profiles to get employed. They will be getting double salary (from us and from the company), and a good bonus if they succeed in getting companies info.
Henry, 2026-04-10
Proposed Methodology
- Fake credentials: The group makes fake diplomas, certifications, and LinkedIn profiles. Spectrum, 2026-04-10: "if we can fake diplomas... we can get jobs in big firms as paralegals etc."
- Interview readiness: Henry, 2026-04-10: "the employee will have to be ready to go through video interviews in zoom several times a day."
- Role selection: Spectrum noted that senior roles check experience and citizenship. He steered the plan toward remote low-level roles such as IT help desk. Spectrum, 2026-05-03: "i think if we hook people who are in usa would be better."
The North Korea Template
The group copies a known state model. Henry, 2026-04-13: "i heard of north koreans infiltrating usa organizations pretending to be south koreans." On 2026-05-01 he pasted a full news article about North Korean IT workers who take remote jobs at large firms under fake identities to steal data and fund the state. This is the documented template the group follows.
Targeting
Adrian set the target list on 2026-05-01 in the Fake_Employee room:
скажем устраивайтесь в топ фирмы по accounting или law firms или REDACTED, REDACTED, REDACTED, REDACTED?
(get hired at top accounting firms or law firms, or even REDACTED, REDACTED, REDACTED, REDACTED?) Adrian, 2026-05-01
The named defense contractors are top US aviation and military production companies. The group also pursued two technology firms. Adrian, 2026-06-27: "Fake_Employee (устраиваем сейчас в REDACTED CYBERWARFARE COMPANY и REDACTED CYBERWARFARE COMPANY)" (we are currently getting placed into REDACTED CYBERWARFARE COMPANY and REDACTED CYBERWARFARE COMPANY).
On 2026-09-23 Adrian narrowed the keep-list to REDACTED CYBERWARFARE COMPANY and REDACTED CYBERWARFARE COMPANY and wrote "очень важно устроить туда кого нибудь" (very important to get someone placed there).
Confirmed and Not ConfirmedShowHide
Confirmed: the recruitment doctrine, the double-salary model, the North Korea template, the fake resume artifact, and an active leadership-directed campaign to place operatives in REDACTED CYBERWARFARE COMPANY and REDACTED CYBERWARFARE COMPANY from June to September 2026.
Not confirmed: any successful placement. The REDACTED CYBERWARFARE COMPANY candidate was blocked by a past criminal record. Henry, 2026-09-24: "не сможет в [REDACTED] устроится изза судимости в прошлом" (cannot get into REDACTED CYBERWARFARE COMPANY because of a past criminal record). REDACTED CYBERWARFARE COMPANY had no suitable role. No message confirms an operative inside a target firm by the end of the data on 2026-09-29.
The Fake Resume
The recovered PDF is a product of this operation. The cover identity is "Juan Diego Sanchez," Help Desk Technician at USF in Tampa. Created via Canva on 2025-01-04. Design IDs: DAF1L-FVgTE, BAFtZXrKf1A. Author: "Juan Sanchez." Fabricated references. Gmail: juandiego20995@gmail[.]com.
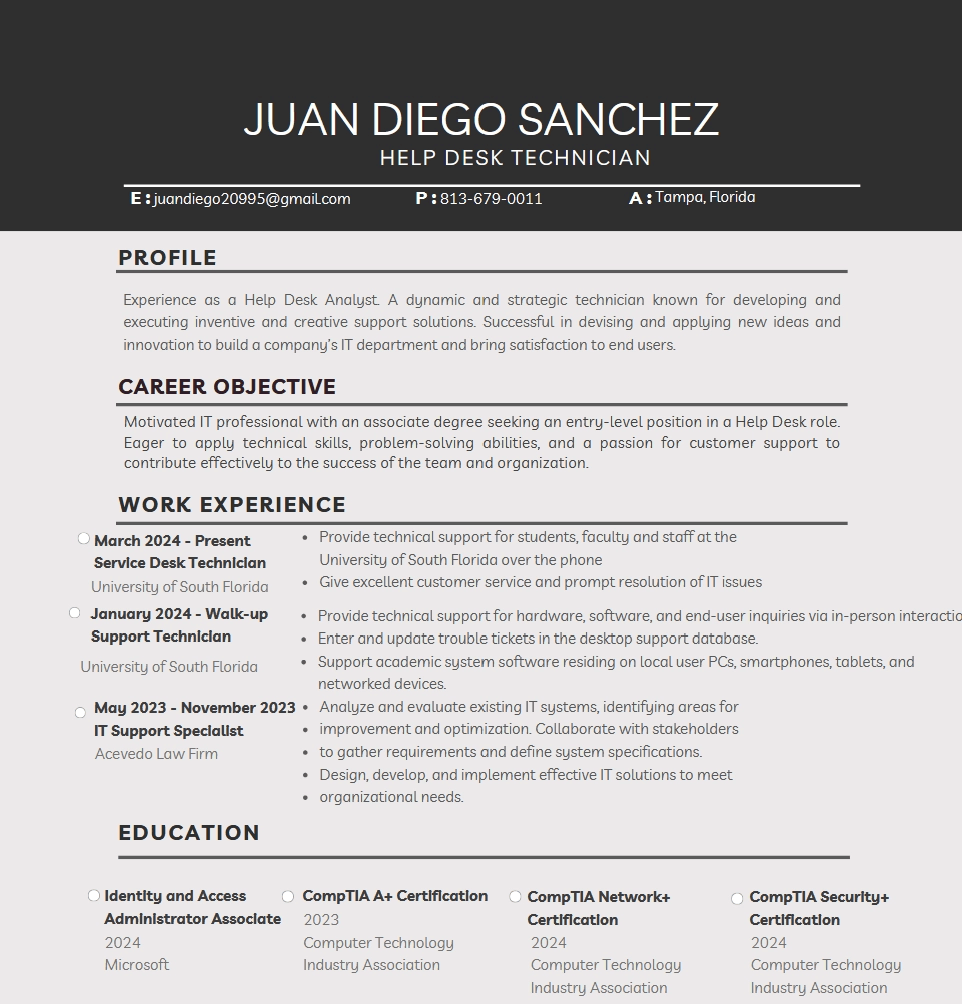
Screenshot of the resume uploaded to the SRG leak site.
DEEPFAKE_DATALOADING (9 messages)ShowHide
The DEEPFAKE_DATALOADING room holds a plan that has never shipped. On 2026-05-04, Adrian shared a 25 million dollar deepfake scam article from Hong Kong. Henry replied on 2026-05-09: "я в этих технологиях дип фейка вообще не разбираюсь" (”I do not understand deepfake tech at all”).
The method was a Microsoft Teams video call with a deepfake feed from a fake domain such as redacted-it[.]com, against the target REDACTED FIRM. The group looked for specialists on hh.ru, Telegram, and YouTube.
- References the Hong Kong $25M deepfake scam where deepfake video calls impersonated a company CFO
- Plan: register fake IT domains (for example,
redacted-it[.]com) and make deepfake Microsoft Teams video calls.
FAKE_CLEANER: Building Access via Bribed Cleaners (32 messages)ShowHide
Plan to bribe cleaning company employees for physical building access. Henry proposed a two-stage approach:
- Bribe a cleaner to share their entry pass. Copy it with a card skimmer.
- Use the cloned pass to let agents into the building after hours.
- Extend the same cleaner to other buildings in their company's portfolio.
Henry also proposed an HVAC sabotage variant: have the bribed cleaner damage a building's ventilation or heating system. Then send agents disguised as HVAC repair technicians.
we can use a scimer to copy his entry pass
Henry, 2026-03-19
in theory we would be able to get access to almost all big office buildings in nyc if we had our people in different hvac companies
Henry, 2026-03-19
Adrian forwarded a plan from Paul (an agent): use cleaners already inside corporate offices to call elderly IT staff via Zoom. Keep them on the call while an agent physically accesses their unattended workstation.
Status: Deprioritized as of May 2026. Henry assigned Agent Z to bribe valets and cleaners at their target building.
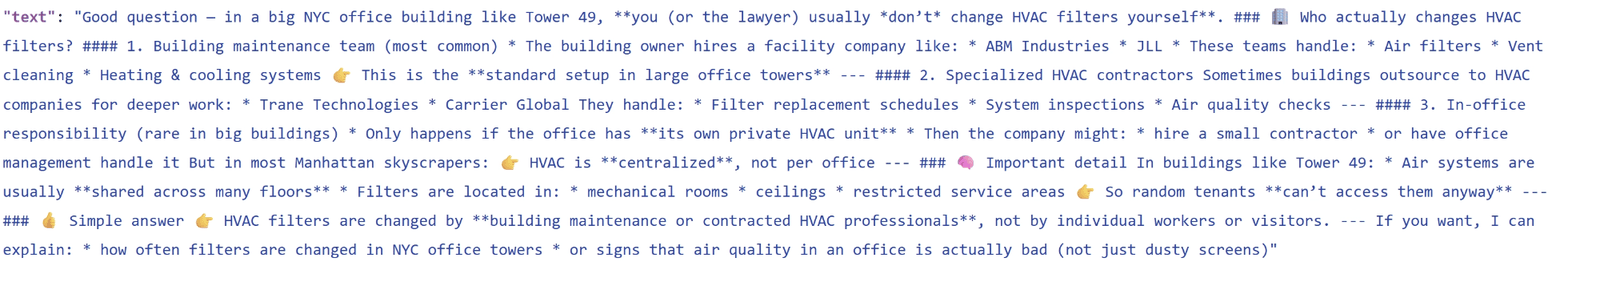
Translated message from Henry from 2026-03-19 detailing information necessary for HVAC operation.
VAN_SPR: Work Van Infiltration (9 messages)ShowHide
Agent OJ proposed buying a branded company van at auction to access Manhattan office towers:
- Buy a company van at auction ($8-9K) from a firm with offices in a tower that also houses law firms
- Copy the company uniforms and print fake badges
- Enter the building after 5-6 PM, pose as workers dropping off the van
- Change into business clothes in the bathroom and access target offices
- Use a card skimmer to clone entry passes
- After one operation, change the van stickers and uniforms for the next target
Нам не нужны агенты больше... Я буду их катать и все!!! Это топ вариант (Translation: We do not need more agents... I will drive them around and that is it!!! This is the top option)
OJ, via Adrian, 2026-03-19
Status: Deprioritized as of May 2026.
FAKE_CLIENT: Client Impersonation (12 messages)ShowHide
Plan to send agents into law firms disguised as clients. Adrian proposed the main variant:
- Enter as a client. Carry a USB drive with AnyDesk installed.
- Ask the lawyer to open a file from the USB "related to the case."
- When AnyDesk launches, the remote operator connects.
- The agent distracts the lawyer while the operator exfiltrates data.
we should only hope that he doesnt know what anydesk is
Henry, 2026-03-20
Henry later used this channel to recruit agents who did not qualify for the main vishing operation.
PRIVATE_INVESTIGATOR (18 messages)ShowHide
- Adrian wants PIs in New York to identify and surveil agent "xyz" (the ID maker they do not fully trust)
- Payment via BTC or Zelle
- Henry devises counter-surveillance: drop a package that requires a signature to identify the real address of xyz
xyz told me he knows some n****s from the ghetto who been to prison and dont care about anything and can shoot a person for 1000
Henry
Extortion Targets: Law and Accounting Firms
The named extortion targets sit in the US, across six states and Washington DC, plus one multinational firm. Adrian set the scope on the record: "берем в счет только UK и US" (we only count UK and US). REDACTED FIRM 2 is the multinational case, targeted in both the US and the UK. The locations below are the firms' headquarters from open sources.
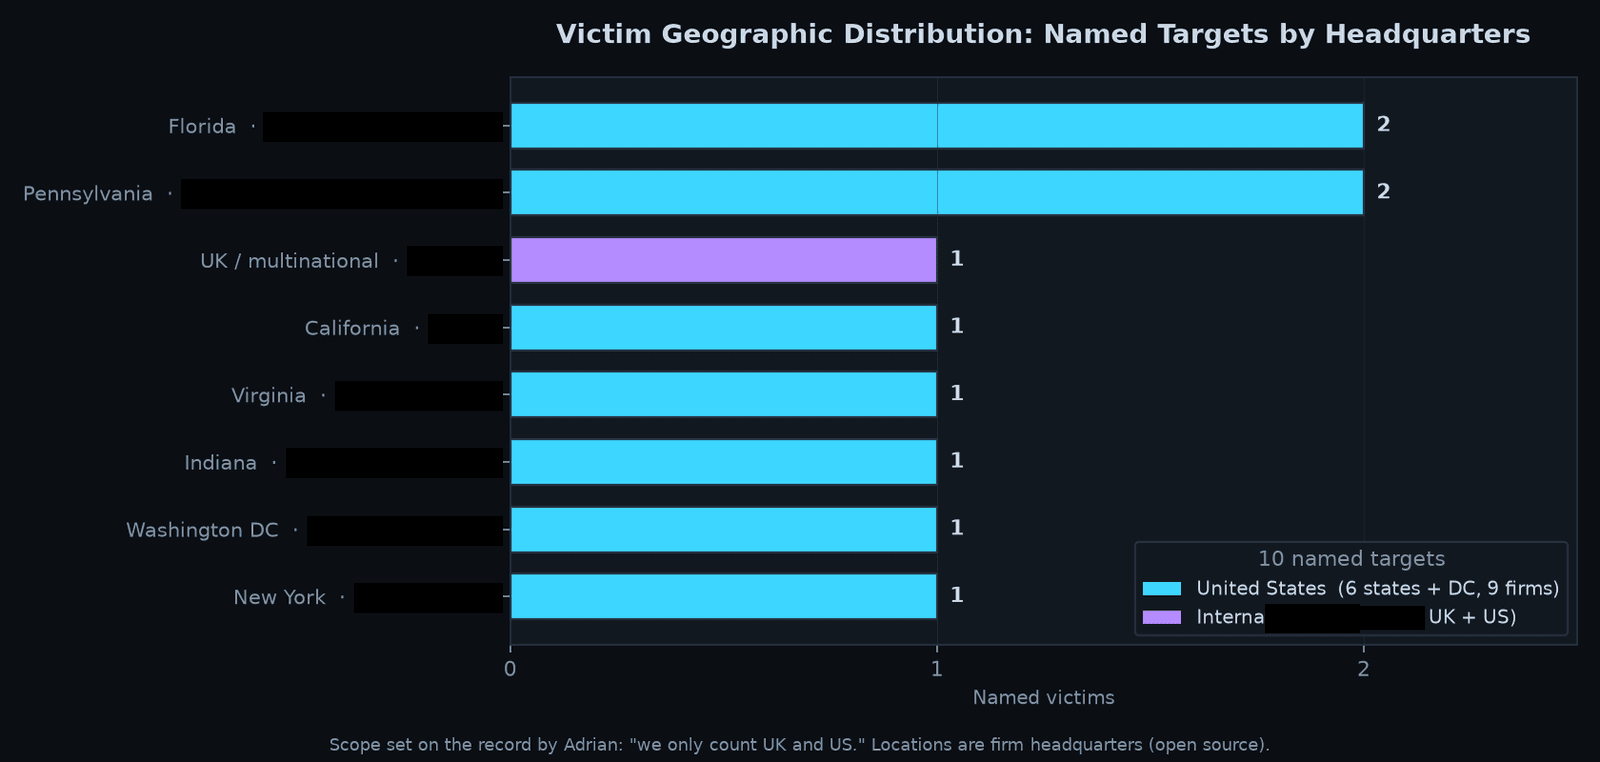
Victim geographic distribution. Named extortion targets by headquarters. Pennsylvania and Florida lead with two firms each. All are US except REDACTED FIRM 2, which is UK and multinational.
The victims and targets cluster by sector. The corpus references about 33 distinct firms. 29 are law firms, 2 are insurance or healthcare, and 2 are accounting. Law firms are about 88 percent. This set is the targeting universe, which is wider than the confirmed-paid set of about 27 GOLD firms.
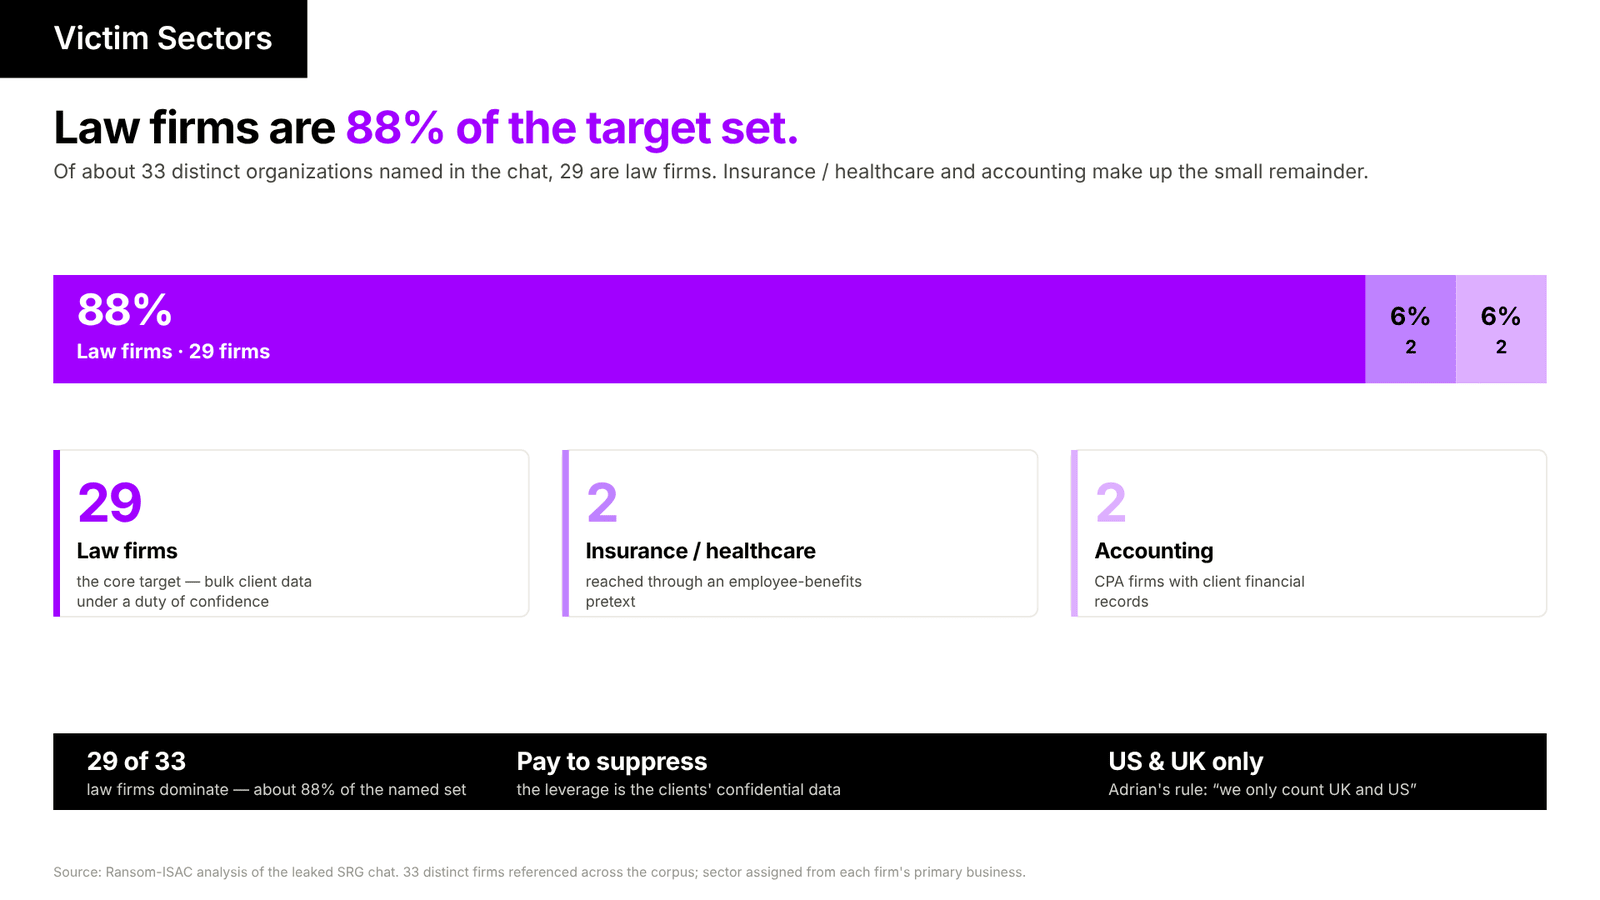
The victim set by sector. Of about 33 distinct firms referenced, 29 (about 88%) are law firms. Insurance/healthcare and accounting make up the small remainder.
The spread is wide but the profile is narrow. Every named target is a US or UK professional-services firm with data worth a seven-figure or eight-figure ransom.
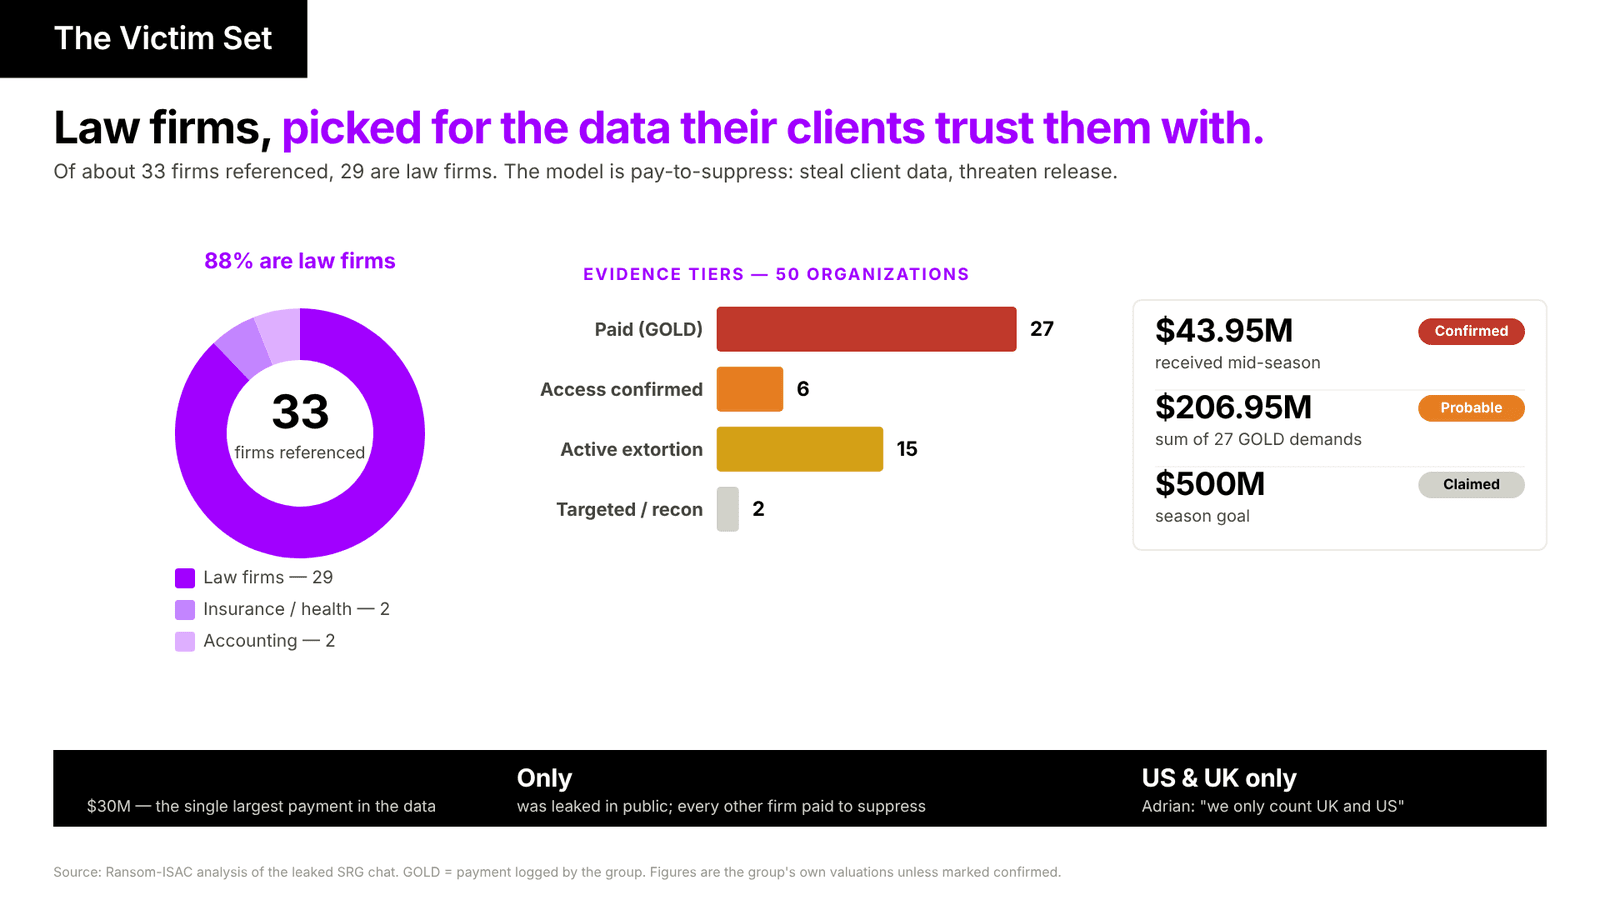
The victim set by sector and evidence tier. Of about 33 firms referenced, 88% are law firms. The group's accounting records at least $43.95M received. The $206.95M and $500M figures are the group's own valuation and goal.
Vishing Call Script: Full Breakdown
The vishing_call_script.txt is a two-part Russian-language document with English notes. This is the operational playbook for the phone-based attacks discussed in SPR_TRG_TALK. The REDACTED FIRM victim room confirms the method with the note "anydesk + 22" as the access method.
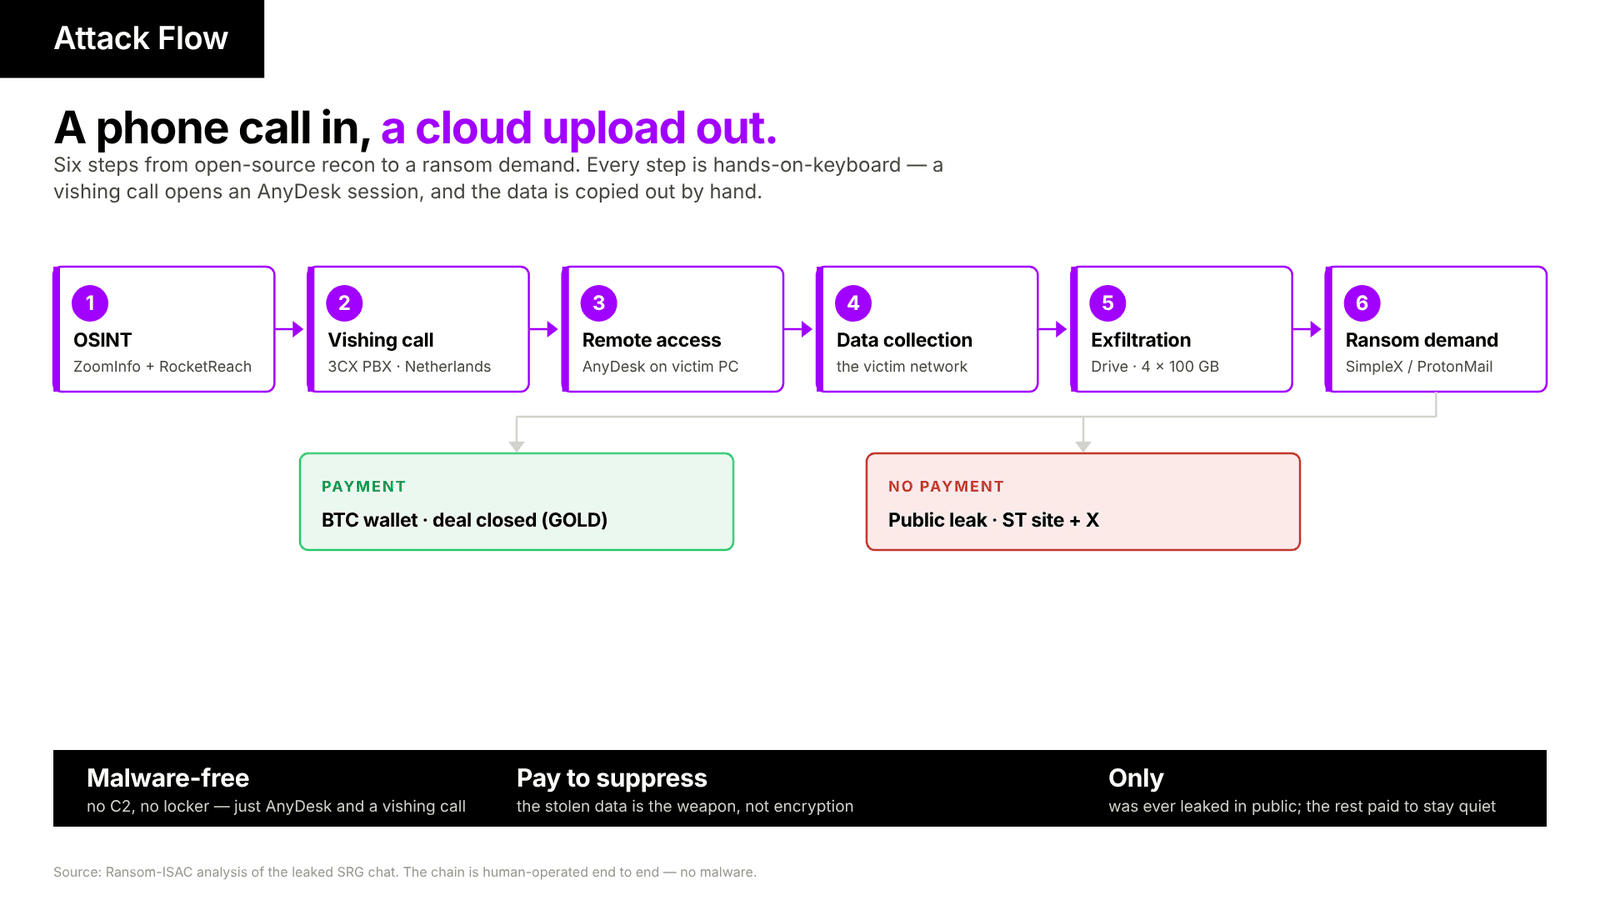
The end-to-end attack chain. Six hands-on-keyboard steps from OSINT to a ransom demand, then a fork. Payment closes the deal, refusal triggers a public leak.
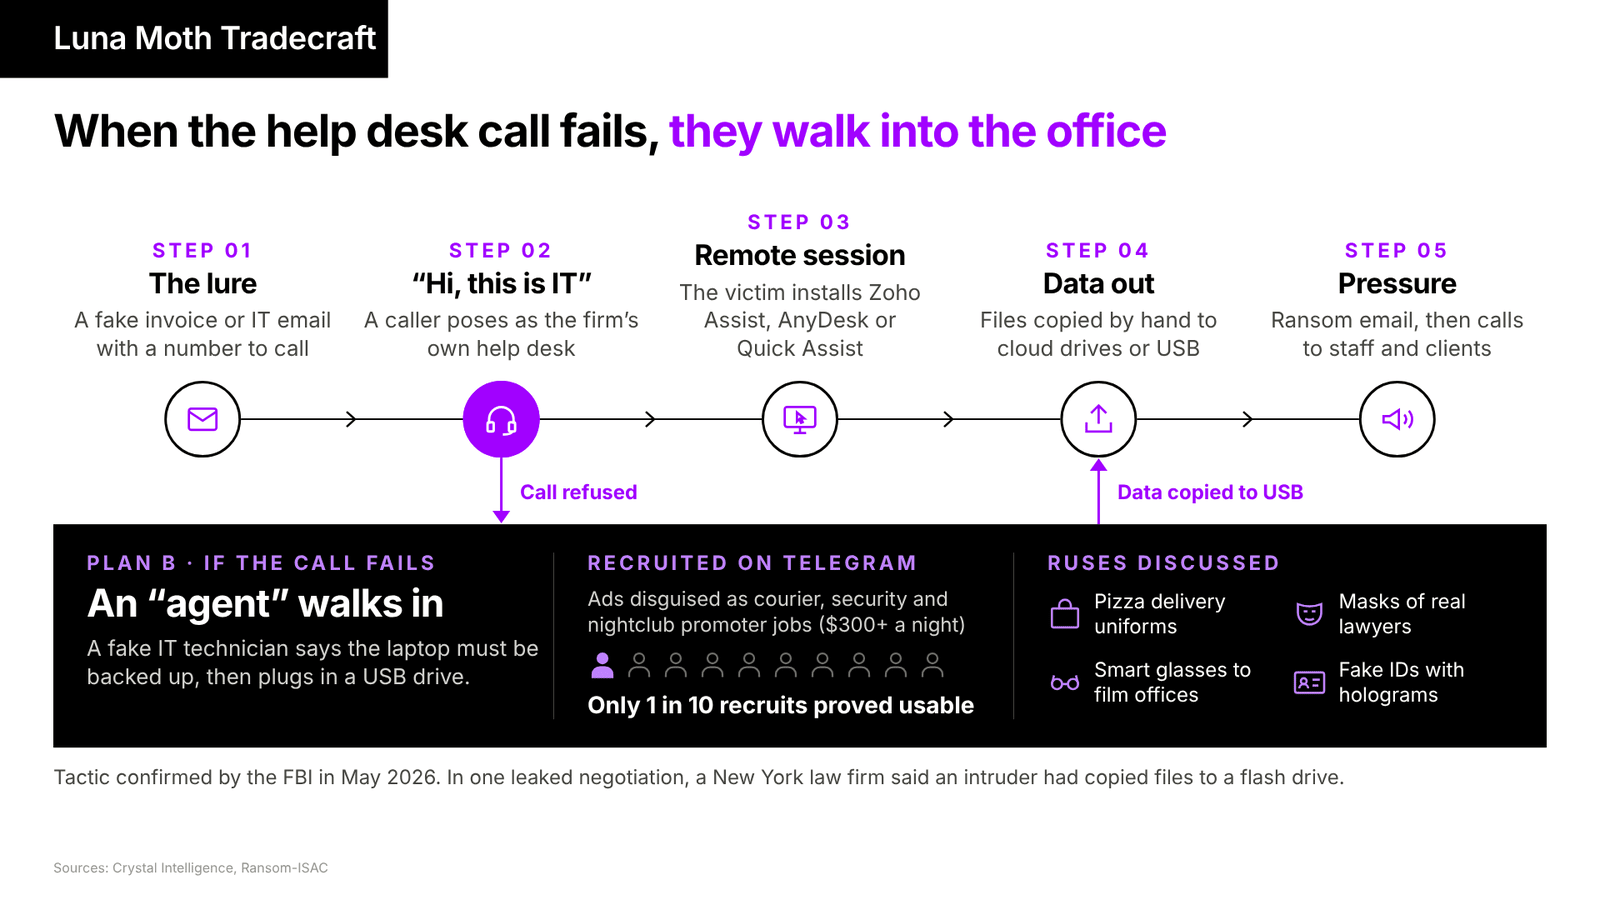
The callback phishing chain and the physical fallback. Step 04 shows the hand-copy method. The corpus holds no exfiltration utility. Slide details on recruitment and ruses come from Crystal Intelligence.
Part 1: Methodology (Freeform)
The author describes their personal technique in first person. The attack has eight steps:
- Introduction. Call the target. Introduce yourself with confidence as a name from the IT department. Ask how they are, as if you know them personally.
- Fear induction. Tell them that suspicious activity was detected on their device. Ask if they received an email with a PDF. 99% say no.
- Relief and re-escalation. Say "we blocked the email." This calms them. Then say that other employees DID click the PDF and that the network is now compromised.
- False familiarity. Say "I know you would never do something like that." This builds trust while it implies surveillance.
- Remote access request. Tell them you need to run a "security check" via remote access (AnyDesk). The caller must know the tool well.
- Exfiltration. Once connected, tell the target not to touch anything. Check the group chat every minute for instructions.
- Persistence cover. Say "Security updates installed." Tell the target to leave the computer on for at least one day.
- Callback channel. Ask the target to save your phone number for future contact.
this is exactly what i do on call and how i talk to them
its basically playing with their nerves in trg i will make it a script Author's English note
Part 2: Scripted Roleplay (Formal)
A polished Russian-language dialogue between "IT Manager" and "Employee" with:
- Opening: Polite introduction. Ask if the employee has a few minutes.
- Three probing questions: Security, unauthorized software, device behavior.
- Objection handling: When the employee says "I'm not comfortable with a remote session", the script counters with a corporate directory check and identity confirmation email.
- Closing: Session link delivery, gratitude, and reassurance.
The 3CX PBX infrastructure (87.251.67[.]222/223 in the Netherlands) provides the phone system for these calls.
Data at Risk: What They Steal and Why
The model is pay to suppress. The stolen data is the whole weapon. For a law firm the data is the clients' data, and much of it is held under a duty of confidence. A leak harms the clients, not only the firm. That is the pressure the group sells.
What They Take
The group takes bulk client data, not single files. Adrian described one hit as a full breach: "я взломал всю их базу данных" (I breached their entire database). The recovered material shows three kinds of data.
- Personal data at scale. Adrian: "десятки тысяч SSN" (tens of thousands of Social Security numbers) and "тычсячи тысячи confidential" (thousands and thousands of confidential records).
- Litigation and privileged material. The group profiles litigation leaders by exact title, for example "Co-Chair, Business Litigation" and "Attorney & Associate Director, Litigation".
- Financial and deal data. The group tracks chief financial officers by name and researches mergers.
Volume
The group stages the data to consumer cloud storage. The chat references several 100 GB Google Drive accounts and larger stores. Single-victim mentions run from a few GB to tens of GB. Aggregate references reach the terabyte range.
Target Sectors
James set the target list on the record: "интересны financial, insurance, accounting, law firms, manufacturing, hotels, healtcare" (we want financial, insurance, accounting, law firms, manufacturing, hotels, and healthcare). In practice, law firms dominate the victim set.
Why Law Firms Pay
The pressure point is the clients, and the victims say so themselves. One firm, which approved a seven-figure payment, wrote that the amount was "significantly more than the data you took is worth to us." The firm added that it paid only out of respect for its clients' confidentiality. The group aims its pitch at that fear. Its extortion message calls payment the cheapest way to keep the incident confidential. The group also studies breach precedent. It researched a 2023 breach, which affected more than 637,000 individuals, as a measure of the cost of exposure.
Extortion Methodology
The group runs a fixed pricing model and a fixed pressure playbook. The status pipeline is EMAIL to CHAT to LOADING to OFFER to CONTRACT to GOLD.
The pipeline below shows the six stages and the lever that moves a victim to the next one.
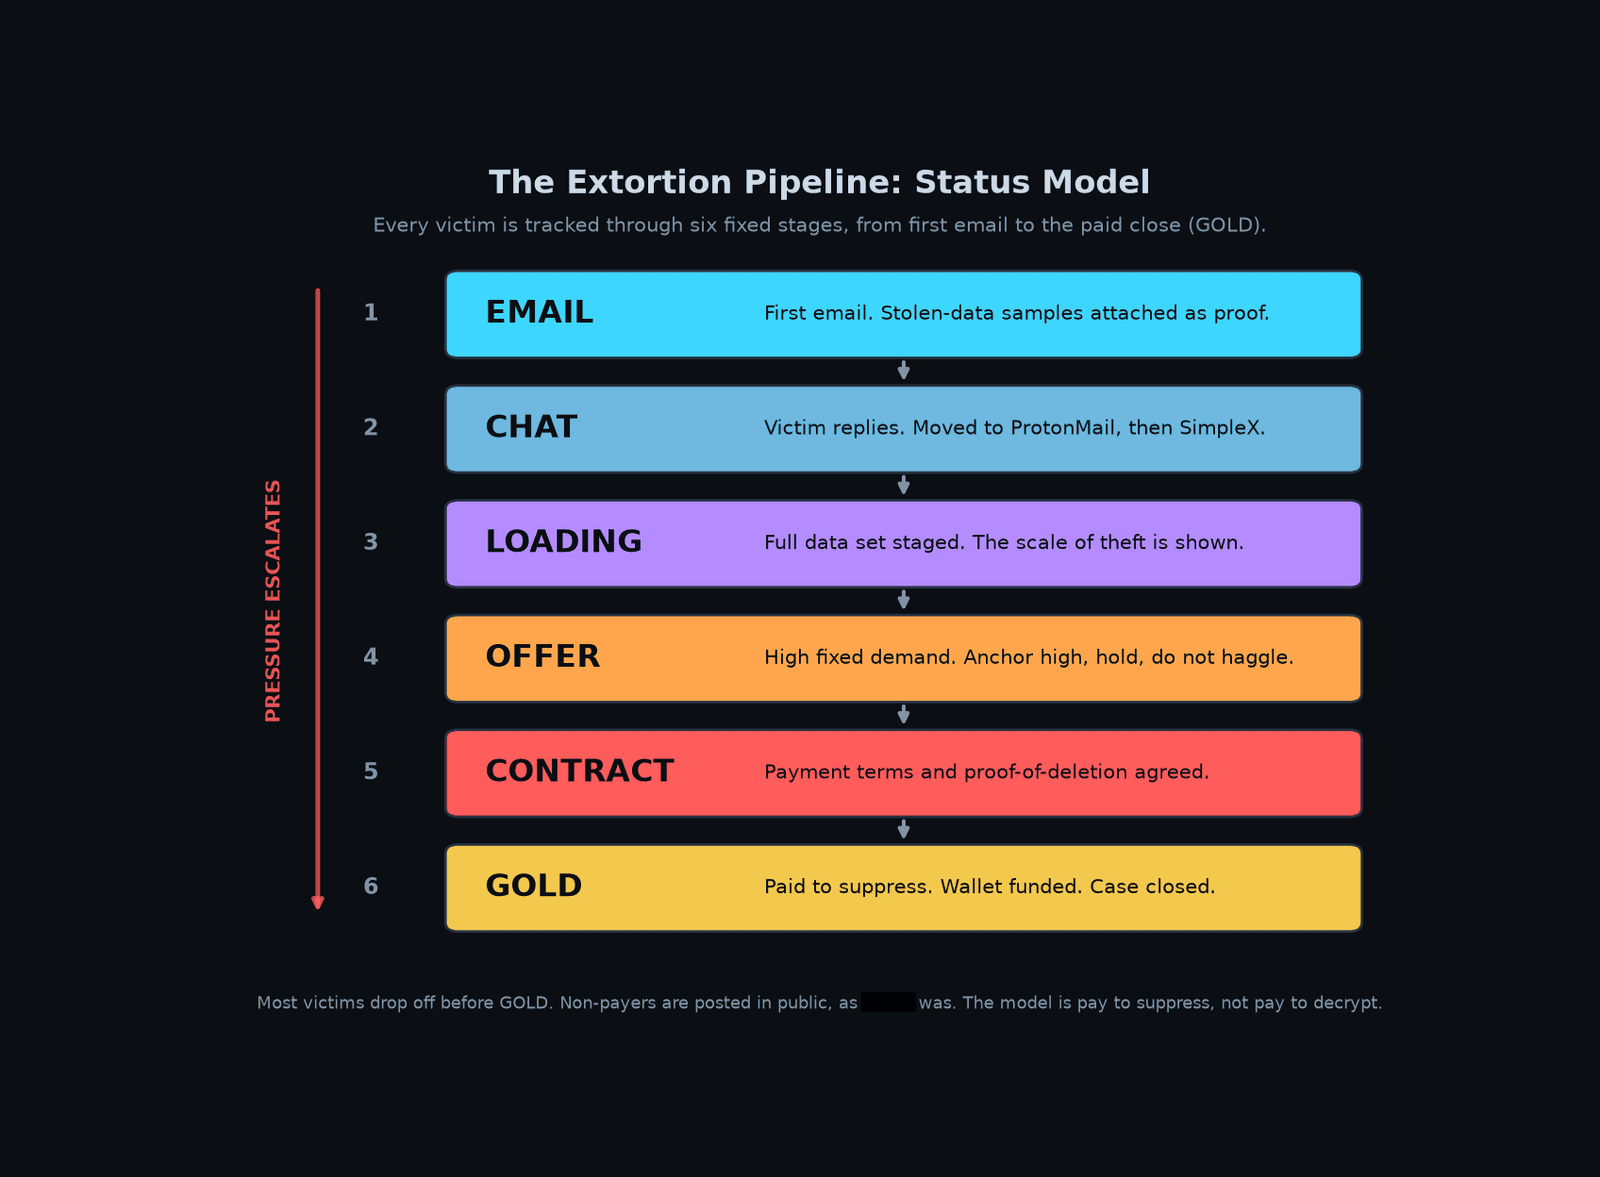
Extortion pipeline status model, six stages from EMAIL to GOLD with escalating pressure
Pricing Model
Offers anchor high and hold. The group does not haggle. REDACTED FIRM 1 is the clean example.
| Date | Marker | Amount (USD) |
|---|---|---|
| 2026-09-02 | OFFER | 5,000,000 |
| 2026-09-02 | OFFER | 9,365,000 |
| 2026-09-04 | OFFER | 18,730,000 |
| 2026-09-21 | GOLD (paid) | 30,000,000 (31,250,000 at BTC rate) |
The path ran from 5 million to 30 million dollars. Adrian on the close: "РЕКОРДНЫЙ ГОЛД БРАТ! ДАВАЙ КОШИК" (record GOLD bro, give the wallet).
The ladder below traces the REDACTED FIRM climb from the first offer to the paid GOLD.
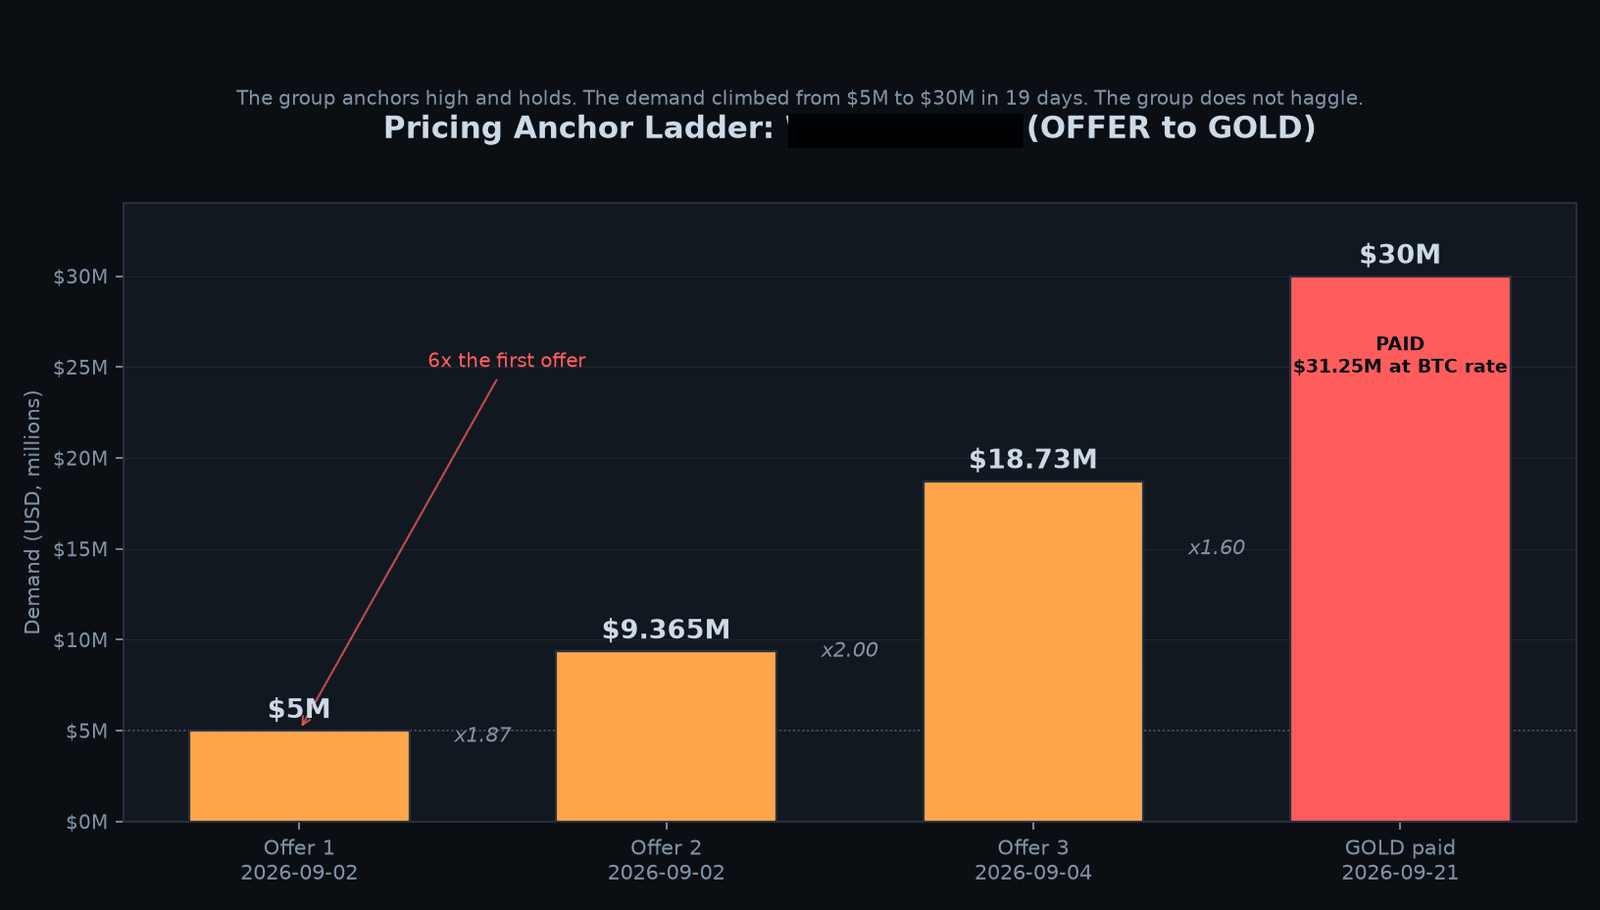
REDACTED FIRM 1 pricing anchor ladder, 5M to 30M over 19 days, paid GOLD
The anchor-high strategy is measurable in the ledger. Across the 22 victims for which both an opening offer and a payment are recorded, the amount paid was a median of 5.5× the opening demand, reached over a median of 10 days. Of the 16 victims who received more than one offer, 15 closed higher than they opened — the group effectively never moves downward. The spread runs from $100K → $6M in 23 days to $500K → $20M in 22 days; the two initial September demands were $250K and $450K.
Offer vs Payment
Across the ledger the group opens with a first offer and then ratchets the demand upward under deadline pressure, so victims almost never pay the opening figure. Of the firms where both a first offer and a paid GOLD are recorded, the amount paid is a median of 5.5 times the opening demand. The spread is wide. At the low end REDACTED FIRM paid 1.6 times its first offer. At the high end one firm paid sixty times, moving from a $100,000 opening to a $6,000,000 close, and another paid forty times, from $500,000 to $20,000,000.
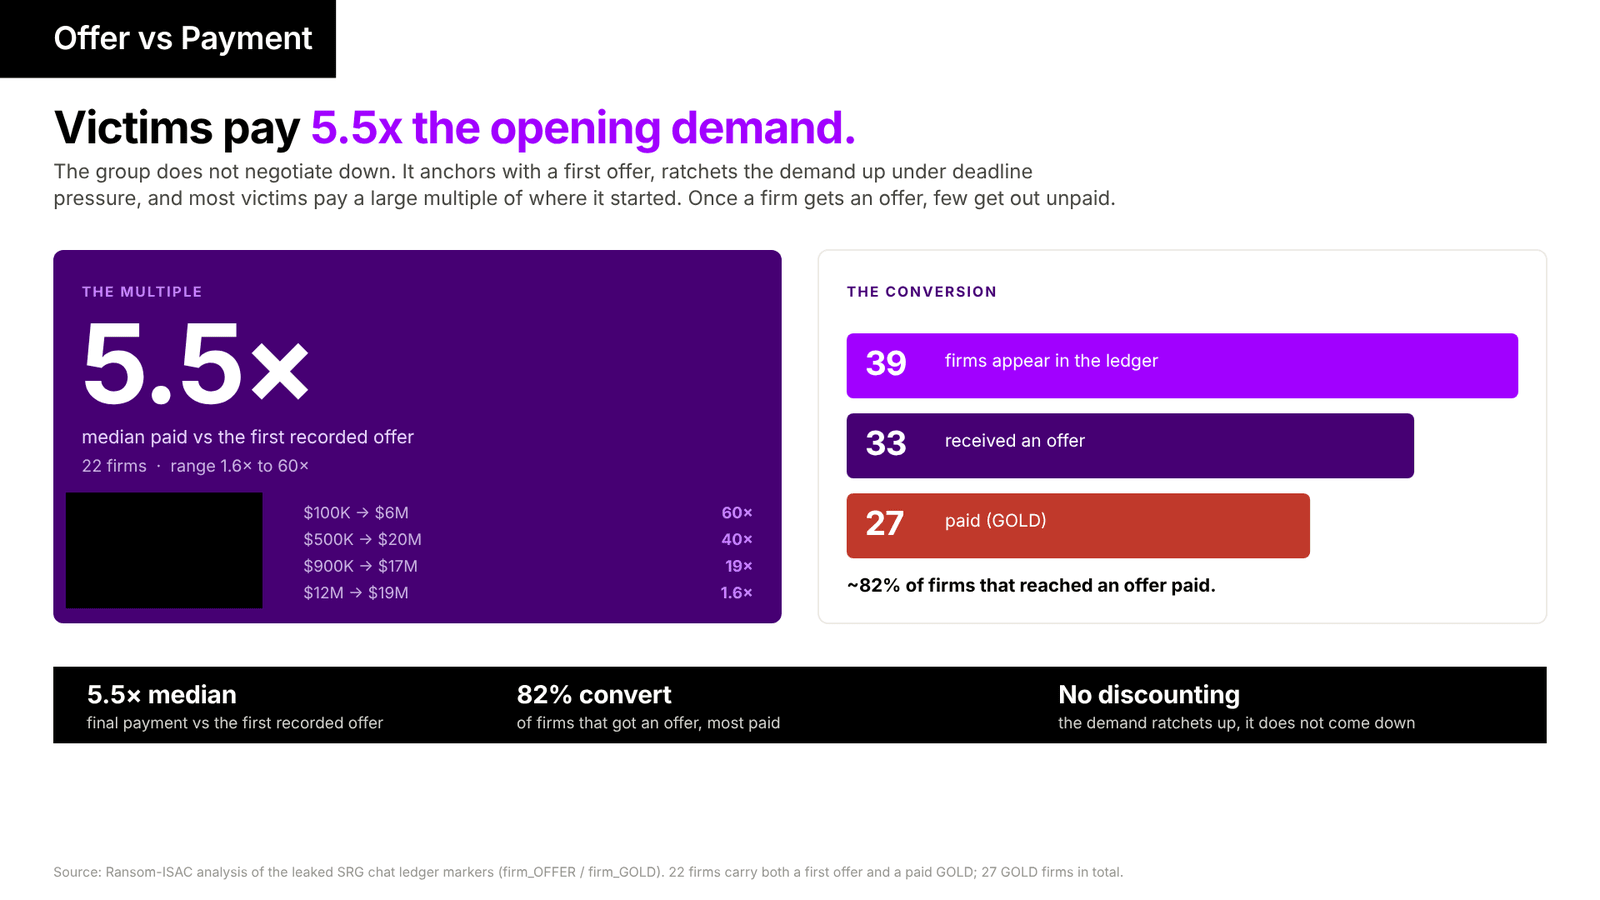
Four names of victim firms have been redacted.
The second pattern is conversion. Thirty-nine firms appear in the ledger with a negotiation marker. Thirty-three of them reached an offer, and twenty-seven paid. Once a firm is engaged to the point of an offer, roughly four in five pay. The group does not discount to close. It holds the anchor, raises it, and relies on deadline and leak pressure to carry the victim to a figure well above where the conversation began. For a defender the implication is blunt. The decisive moment is before the first offer, not during the negotiation, because by the time an offer is on the table the outcome is already weighted heavily toward payment.
Pressure Playbook
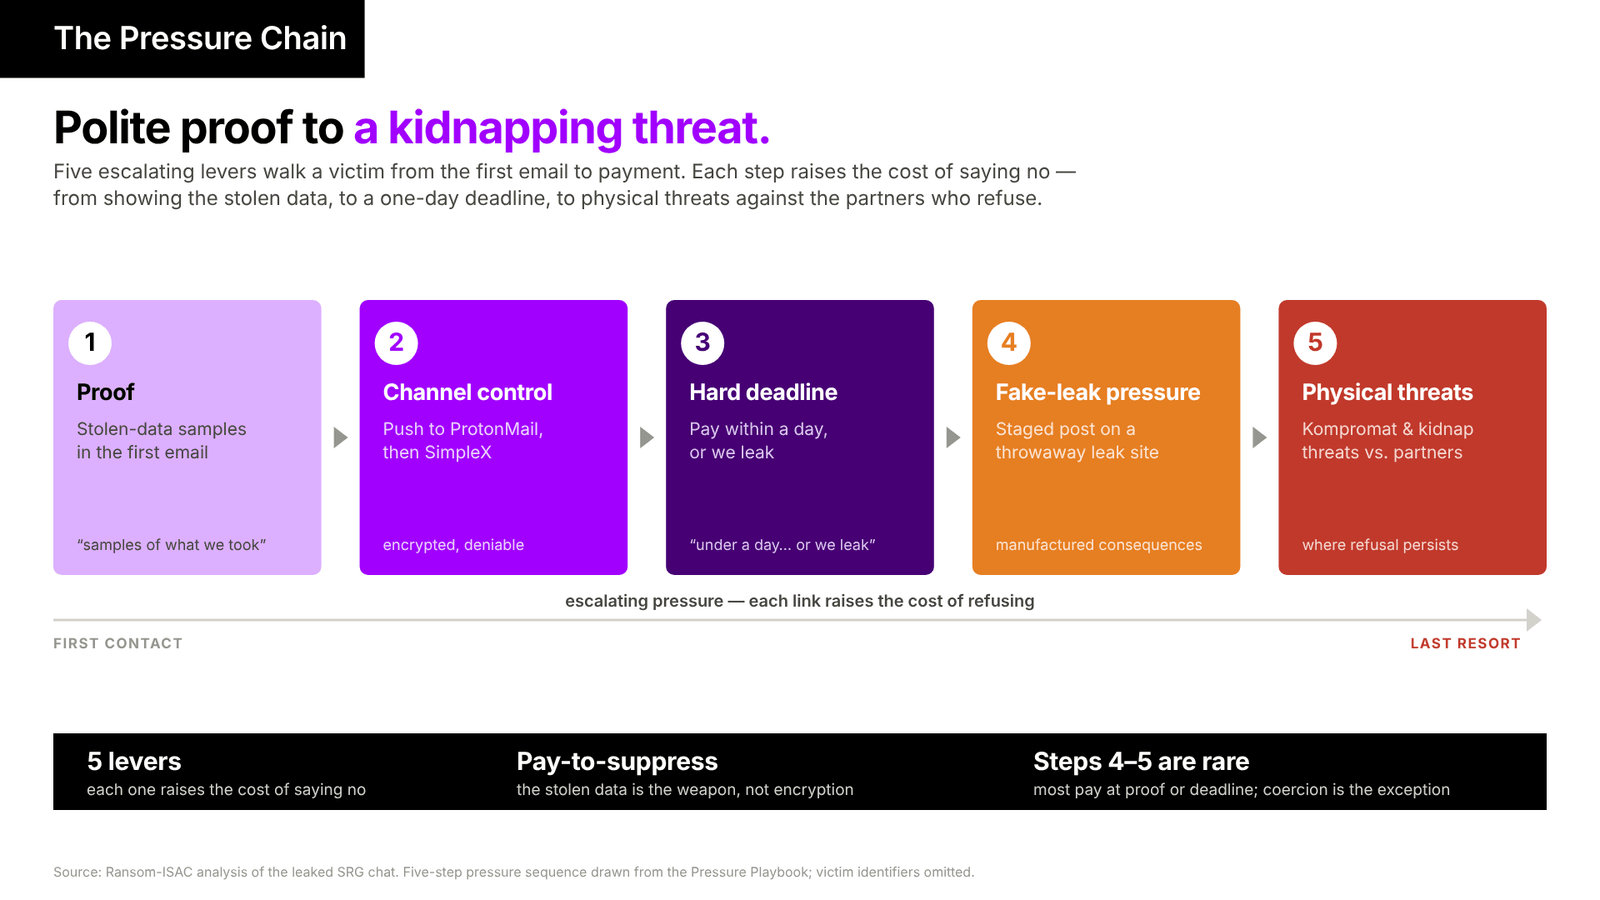
The Pressure Chain: polite proof to a kidnapping threat.
- Offer Proof: The first email carries stolen-data samples. To REDACTED FIRM, 2026-09-02: "We attached the list of data we took from your network... some samples for you to see what we took."
- Move to an encrypted channel: ProtonMail, then SimpleX. The REDACTED FIRM 3 handle is
new2-th1s-talk, the REDACTED FIRM 4 handle ismutagenic. - Hard deadline: 2026-08-27: "скажи у них меньше суток что бы ответить - иначе сольем" (tell them under a day to answer, or we leak).
- Fake-leak pressure: 2026-09-24: a staged post on
sdfmskfd[.]comclaiming new company names leaked, to manufacture consequences. - Physical threats where used: 2026-03-15: kompromat and kidnapping threats against senior staff who refuse (Not currently deployed as part of active pipeline)
Case Snippets
- Case One. Contact the firm contact. Moved from chat to SimpleX
new2-th1s-talk. - Case Two Access vector
anydesk + 22. Contact the firm contact, who replied: "Got your note, let's chat." - Skeptical victim (Case Three, 2026-09-21). "how am I supposed to take that offer seriously when you don't have a website, no established reputation, and haven't even provided the files?"
- Case Four (2026-02-20). The victim approved a 1,000,000 dollar payment: "This meets your seven-figure requirement... significantly more than the data you took is worth to us."
Case Three auto-reply. An out-of-office reply to the extortion email, subject "REDACTED cyber security incident". From a managing director. Names his assistant an assistant. Proof the email reached the victim.
Victim auto-reply. An out-of-office reply to the extortion email, subject "REDACTED FIRM 3 cyber security incident". From a staff member. Proof the email reached the victim.
Victim out-of-office auto-reply, provided as proof that the extortion email reached the victim.
Vishing Campaign Infrastructure (August-September 2026)
On August 26, 2026, Adrian distributed operational packages for simultaneous vishing campaigns against 15+ firms. Each package contains a dedicated Gmail, a Google Voice number with credentials, and an executive target list.
Show table (13 rows)
| Target Firm | Operational Gmail | GV Number | GV State |
|---|---|---|---|
| REDACTED FIRM | kalvaramanjunath@gmail[.]com | (504) 356-3852 | LA |
| REDACTED FIRM | abdulkalerm20@gmail[.]com | (502) 783-7917 | KY |
| REDACTED FIRM | alamkhan.davangere@gmail[.]com | (316) 749-8765 | KS |
| REDACTED FIRM | raveeshkumar391@gmail[.]com | (717) 478-4359 | PA |
| REDACTED FIRM | muneshm138@gmail[.]com | (260) 786-5438 | IN |
| REDACTED FIRM | abhishekkurahatti004@gmail[.]com | (601) 994-5243 | MS |
| REDACTED FIRM | sureshshetty9691@gmail[.]com | (208) 557-4852 | ID |
| REDACTED FIRM | basavarajn773@gmail[.]com | (503) 714-5633 | OR |
| REDACTED FIRM | pushpavathi8050866121@gmail[.]com | (816) 514-5415 | MO |
| REDACTED FIRM | vishwaskamble305@gmail[.]com | (405) 696-7842 | OK |
| REDACTED FIRM | mamathasonu169@gmail[.]com | (612) 568-5418 | MN |
| REDACTED FIRM | gcvijapur@gmail[.]com | (304) 884-5645 | WV |
| REDACTED FIRM | abrorjon7@gmail[.]com | (951) 456-2338 | CA |
Each Google Voice account has a Gmail, a password, a Hotmail recovery email, and a TOTP backup code on file. The GV numbers are registered in different US states to match the area code of each target firm's headquarters.
Compromised Networks (Mike, ZoomInfo Recon, 2026-09-23)
| Organization | Hosts | AV/EDR | Access Level |
|---|---|---|---|
| REDACTED LAW FIRM | Withheld | SentinelOne | Withheld |
| REDACTED INSURANCE | 12,000+ | Sophos | Domain Admin |
Active Victim Negotiations (September 2026)
On the secondary server under the "Sleepless Threat" brand:
GOLD Record: REDACTED FIRM 1
The largest single payment in the dataset. The negotiation progressed over 19 days:
| Date | Status | Amount |
|---|---|---|
| Aug 26 | CHAT | Initial contact. "All VM" (voicemails left). |
| Sep 02 | OFFER | $5,000,000 |
| Sep 02 | OFFER | $9,365,000 |
| Sep 04 | OFFER | $18,730,000 |
| Sep 21 | GOLD | $30,000,000 (adjusted to $31.25M for BTC rate increase) |
РЕКОРДНЫЙ ГОЛД БРАТ! ДАВАЙ КОШИК
(RECORD GOLD BRO! GIVE ME THE WALLET)
Adrian, 2026-09-21
Operational infrastructure for this attack:
- Operational email:
kalvaramanjunath@gmail[.]com - GV for vishing:
eldowdy4187@gmail[.]com/ (504) 356-3852 (LA)
GOLD: REDACTED FIRM 2
- GOLD amount: $21,000,000 (Aug 26 2026)
- Henry: "u nikh naverro khoroshaya infa byla skachana" (they probably had good data downloaded)
- Mike's recon (Sep 23): AV: SentinelOne. Host count and access level withheld.
- GV for vishing:
buckettwigg@gmail[.]com(number withheld)
Executive target list:
The actors compiled a target list of 10 senior executives (President, Global CIO, US and Global CEOs, US Managing Partner, US Chair, Co-Chair of Global Privacy and Cybersecurity, and other partners) with their work emails and phone numbers. Names and contact details are withheld from this public release.
REDACTED FIRM 3
- Victim contact: [contact withheld]
- Ransom demand: $250,000
- Comms: ProtonMail to SimpleX Chat (handle:
new2-th1s-talk) - Evidence of data: file paths and a workstation name from the victim network (withheld)
REDACTED FIRM 4
- Victim contact: the firm contact [contact withheld]
- Ransom demand: $450,000
- Initial access: AnyDesk + vishing ("anydesk + 22")
- Comms: SimpleX Chat (handle:
mutagenic) - Victim was skeptical: "how am I supposed to take that offer seriously when you don't have a website, no established reputation"
REDACTED FIRM 5
- Victim contact: [contact withheld]
- Initial access: Zoom + Google Drive
- Status: Loading / staging phase
REDACTED FIRM 6
- Target contact: a VP, Corporate Groups [contact withheld]
Victim Status Tiering
The group tags every victim with a status token. The token moves through a fixed pipeline. This pipeline is the single most useful key in the data. It separates paid deals from open demands.
Pay-to-Suppress Model
Victims pay to suppress public information leak, not to decrypt data. The group steals data and threatens release.
Only one firm was leaked publicly due to lack of payment. Adrian posted a databreaches.net link for one victim on 2026-04-10 and said the goal was "просто их слить" (”just to leak them”). One leak was a fake planted on sdfmskfd[.]com to pressure the victim, not a real publication.
Victim Lifecycle
EMAIL (first contact sent) then CHAT (victim replies) then LOADING (data being stolen) then OFFER (ransom talks, rising amounts) then CONTRACT (deal agreed) then GOLD (closed, payment collected).
GOLD means paid, not demanded. Every GOLD tag is followed by a wallet request ("ДАВАЙ КОШИК" / give me the wallet). On 2026-04-29 Henry confirmed collection directly: "отправил кош на 500 от REDACTED_GOLD" (sent the wallet for 500k on REDACTED).
Payment Tiers
| Tier | Meaning | Firms |
|---|---|---|
| Tier 1 Paid (GOLD) | Payment collected | 27 |
| Tier 1 Access | Internal access confirmed, no GOLD yet | 6 |
| Tier 2 Extortion | Demand or active talks, no confirmed access | 15 |
| Tier 3 Targeted | Email or recon only | 2 |
The 27 paid firms are the GOLD entries in the Law Firm Extortion table above. The five largest are $30M, $21M, $20M, $19M, and $17.5M.
Payment Figures: Confirmed, Closed, and Claimed
| Figure | Amount | Grade | Source |
|---|---|---|---|
| Recorded as received this season | $43,950,000 | Confirmed | Adrian, internal accounting, 2026-05-04: "мы получили в этом сезоне уже выплат на 43.950.000". Mid-season figure. |
| Closed-deal demand value | $206,950,000 | Probable | Sum of the 27 GOLD firm demands. The group's own valuations. |
| Season goal | $500,000,000 | Claimed | Adrian, 2026-09-02: "за сезон план пол миллиарда долларов" (half a billion dollar plan for the season). |
The $43.95M is the only received figure the group's own accounting states. It is a floor: it covers payments up to 4 May. Treat the GOLD sum as closed-deal value. Treat the $500M as a goal.
Technical Infrastructure
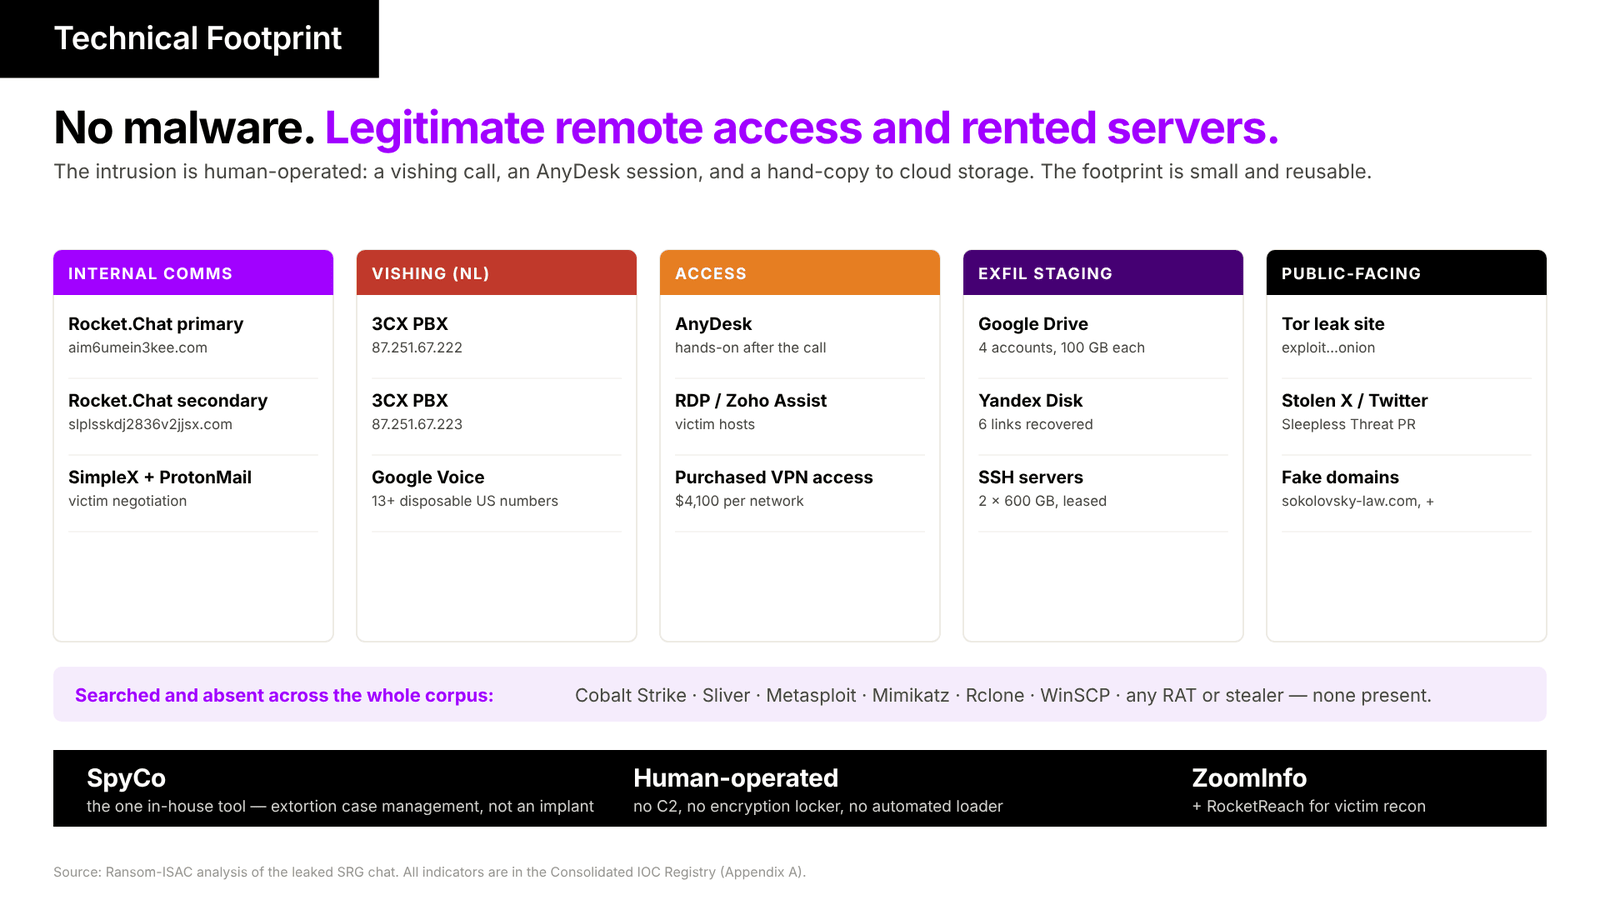
The group's technical footprint, grouped by function. The intrusion is human-operated: no C2 framework, no encryption locker, no malware. A full-corpus search for offensive tooling returned nothing.
Tools and Capabilities
This ranks the tools and capabilities the operators discuss, and maps each to the operator who owns it, ranked using number of messages that mention the item.
Tool Index
Show table (18 rows)
| Tool | Use |
|---|---|
| AnyDesk | Remote access after vishing calls |
| 3CX PBX | Phone system for vishing (Netherlands VPS) |
| Citrix / VPN | Persistent access to victim networks |
| ZoomInfo + RocketReach | OSINT for target employee recon |
| Zoom | Video pretexting |
| Google Drive (4 accounts) | Exfiltration staging |
| SimpleX Chat | Victim ransom negotiations |
| ProtonMail | Initial victim contact |
| Privnote | Self-destructing credential sharing |
| Canva | Fake document creation |
| Deepfake technology | Video call impersonation (planned) |
| SpyCo | Custom tool built by James (JS obfuscation) |
| Rocket.Chat (self-hosted) | Internal communications |
| X/Twitter (stolen account) | Sleepless Threat PR and leak announcements |
| ChatGPT | OSINT research (military bases, defense contractors, law firm breaches) |
| Card Skimmers | Clone employee building access passes |
| Yandex Disk | Exfiltrated data storage (6 links recovered) |
| Google Voice | Disposable US phone numbers for vishing (13+ accounts recovered) |
Tool & Capability Mentions
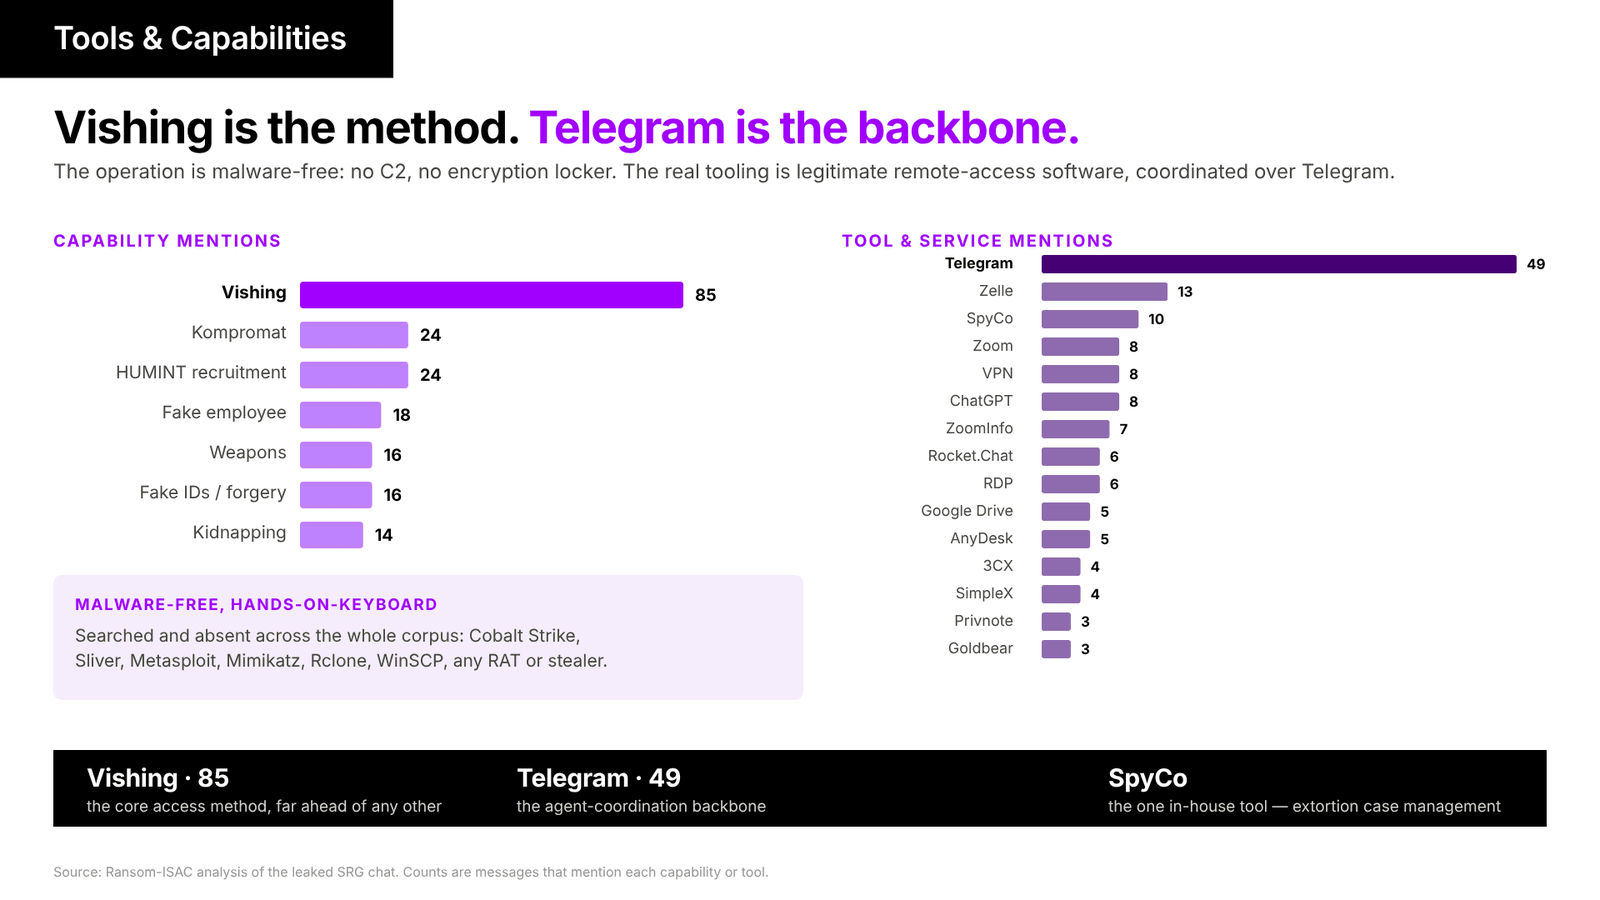
Capability and tool mentions across the corpus. Vishing dominates the capability talk. Telegram is the most-mentioned tool. The operation is malware-free. No C2 framework, encryption locker, or offensive tooling appears.
Tool Mention Breakdown
This pie shows every operational tool and service as a share of total tool mentions across the corpus. The count is the number of chat messages that name the tool. The view is corpus-wide and does not split by operator. Telegram dominates because it is the coordination backbone for the field agents. The intrusion tools are legitimate remote-access software, AnyDesk and RDP, not malware.
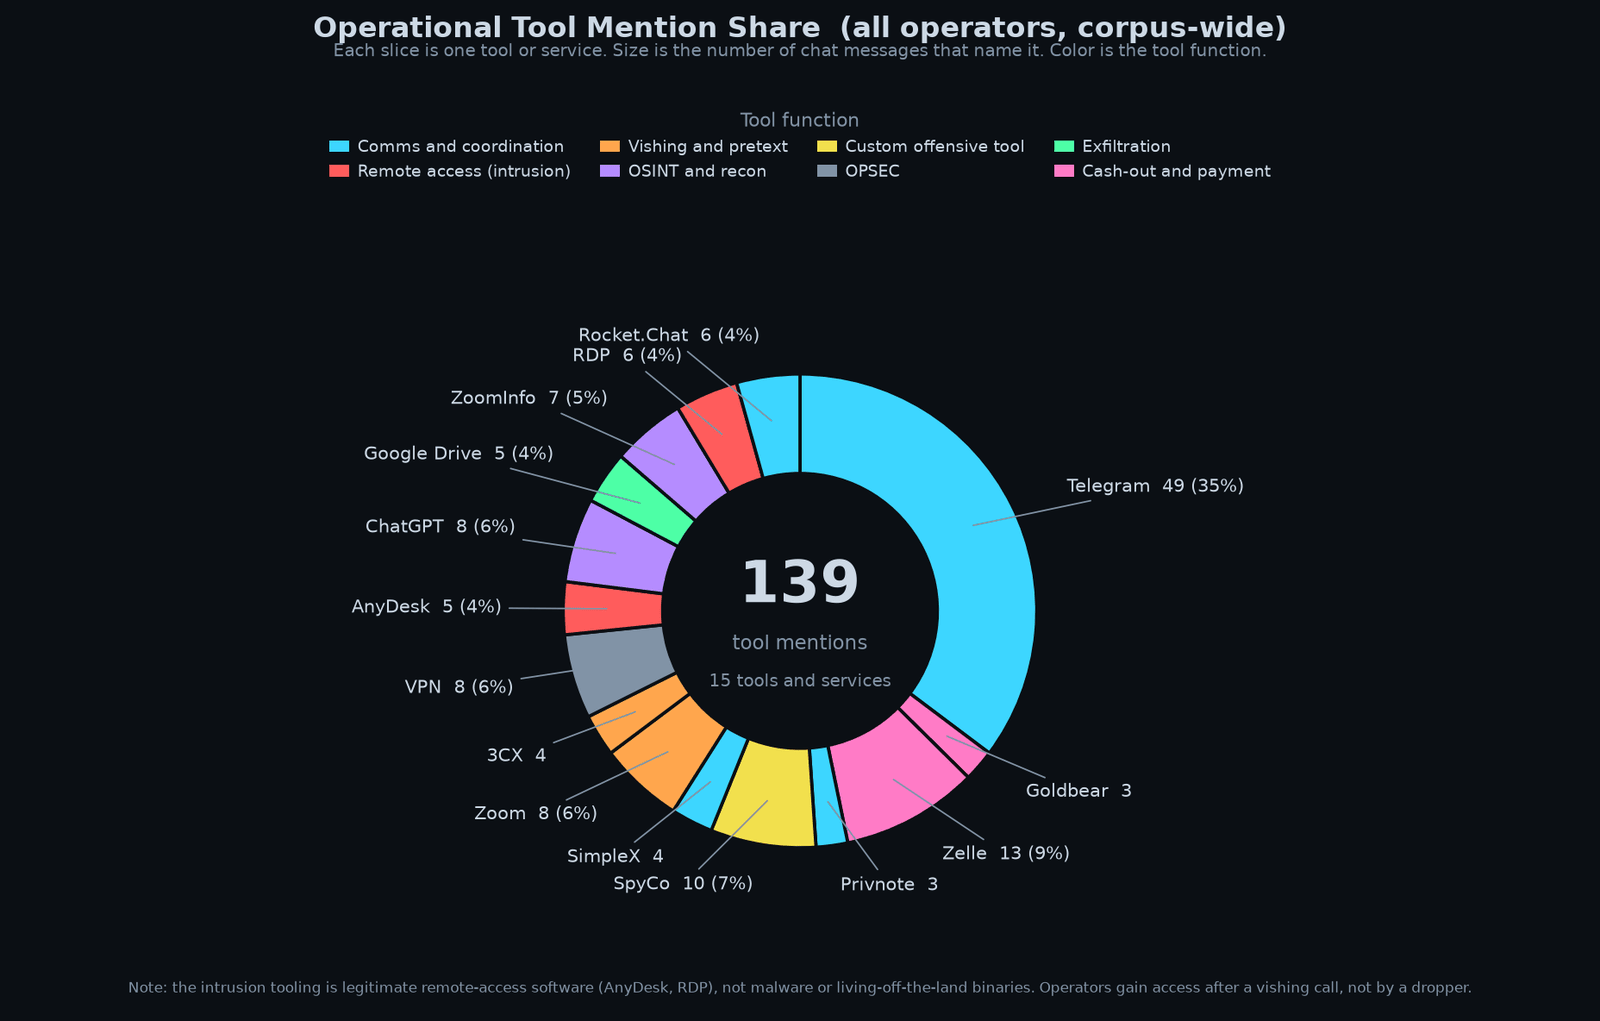
Operational tool mention share across the SRG corpus, all operators, 139 mentions across 15 tools, colored by function
Tools & Services Ranked by Mention
Show table (15 rows)
| Tool or Service | Mentions | Use |
|---|---|---|
| Telegram | 49 | Agent coordination backbone |
| Zelle | 13 | Fiat payment |
| SpyCo | 10 | Custom tool by James |
| Zoom | 8 | Video pretexting |
| VPN | 8 | Access and OPSEC |
| ChatGPT | 8 | OSINT and research |
| ZoomInfo | 7 | Target recon |
| Rocket.Chat | 6 | Internal comms |
| RDP | 6 | Remote access |
| Google Drive | 5 | Exfiltration staging |
| AnyDesk | 5 | Remote access after vishingaccess |
| 3CX | 4 | Vishing phone system |
| SimpleX | 4 | Victim negotiation |
| Privnote | 3 | Credential sharing |
| Goldbear | 3 | Cash-out exchanger |
Telegram is the most-discussed tool, the backbone of agent coordination. AnyDesk is named only five times although it is the core access tool. It lives in the vishing script, not in daily chat.
Offensive and Access Tooling
The group does not use malware or a traditional command-and-control framework. A full-corpus search for C2 and offensive tool names returns nothing. There is no Cobalt Strike, no Sliver, no Metasploit, no Mimikatz, no stealer, and no remote access trojan. There is no exfiltration utility such as Rclone or WinSCP. This matches the known Luna Moth and Silent Ransom Group method. The intrusion is human-operated. An operator talks a victim into a remote-access session on a vishing call, then copies the data by hand to cloud storage.
The real tooling is short. It is remote-access software and one custom platform.
| Tool | Mentions | Type | Role |
|---|---|---|---|
| SpyCo | 11 | Custom in-house platform | Extortion case management, built and maintained by James |
| AnyDesk | 6 | Legitimate remote access | Hands-on-keyboard access after a vishing call |
| RDP | 6 | Legitimate remote access | Access to victim hosts |
| Zoho Assist | 2 | Legitimate remote access | Backup remote-access option |
SpyCo is the one proprietary tool. It is not an implant. It is a case-management platform for the extortion business. The chat shows per-victim records keyed to the pipeline stage, for example SPYCO_[victim-domain]_OFFER and SPYCO_[victim-domain]_CONTRACT. James fixed its deadline timers on 2026-05-19. The platform tracks the first CONTRACT and the GOLD close.
OSINT Tools
Henry used ChatGPT as an OSINT research tool. Multiple URLs in the chat carry utm_source=chatgpt.com parameters. Topics researched via ChatGPT include: law firm data breach settlements, New York military bases and installations, defense/aerospace manufacturing companies in NY/NJ/CT, and drone manufacturers.
AI-Assisted Operations
Confirmed: ChatGPT for OSINT
The operators use ChatGPT to research targets. The tell is the utm_source=chatgpt.com tag on links they paste, plus direct statements.
- Defense contractors: On 2026-04-02 in ARMA_PARTNERSHIP they shared a REDACTED defense-strategy link carrying
utm_source=chatgpt.com. Adrian, 2026-05-01: "надо спросить чат gpt" (need to ask ChatGPT). - Military bases and drone makers: On 2026-09-23 Henry pasted ChatGPT output on New York, New Jersey, and Connecticut. It named [REDACTED] military sites, and separated real UAV makers such as REDACTED from component suppliers. This fed the naval and defense HUMINT targeting.
- Payment-history research: On 2026-02-06 they pasted a ChatGPT table of law firms and the amounts those firms had paid before. This is extortion pressure research.
- Scope: The group’s AI footprint than peer groups such as The Gentlemen. The operators use one commercial tool, ChatGPT, for research. The data shows no other model, no uncensored local model, and no AI translation or image generation.
Technical Footprint by Operator
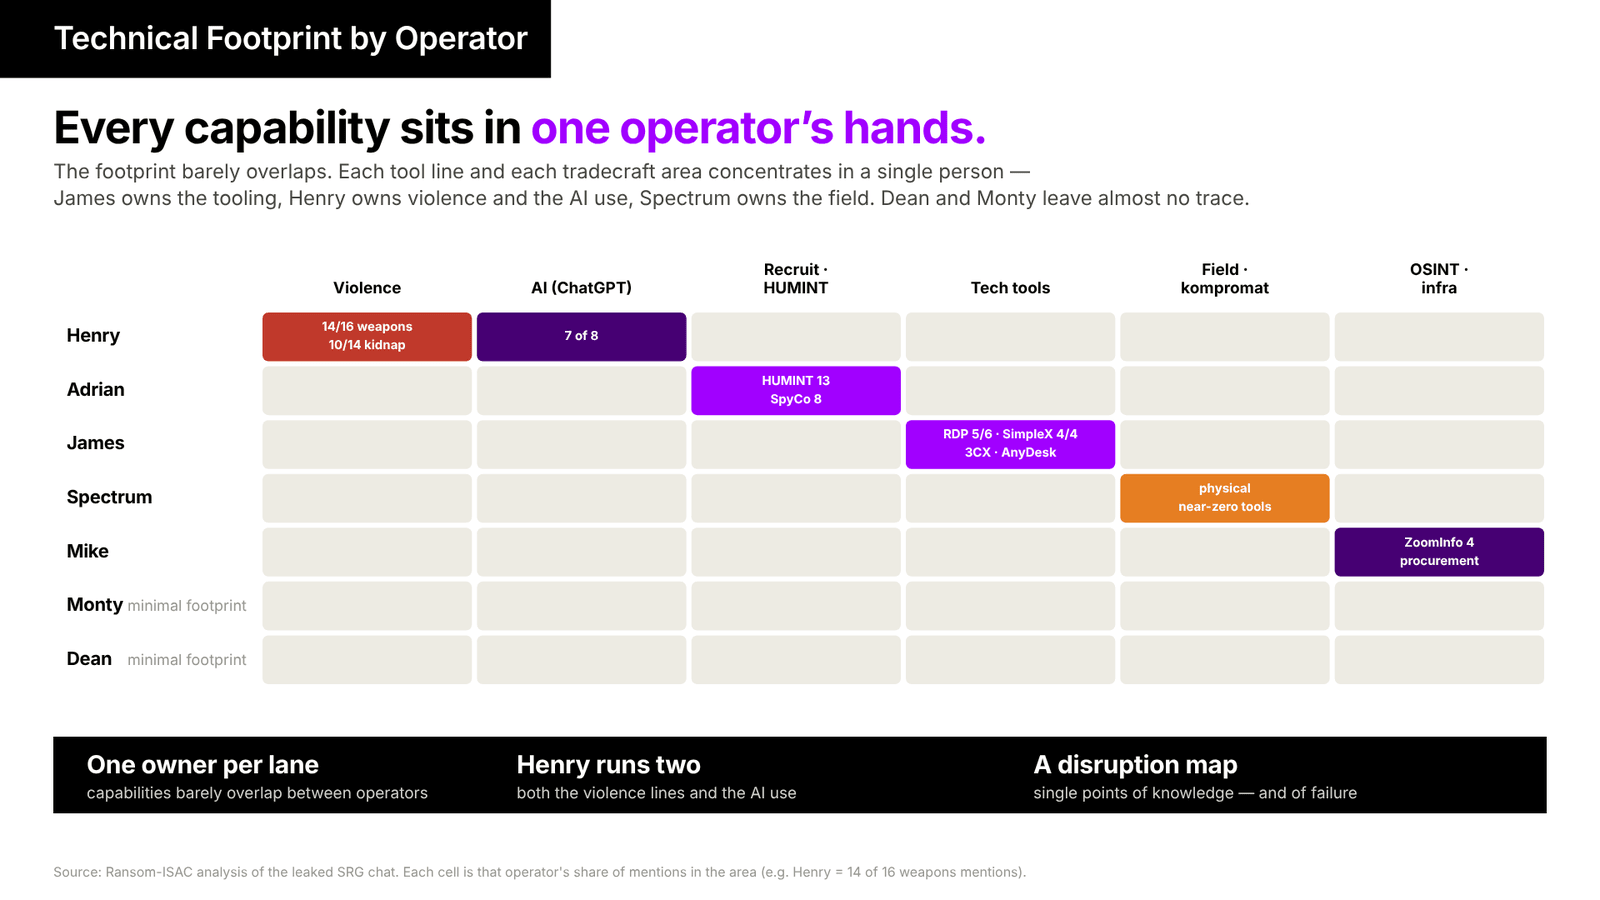
Technical Footprint by Operator: every capability sits in one operator's hands.
- Adrian: recruitment (HUMINT 13) and SpyCo (8), his 3 million dollar contract tool.
- Henry: the hub. He owns the violent lines (Weapons 14 of 16, Kidnapping 10 of 14) and the AI use (ChatGPT 7 of 8).
- Spectrum: field operations only. Physical and kompromat work. Near zero tools.
- James: the sole technical-tools operator. RDP 5 of 6, SimpleX 4 of 4, plus 3CX and AnyDesk.
- Mike: OSINT and procurement infrastructure. ZoomInfo 4.
- Dean and Monty: minimal technical footprint.
On-Chain Blockchain Analysis
Note: analysis performed on 2026-10-08 using the Blockstream API.
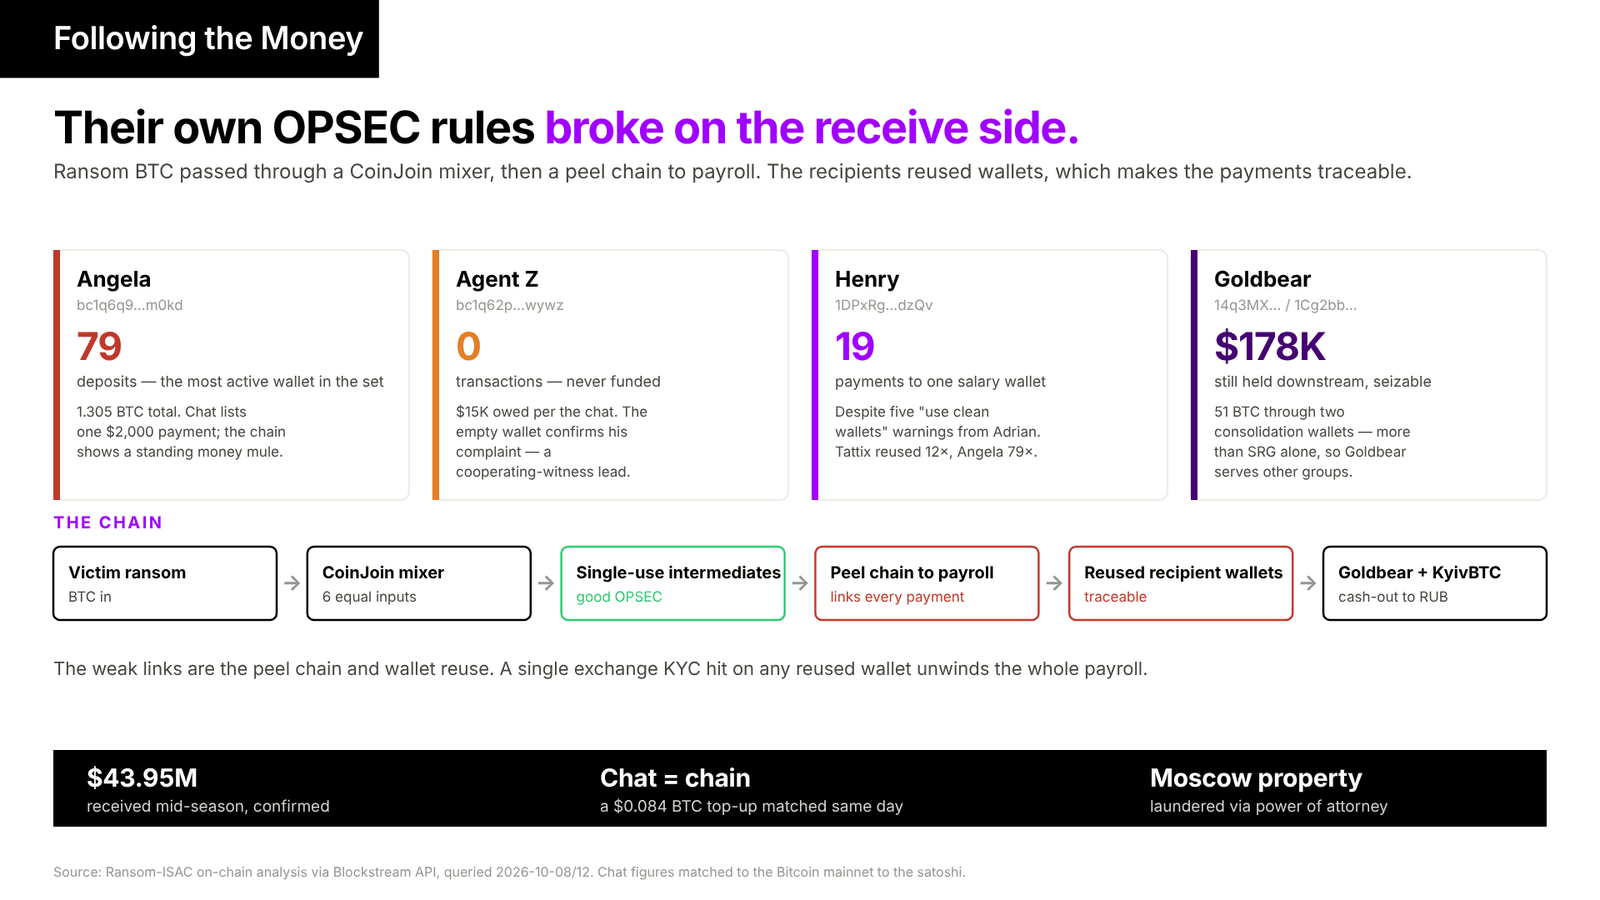
The key on-chain findings. The group mixed ransom BTC through CoinJoin, but recipients reused wallets heavily, which makes the payroll traceable. Angela, Agent Z, Henry, and Goldbear are the strongest law-enforcement leads.
All wallet addresses from the chat export were checked against the Bitcoin mainnet via the Blockstream API. Values are in satoshis (1 BTC = 100,000,000 sats).
Wallet Balances and Activity
Show table (14 rows)
| Owner | Wallet | Total Received (BTC) | Deposits | Balance (BTC) | Status |
|---|---|---|---|---|---|
| Angela (manager) | bc1q6q9ww5ddr7gculnmmqkvg8944f6ecmzqd4m0kd | 1.30489212 | 79 | 0.00339173 | Near empty |
| Goldbear (exchanger) | 1JAVjvoq5c6dGH6eeLTnx4DQYPf5omtGaN | 0.54397660 | 20 | 0.13230570 | Active balance |
| Henry (salary) | 1DPxRgDgP2aT9PqqSGYtQseHZVCQZQdzQv | 0.31496758 | 19 | 0 | Drained |
| Nur | 19A5zQ4YCUw8TMJBpFdyTT3DbKv6XFLN42 | 0.12158630 | 9 | 0 | Drained |
| Tattix / main agent | 15HP3kzUGTFQQuDfSqz85gvLz2h6si2evY | 0.11875422 | 12 | 0 | Drained |
| Mus | 15hm9UAGeAmq9f8itDMKg1b8BKwwzJnAUu | 0.09043776 | 8 | 0 | Drained |
| Henry (treasury top-up) | bc1qurppf5r2wtzxjjr0t6n2s2n299d3rgq3rl36rp | 0.08418923 | 2 | 0 | Matches the 2026-07-28 chat calc to the satoshi. Drained by 2026-08-19. |
| Henry (personal) | bc1qtahjyeej6z7k2vhad34g82e385gq49u3dsc848 | 0.06397578 | 1 | 0 | Drained |
| Rose | bc1qyw5m89wz49k5gddlssu9gu6n8njxyw06rqx9fn | 0.04051933 | 1 | 0 | Drained |
| FAKELAB | bc1q07rjleva5yturfc46qp762fxj05nt07nayyvte | 0.03954380 | 1 | 0 | Drained |
| Adrian (sent to) | bc1qej6ecmdvyl2c9rk8r7h25taq6amlktqs246m3q | 0.02625481 | 1 | 0 | Drained |
| Female operative (BTC side) | bc1qyfnwrxn0stuza077gs80xe544r3y4jwnwry2rv | 0.01761637 | 1 | 0 | Drained. Amount matches chat exactly. |
| Work Group X | 3PfKMnR2QBf2M9LbGH8wzF3c1BtA3Gf9Rr | 0.00350614 | 1 | 0 | Drained |
| Agent Z ($15K owed) | bc1q62pxr8sgc4jzhxsrw2f709d7ldfadhflrvwywz | 0 | 0 | 0 | Never funded |
Treasury Reconciliation and Chat-to-Chain Proof
One exchange shows the group's internal accounting and proves the chat ties to the blockchain. On 2026-07-28 in the Main command DM, Henry reconciled a Bitcoin float with Adrian. The screenshot below is Henry's clipboard.
Adrian had sent Henry 0.82179423 BTC. After Henry paid operator salaries and some advertising, 0.737605 BTC remained. The difference, 0.08418923 BTC, is the top-up Henry asked Adrian to send.
та сумма что ты мне прислал... минус то что осталось... надо было платить зп и прочее... и на рекламу немного
Translation: “that is the sum you sent me, minus what is left, had to pay salaries and other things, and a bit on advertising” Henry, 2026-07-28
Henry gave the receiving wallet bc1qurppf5r2wtzxjjr0t6n2s2n299d3rgq3rl36rp. Adrian replied "отправил Братик" (sent, bro) at 14:38 UTC.
According to Blockstream, that wallet received exactly 0.08418923 BTC in one transaction at 2026-07-28 15:40 UTC, the same day. The coins were later spent in full. The chat math, the screenshot, and the on-chain record agree to the satoshi. This is direct proof of the chat-to-chain method used across this section.
Money Laundering
Henry launders criminal proceeds into Russian real estate and a car, and states the concealment method in the chats while Adrian coaches.
The group turns Bitcoin extortion income into Moscow property and vehicles, then launders the source as savings, inheritance, a gift, or a fake loan agreement before a permanent move to Russia.
One Moscow address appears in the chat, Adrian 2026-05-05: Багратионовский проезд 7к3, Москва 121087.
- The plan:
- Henry, 2026-07-27: "буду там на недвижку еще откладываю... чтоб можно сдавать было... когда на постоянку приеду" (”I am setting money aside there for real estate, so I can rent it out, when I move there permanently”).
- He also buys a Moscow apartment for his grandmother and plans a Porsche 911.
- Hiding the source:
- Henry, 2026-08-06: "по доверености просил купить недвижку еще на мое имя. Там спрашивли происхождение средств в банке. Я сказал что можно выбрать опцию накопления" (”via power of attorney I bought more real estate in my name. The bank asked the source of funds. I said you can select the savings option”).
- The coaching:
- Adrian, 2026-08-06: "всегда спрашивают откуда деньги, можешь ставить наследство или подарок" (”they always ask where the money is from, you can put inheritance or gift”) and "сделай догвоор займа, это рабоатет" (make a loan agreement, that works).
- The channel: Henry prefers new-build developers that take money into escrow accounts, bought through a power of attorney.
Transaction Tailing
The wallets below received the most of the 52 Bitcoin addresses named in the chat. The chat does not establish what each address was used for, so a trail shows where money from that address went, not that all of it belonged to the group. Each trail follows the largest output at every step.
WALLET 1: bc1qrqt2n7tnx3znrnf0s9ctarxnp4j6l6z0cexsn9 [$536,741]
This case splits into two branches: a high-balance branch and a low-value split.
HIGH BRANCH
While tracing this Bitcoin Wallet, selecting 5.4 BTC branch.
Initial Out of the Wallet [HIGH BALANCED]
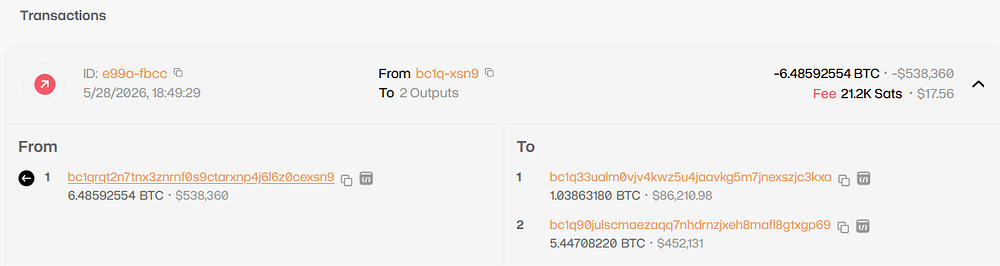
Initial Out of the Wallet [HIGH BALANCED]
A notable wallet appears here, one previously mapped to Akira Ransomware.
While tracking out the high balanced wallet (5.4BTC), we can see it further ends up in a high-frequency malicious wallet, which has been active since June 2021.
MALICIOUS WALLET:
bc1qng0keqn7cq6p8qdt4rjnzdxrygnzq7nd0pju8q
Final Out to the Wallet [HIGH BALANCED]
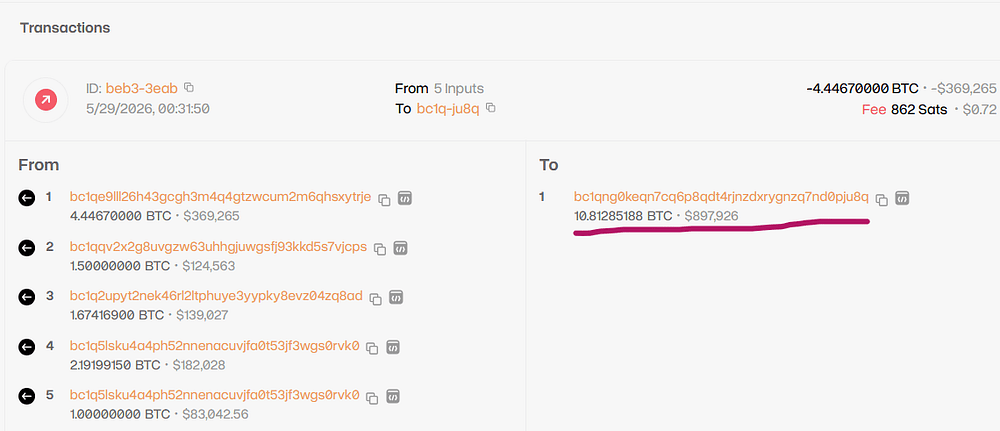
Final Out to the Wallet [HIGH BALANCED]
Apart from Akira Ransomware, it is also tied to Lockbit Ransomware 2025, specifically when the panel got exposed with along with internal chats and wallet addresses. The wallet belongs to WhiteMist, a malicious crypto exchange used for illicit purposes.
NOTE: This wallet is not directly linked to the Ransomware Players but a constant supported provided to Ransomware Groups over the years.
LOW BRANCH
While tailing the low wallet branch, its amounted figure is 1 BTC.
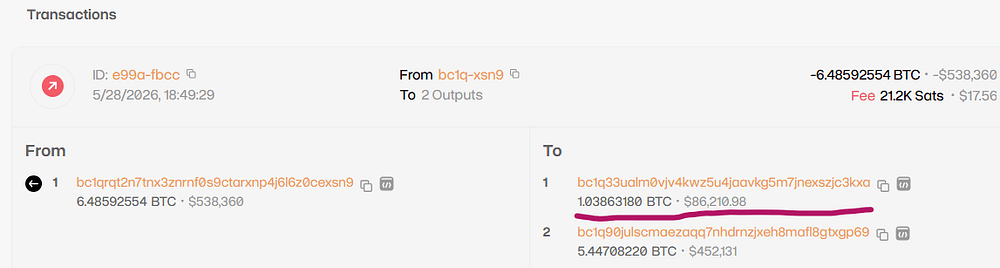
Transaction tailing of the low-value branch, which terminates at the 001K Bot service.
The final destination is the 001K Bot service identified earlier.
Final Out to the Wallet [LOW BALANCED]
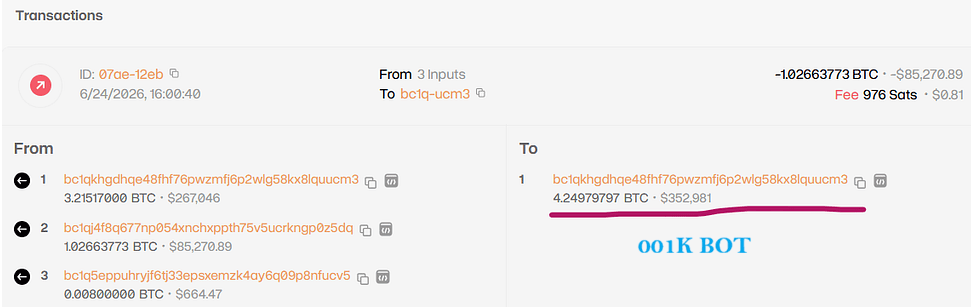
Final Out to the Wallet [LOW BALANCED]
WALLET 2: bc1qty6fppk4k475k64qahredmy0lrhwv00geqjnea [$112,644]
While transaction tailing the highest balanced wallet, it is found that the group finally transferred the hefty with a fee of $20 to the service [001K.BOT].
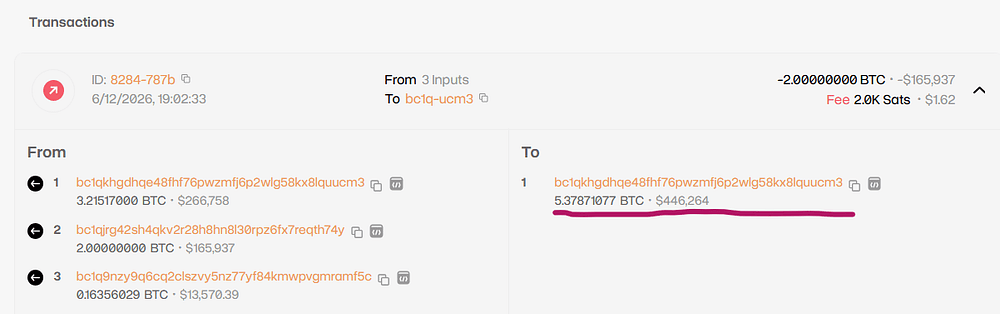
The highest-balance wallet's transfer into the 001K Bot service.
001K BOT: bc1qkhgdhqe48fhf76pwzmfj6p2wlg58kx8lquucm3
While checking the other branch/split, it is again found that the same deposit address is being used to dump all the money.
WALLET 3: bc1qqgsp70raz2xt72clpwry7hjdfcalysextu0vm7 [$301,702]
Similarly, following the high balanced trail, we can see the amount got split into 2. Hence, peeling 3.64 BTC Wallet:-
Initial Out of the Wallet [HIGH BALANCED]
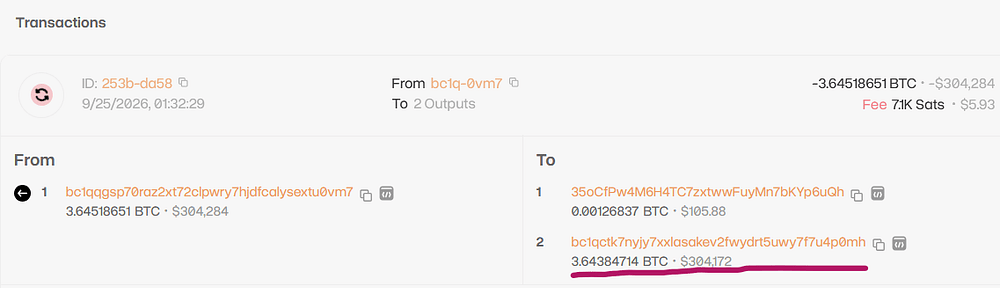
Initial Out of the Wallet [HIGH BALANCED]
The final peel is revealed to have deposited to 001K Bot Service.
Final Out to the Wallet [HIGH BALANCED]
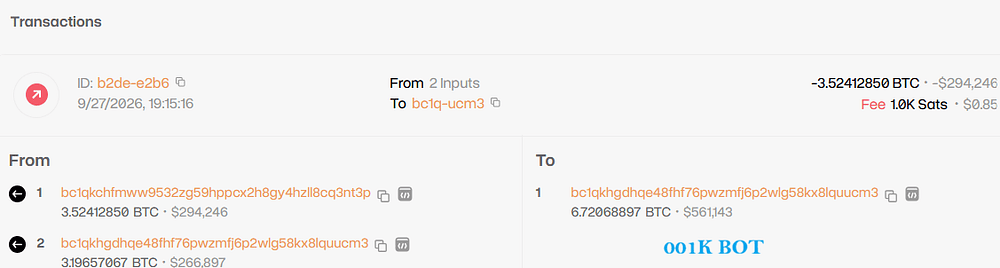
Final Out to the Wallet [HIGH BALANCED]
WALLET 4: bc1qpns7fuy6eaukumxtpd3t03uws68kk0z3ua4wps [$220,841]
This trail first runs through an intermediate wallet:
bc1qzrd5xagdarxmnnxaqus3q9qmjxvec32gqjy57j
The transaction is initially split between $5 and $222,672 in 2 Wallets.
Initial Out of the Wallet [HIGH BALANCED]
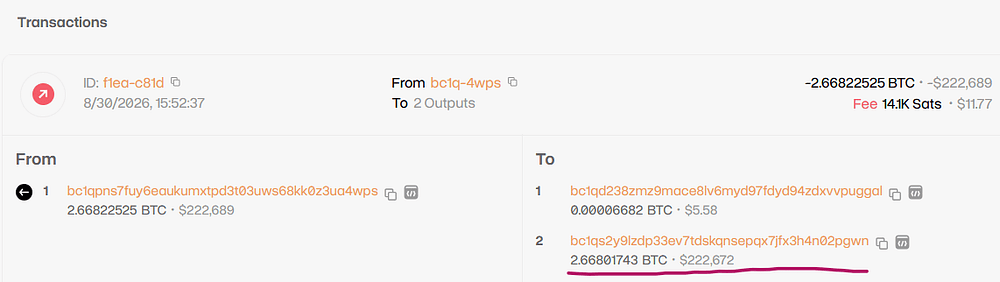
Initial Out of the Wallet [HIGH BALANCED]
Peeling this wallet also resulted in 001K Bot service at the final stage.
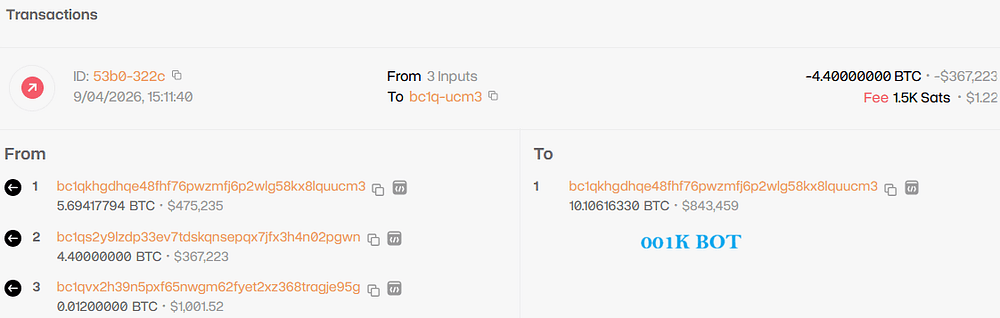
A 4.4 BTC transaction on 9 April 2026 into the 001K Bot BTC address.
WALLET 5: bc1qk6swlp3yarz8ghg4r093zuhtxxaw9gd5h8x20x: $83,878.43
Following similar steps, I found that this wallet deposited nearly 0.2BTC at the end to a HitBTC Hot Wallet: bc1qdfl3dfnwwvlqa5jpckh0ccwpjczh5y566c4g76which is again a malicious history of fraudulent transactions like Investment Scam, Vishing, Crypto Scams, Ledger Swap etc. It’s also notable that this address is again used in Sonic DEX Hack. The wallet has been active since June 2023.
WALLET 6: bc1qfl857h8wwv9yauynektfh8eahs3vj7x9h4xc0s: $60,813.38
This wallet differs from the others: its funds went to the following Bitcoin wallet, active since December 2024.
bc1qgslzx6wmddmrg0rfl5nfhdynvgtkp5wd8vyndl
OTHER WALLETS
One more wallet also ends at the 001K Bot service:
bc1qgyvjlkm7dg2he5rl0ce7gxngznuaewh860lghu : $107,526
Five of the seven traced wallets have a trail that ends at the deposit address 001K publishes itself. That makes 001K the main cash-out point in this data (Possible). The other large addresses named in the chat were not traced.
LEGACY WALLETS
- 1DPxRgDgP2aT9PqqSGYtQseHZVCQZQdzQv : $26,050.42 found to be deposited the whole amount to 17Hh59K259oHaMtSfeJh9UmkV4seDAQe7x which is active since January 2026
- 1JAVjvoq5c6dGH6eeLTnx4DQYPf5omtGaN : received $44,991.36 and sent most of its funds to another wallet address: 12XZMdaAGmcHf4ocFSqpd8jFd1WH7RHUPs, which is a ByBit Hot Wallet. It still holds 0.13230570 BTC.
001K BOT SERVICE
001K Bot is an automated crypto-cash service with links to the Russian financial system as per BitQuery:
“A custodial crypto-financial platform designed for fast digital asset management, payments, and token swaps rather than complex trading terminals or decentralized finance (DeFi) tools”
https://001k[.]bot/wallets
Same BTC Address publicized by 001K
The domain was registered in April 2024, but the service is older, with Telegram channels dating to September 2023.
Telegram Channel
Telegram Channel
The administrator remains active, as shown by the fresh funds still arriving at the service's Bitcoin wallet.
Instagram Account
Instagram Account
The service claims to offer AML support, but its transactions show otherwise.
001 K Bot Admin
001 K Bot Admin
The service also advertises on other platforms, including Instagram.
001K BOT: MALICIOUS ACTIVITIES
There are various instances where 001K Bot involved in numerous scams and other malicious activities including Ransomware, SCAM, Ponzi etc.
GOLDEN WAY PONZI: A Multi-Level-Marketing for investing on Gold through their platform. According to Decripto, 001K Bot was involved in the $90M Scam in 2024.
DMYTRO SHEVCHUK: Dmytro Shevchuk is a public trader who had a long time reputation as a successful trader across various platforms. Investors were offered Fund Management starting from $10 at 6% monthly interest and ended up on the scam. He also sold “mentoring” programs, according to an investigation by how2onchain.
001K BOT Activity tied to Telegram Deposit
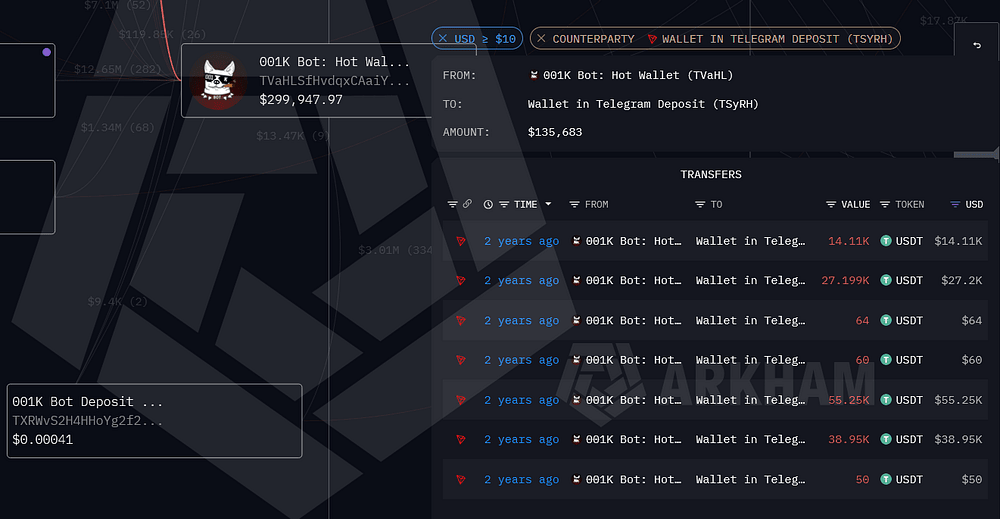
001K BOT Activity tied to Telegram Deposit
Shevchuk had found to be deposited $230K to this Service, as per an investigation.
Public reporting and forum activity show a consistent pattern of use across these actors. All types of illicit activities which are mentioned above uses this service to lose the money trail, marking a dead-end for the investigators.
Key On-Chain Findings
1. Angela is the biggest wallet, not a $2,000 agent.
The chat describes Angela as a "manager/oper who controls the process" with a single $2,000 payment. But her wallet received 79 deposits and 1.30 BTC total. This is the most active recipient address in the dataset. Angela is likely a primary money mule or operational coordinator who receives regular payments for ongoing work. The 79 deposits suggest weekly or near-daily funding.
2. Agent Z was never paid.
Henry's September 2026 ledger requests $15,000 for Agent Z to wallet bc1q62pxr8sgc4jzhxsrw2f709d7ldfadhflrvwywz. This wallet has zero transactions on-chain. Z's complaint in chat ("I was supposed to get 10k monthly" and "I didn't get the 5k from before") is confirmed by the blockchain. Adrian never sent the funds.
3. Henry reused his salary wallet 19 times.
Despite Adrian's five separate warnings to use clean wallets, Henry received 19 payments to the same 1DPxRgDgP2aT9PqqSGYtQseHZVCQZQdzQv address. Tattix reused their wallet 12 times. Angela reused 79 times. The OPSEC discipline is one-directional: Adrian follows it on the send side (single-use intermediates) but the recipients ignore it.
4. Goldbear exchanger still holds 0.13 BTC.
1JAVjvoq5c6dGH6eeLTnx4DQYPf5omtGaN has a live balance of 0.13230570 BTC. This wallet had 20 deposits and 39 total transactions. It is actively used as an exchange or broker.
CoinJoin / Mixer Detection
The December 2025 funding transaction that paid all 8 agents has a clear CoinJoin signature.
Transaction 9f0fba450da09e63a0536153470f73f51936970a61485d491448ee6ca86abef1 funded Adrian's payment source wallet. It combined 6 inputs with identical values:
| Input Address | Amount (sats) |
|---|---|
bc1q4wtujhq4vgns8kzy2ut5r58ztm7cxgfx093jwd | 5,666,201 |
bc1qzqlswr8g5rqmuf8wmt78lu3hmamxw4qehcw58j | 5,666,201 |
bc1qfxk3eelkzm0q2xu7am9048gphujfejskgmmx2q | 5,666,201 |
bc1qhu4r7599cy7hpysnrnn27unsctw8gr6kgmkt4c | 5,666,201 |
bc1qx6t9hr25rg4m6cfv6pmcy5lsn67jz32esk6mzj | 5,666,201 |
bc1q42y26t5jqe3nln8qdqqz46xt89eqy62h53myec | 5,666,201 |
Six identical input values is the signature of a CoinJoin mixing protocol (Wasabi Wallet, JoinMarket, or similar). The ransom BTC passed through a mixer before Adrian distributed it as payroll. This is the anti-tracing step Adrian refers to in his OPSEC warnings.
The three outputs of this mixing transaction:
bc1qt3yarf7fvxvvddwy4jm5y8ahs5323xghjgf290(22,369,568 sats) = Adrian's payment sourcebc1qd528kl5ah68aa2sw6y6343q627gtsz9s8mkcdz(10,862,653 sats) = separate fundbc1qvlf5z6jel4z9e89q8znrtpqhtw448q466azmx9(707,085 sats) = fee or small output
Peel Chain (December 2025 Payment Distribution)
Adrian distributed the December 2025 agent payments in a peel chain. Each payment uses the change from the previous transaction as input for the next. This links all payments on-chain:
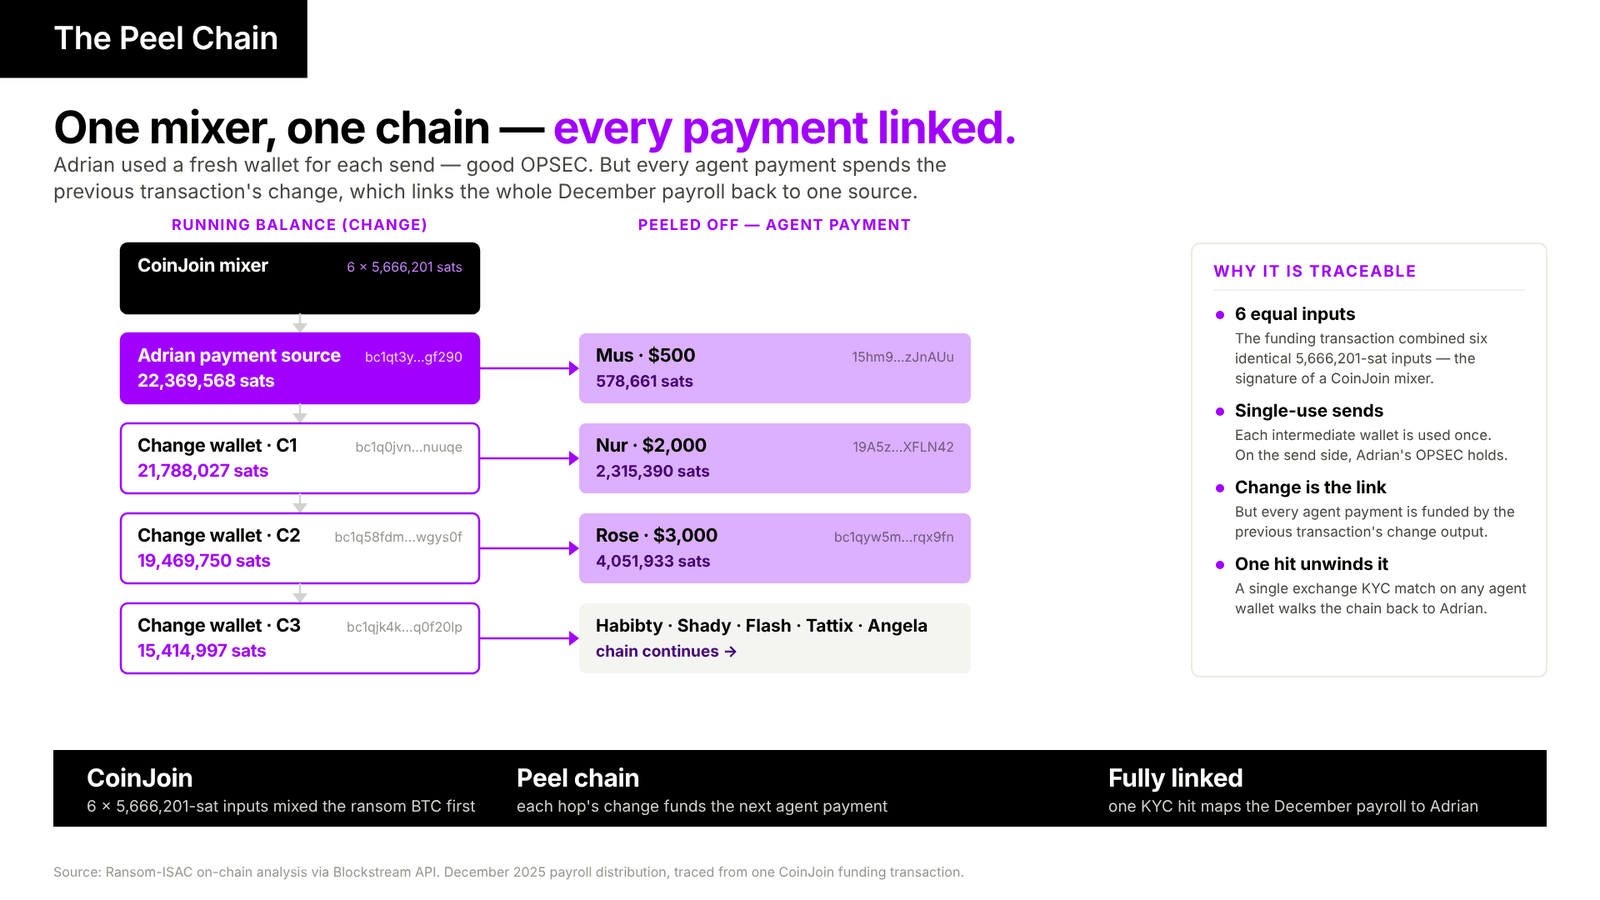
The December 2025 payroll peel chain. One CoinJoin funding transaction (six equal inputs) feeds Adrian's source wallet. Each agent payment peels off while the change funds the next, chaining every payment to one source.
Each link in this chain is confirmed on-chain. Adrian instructed agents not to mix wallets. The peel chain defeats that rule. A blockchain analyst can follow each change output and link all agent payments to the same CoinJoin source.
September 2026 Source Wallet
The September 2026 Dean salary payment traces upstream:
- Source:
bc1qhts2vkdusa5x0rpcdakaqx85hwqzpsdgwjpues(single-use, 0.03751343 BTC) - Intermediate:
bc1q47hq52yckx7dsydkdsf73j5vrtd8xkq6p44yfu(single-use, 0.02989555 BTC) - Destination:
1DPxRgDgP2aT9PqqSGYtQseHZVCQZQdzQv(Henry salary, 0.01753073 BTC)
Unlike the December 2025 source, this wallet has no CoinJoin signature. It received a single deposit and spent it once. This represents a different Adrian treasury or a post-mixer intermediate.
Tracing Summary
The full financial chain is:
- Ransom payments from victims (BTC)
- CoinJoin mixer (6 equal-value outputs confirmed in Dec 2025)
- Adrian's single-use intermediate wallets (good OPSEC, single deposit and single spend)
- Peel chain distribution to agents (bad OPSEC, links payments together)
- Recipient wallets (bad OPSEC, heavy address reuse by Angela, Henry, and Tattix)
- Cash-out via Goldbear exchanger to
14q3MXjwc5CN6uNFXDm585XZSYCTgTdzGP(13 BTC, $167K remaining) and KyivBTC for RUB
The weakest links for law enforcement tracing are steps 4 and 5. The peel chain links all agent payments. Angela's 79-deposit wallet, Henry's 19-deposit wallet, and Tattix's 12-deposit wallet all violate the group's own OPSEC rules and are fully traceable.
Downstream Exchange Network
The Goldbear exchanger feeds into two large consolidation wallets. These wallets processed far more BTC than the SRG chat accounts for, which means Goldbear serves other clients.
| Wallet | Total Received (BTC) | Deposits | Total TXs | Balance (BTC) |
|---|---|---|---|---|
14q3MXjwc5CN6uNFXDm585XZSYCTgTdzGP | 13.00429425 | 116 | 208 | 1.67673074 (~$167,673) |
1Cg2bb48P8D3rvF9fipbcxaStSjpo8PPFr | 38.09120827 | 102 | 202 | 0.11048770 (~$11,049) |
| Combined | 51.09550252 (~$5.1M) | 218 | 410 | 1.78721844 (~$178,722) |
Intelligence value. These two wallets are not SRG property. They belong to the Goldbear exchange service. Their 51 BTC total throughput far exceeds the SRG payments shown in the chat. Goldbear processes BTC-to-cash for multiple threat actor groups. Law enforcement can use these addresses to identify other Goldbear clients.
Updated Wallet Table (All Reused Wallets)
Several wallets that appear in the chat as one-time payments are reused far more than the chat shows:
| Owner | Wallet | Chat Says | On-Chain Deposits | On-Chain Total (BTC) |
|---|---|---|---|---|
| Angela (manager) | bc1q6q9ww5ddr7gculnmmqkvg8944f6ecmzqd4m0kd | 1 payment, $2,000 | 79 | 1.305 |
| Goldbear (exchanger) | 1JAVjvoq5c6dGH6eeLTnx4DQYPf5omtGaN | Exchange address | 20 | 0.544 |
| Henry (salary) | 1DPxRgDgP2aT9PqqSGYtQseHZVCQZQdzQv | Monthly salary | 19 | 0.315 |
| Tattix (agent) | 15HP3kzUGTFQQuDfSqz85gvLz2h6si2evY | $350/month | 12 | 0.119 |
| Nur | 19A5zQ4YCUw8TMJBpFdyTT3DbKv6XFLN42 | 1 payment, $2,000 | 9 | 0.122 |
| Mus | 15hm9UAGeAmq9f8itDMKg1b8BKwwzJnAUu | 1 payment, $500 | 8 | 0.090 |
Angela, Nur, and Mus each received far more payments than the chat leak shows. The chat covers only one payment cycle. On-chain data shows these wallets process payments across many months. Angela's 79 deposits mark her as the most active financial participant in the network.
FAKELAB Cash-Out (Analyst Observation)
FAKELAB moves little money, but the method is deliberate. The forger appears to cash out its own proceeds through drop accounts on the HitBTC exchange, rather than under its own name. A large share of its funds also routes through Kraken Darknet Market, split across two separate paths. That split spreads risk and limits exposure on any single route, which points to an operator who manages funds with care, not an amateur. This observation comes from a contributing analyst and is not independently confirmed in the leaked corpus. The HitBTC nexus is consistent with the HitBTC hot-wallet cash-out already noted in the Transaction Tailing section above.
*On-chain data queried 2026-10-08 via Blockstream API (blockstream.info/api). All wallet balances and transaction counts are current as of this date.*
Warning Signs for Target Organizations
This section lists the tells for staff of organizations who are likely valuable targets for SRG (with special regards to law firms). The first person to come into contact with an agent is a front-facing employee such as a receptionist, a partner, or a general counsel, not the security team. Detection and Hunting below covers the log and endpoint side. This section covers the human side.
IT Impersonation Phone Scam (All Employees)
This impersonation involves a phone call which impersonates the target organization’s own IT department.
Suggested templates found in chats:
- "Hello. This is REDACTED FIRM IT Department, connecting you to the IT specialist , [name withheld]".
- "Hello. This is REDACTED FIRM IT Department, connecting you to the IT specialist , [name withheld]".
The caller impersonates an “IT Specialist” and uses the target firm’s name. The internal TA script coaches a warm and familiar tone, coaching agents to introduce themselves briefly, name the department as IT, and to ask how the person is doing, as if they know them. The caller asks the target to install or open a remote-access tool, then read out the connection code.
Watch for these signals:
- A cold call from "IT" about a problem you did not report.
- A request to install AnyDesk, Zoho Assist, Splashtop, or TeamViewer.
- A request to read back a numeric connection or access code.
- Pressure to act during the call, before you can verify the caller.
The call runs in a fixed order. You may hear these beats:
- "We detected suspicious activity on your device."
- "Did you get an email with a PDF?" You say no. "Good, we blocked it." This is false relief.
- "But other employees clicked it, so the network is now compromised." This re-raises the fear.
- "I know you would never click something like that." This fakes trust, and it implies they watch you.
- "I need to run a security check by remote access." This is the moment of compromise.
- "Leave your computer on for a day for the update." Then: "Save my number in case you need help."
The Business Inquiry: Reception, Intake, and Client-Facing Staff
A fake client or partner asks you to review a document that only opens in a remote session. Henry: "so for them to check out our order or partnership contract they will have to do it via zoho". The group also targets insurance and healthcare with a benefits pretext. It asks to reach "someone higher than a regular phone agent". The tell is a new counterparty who needs you to screen-share or install software to view an order, a contract, or a quote.
The Front Door: Reception, Security, and Facilities
The group uses the phone to clear a visitor into the building. One operator described it: "i call the reception and pretend im a lawyer in that corp who ordered pizza, so the reception lets the agent goes in". They also plan in-person visits as clients, carrying a USB drive with AnyDesk on it. The tell is a delivery or a visitor approved by a phone call from an unverified employee.
The Extortion Email: General Counsel, Partners, and Executives
The first email carries real samples of your stolen data as proof. The sender then moves you off email fast, to ProtonMail and then to SimpleX chat. The deadline is short and hard. The internal instruction was blunt: "скажи у них меньше суток что бы ответить - иначе сольем" (tell them they have under a day to answer, or we leak). A victim-facing message read: "You have 48 hours to respond , or we will attack you once more and take more data." The demand is pay to suppress, not pay to decrypt. It anchors at seven figures or more, and the group does not haggle. Firms that refuse get posted in public.
The Escalation: Senior Staff and Their Protection
For a target who refuses, the group discusses physical coercion in the chat. The plan named surveillance, a van, a staged kidnapping, a gun, and a fake syringe. The goal was to force a victim to open a remote session to a work PC. The record notes that the victim "can even call someone at the office to give him access". This is planning talk, not a confirmed act. It is in the corpus, and it is aimed at the senior people who hold the data.
Who They Target
Law firms come first, chosen by role. The working vocabulary is partner and officer, the senior staff who can approve a payment. Recon runs through ZoomInfo. Named firms in the call scripts and records include REDACTED FIRM, REDACTED FIRM, and REDACTED FIRM. Insurance and healthcare firms are a secondary line, reached through the employee-benefits pretext.
First Move If You Suspect It
- If a caller claims to be IT, hang up. Call back on a known internal number before you act.
- Do not install any remote-access tool, and do not read out any code to a caller.
- If an extortion email arrives, do not reply. Preserve it, and tell your general counsel and incident response team at once.
Detection and Hunting Guidance
The SRG attack chain starts with social engineering as opposed to a software exploit. Therefore, detection must target the human access vector, as well as the remote access tool and cloud exfiltration step.
The three highest-value detection points are:
- AnyDesk (or any unsanctioned remote access tool) first seen on a host, close in time to an inbound external call. This catches the attack at the moment of compromise.
- Bulk upload to consumer cloud storage from a legal or finance workstation. This catches the exfiltration step.
- A reported suspicious call from "IT" that asks for remote access. This catches the attack before compromise and costs nothing but training.
Callback Phishing (Vishing) Detection
The attack starts one of two ways. The group sends an email with a PDF and a callback phone number. Or the group calls the employee and claims to be internal IT.
Email gateway rules:
- Flag inbound email with a PDF attachment that contains a phone number and little other business context. This is the callback phishing lure.
- Flag PDF attachments with an embedded phone number sent from a free email domain (gmail.com, proton.me).
- Flag email that tells the reader to call a number about a subscription, a charge, or a security alert.
User reporting:
- Train staff that internal IT does not ask for remote access through an unsolicited call.
- Set a rule: any caller who claims to be IT must be confirmed through a known internal number before the employee acts.
- Give staff a fast way to report a suspicious call. The group relies on employee trust, so a reported call is an early warning.
Remote Access Tool Detection (AnyDesk)
After the call, the caller tells the employee to install AnyDesk. This is the point of compromise. AnyDesk is the highest-value detection point in the whole chain.
Endpoint rules:
- Alert on AnyDesk.exe first seen on a host, especially when it runs from Downloads or a temp folder.
- Alert on any remote access tool that is not standard for the environment: AnyDesk, TeamViewer, Zoho Assist, Splashtop, ScreenConnect.
- Correlate the install time against phone and email logs. An AnyDesk install within 30 minutes of an inbound external call is a strong indicator.
- Alert when a remote access tool runs on a finance, legal, or executive assistant workstation. These are the group's preferred targets.
Network rules:
- If AnyDesk is not sanctioned, alert on outbound traffic to AnyDesk relay infrastructure.
- Block unsanctioned remote access tools at the proxy where possible.
Exfiltration Detection (Cloud Storage)
The group copies data to consumer cloud accounts. The report documents four Google Drive accounts at 100 GB each, plus Yandex Disk links.
- Alert on bulk outbound uploads to consumer Google Drive, Yandex Disk (yadi.sk), and similar services from workstations, especially from legal and finance staff.
- Alert on rclone.exe, WinSCP, or a MEGA client on endpoints where they are not expected.
- Flag large archive creation (.zip, .7z, .rar) on a file server followed by an outbound transfer.
- Watch for a single workstation that reads a large volume of files across many shares in a short window. This is staging before exfiltration.
Infrastructural Indicators
Block or alert on the known infrastructure from the IOC appendix.
- 3CX PBX vishing phone system: 87.251.67[.]222, 87.251.67[.]223 (Netherlands).
- SimpleX Chat and ProtonMail contact in any inbound extortion email.
- The group's fake pretext domains. See Appendix A.
- The [.]onion leak site. See Appendix A.
Fake Employee and Insider Detection
The group places operatives in remote IT help desk roles at defense contractors and tech firms. This is a hiring threat, not a network threat.
Human resources checks:
- Verify the work history of remote IT candidates with the stated employer directly, not through contact details on the resume.
- Flag candidates whose resume was built in Canva and whose certifications cannot be confirmed with the issuer.
- Flag a mismatch between a candidate's claimed location and their network location during interviews or onboarding.
- Apply the published guidance on North Korean IT worker fraud. The group copies that playbook.
Technical checks:
- Flag a new remote hire who connects through a residential proxy or a location-hiding VPN.
- Flag a new hire who asks for access beyond their role in the first weeks.
Additional Detections
Four additional controls below, each one mapping to a confirmed part of the group's tradecraft:
- Privnote. Alert on any host that contacts
privnote[.]com. The group uses Privnote to share one-time secrets. Attackers also use the service to deliver RMM tools to on-premises hosts and VDIs. - iManage repositories. Monitor internal iManage repositories for a mass keyword search that is followed by a bulk export or by email forwarding. Law firms and corporate legal departments use iManage to manage matters, files, and communications, so it is a primary exfiltration target for this group.
- VDI authentication. Allow only corporate-owned devices to authenticate to the Virtual Desktop Infrastructure (VDI). This control blocks access from an operative's own device.
- USB storage. Disable read and write access to external USB storage. Enforce the restriction with Group Policy Objects (GPO) or an MDM configuration. This control counters in-person IT impersonation and USB-based data theft.
MITRE ATT&CK Mapping
Show table (15 rows)
| Tactic | Technique | Evidence |
|---|---|---|
| Reconnaissance | T1598, Phishing for Information | Vishing calls to gather employee trust |
| Reconnaissance | T1593, Search Open Websites | ZoomInfo and RocketReach for employee OSINT |
| Resource Dev | T1585, Establish Accounts | Gmail, Google Drive, and Zoom accounts for cover |
| Resource Dev | T1583, Acquire Infrastructure | Self-hosted Rocket.Chat, SSH/RDP, 3CX PBX |
| Initial Access | T1566.004, Spearphishing Voice | Full vishing call script recovered |
| Initial Access | T1078, Valid Accounts | Purchased victim credentials ($4,100 each) |
| Execution | T1219, Remote Access Software | AnyDesk and Zoho Assist deployed via vishing |
| Persistence | T1078, Valid Accounts | Fake employee placement at REDACTED CYBERWARFARE COMPANY, REDACTED CYBERWARFARE COMPANY |
| Collection | T1005, Data from Local System | Law firm data exfiltration for extortion |
| Exfiltration | T1567.002, Exfil to Cloud Storage | 4 Google Drive accounts (100 GB each) |
| Impact | T1657, Financial Theft | BTC ransom payments |
| Reconnaissance | T1591.004, Employee Names | Executive target lists with names, titles, emails, and direct phone numbers for 15+ firms |
| Resource Dev | T1588.002, Obtain Capabilities: Tool | ChatGPT for OSINT, SpyCo custom tool, AnyDesk, card skimmers |
| Initial Access | T1200, Hardware Additions | Card skimmers for building access. AnyDesk on USB for client impersonation. |
| Resource Dev | T1597, Search Closed Sources | ZoomInfo for network size and AV/EDR recon (REDACTED FIRM 2: withheld, REDACTED INSURANCE: 12K hosts) |
Appendix A: Consolidated IOC Registry
All indicators extracted from the chat export, verified against the source data. Grouped by type for machine ingestion.
Network Infrastructure
IP Addresses
| Type | Indicator | Context |
|---|---|---|
| IP | 87.251.67[.]222 | 3CX PBX vishing phone system (Netherlands) |
| IP | 87.251.67[.]223 | 3CX PBX vishing phone system (Netherlands) |
| IP | 45.32.232[.]133:2895 | Sleepless Threat RDP work server ("SLEEPLESS RDP WORK") |
| IP | [REDACTED] | Stolen X/Twitter RDP access server (Admin) |
| IP | 199.217.98[.]21 | (600 GB, 1 month lease) |
| IP | 216.203.20[.]157 | (600 GB, 1 month lease) |
| IP | [REDACTED] | Purchased access: REDACTED INSURANCE VPN |
| IP | [REDACTED] | Purchased access: REDACTED ANNUITY PROVIDER VPN |
Domains
Show table (17 rows)
| Domain | Purpose | Registrant Context |
|---|---|---|
aim6umein3kee[.]com | Primary Rocket.Chat server | 5,458 messages, Aug 2025 to Sep 2026 |
slplsskdj2836v2jjsx[.]com | Secondary Rocket.Chat (Sleepless Threat) | 234 messages, Sep 2026 |
exploitivzcm5dawzhe6c32bbylyggbjvh5dyvsvb5lkuz5ptmunkmqd[.]onion | Sleepless Threat Tor leak site | Shared by Henry |
sokolovsky-law[.]com | Fake law firm (social engineering) | Email: oleg.sokolovsky@sokolovsky-law[.]com |
ominetdata[.]com | Fake data company (cloned from evaboot.com) | Email: f.miller@ominetdata[.]com |
develevenor[.]com | Fake identity domain | Two actor mailboxes created |
funconnect[.]com | Fake identity domain | Email: m.gonzales@funconnect[.]com |
redacted-it[.]com | Deepfake impersonation domain | Impersonates REDACTED LLP IT dept |
sdfmskfd[.]com | Fake data breach news site | Used by James for disinformation. James told an agent: "like we detected that on website sdfmskfd[.]com just leaked new company names as REDACTED FIRM" (2026-09-24) |
sleeplessthreat[.]com | Rebrand domain | ST public-facing identity |
ThreatActorsNeverSleep[.]com | Considered rebrand domain | Not confirmed active |
sleepless[.]co | Considered rebrand domain ($18,410) | Premium domain, may not have been purchased |
myrecovery[.]casa | Recovery email domain for Google accounts | All 4 exfil Drive accounts use this domain |
it-REDACTED[.]com | Fake IT support domain | Impersonates REDACTED LLP |
REDACTED-law.com | Fake law firm domain | Impersonates REDA |
thesiliconemasters[.]com | Social engineering cover domain | Referenced in SPR_TRG_TALK |
newyorkhvacinc[.]com | HVAC cover company domain | Physical infiltration cover identity |
Actor Network
Email Addresses
Show table (12 rows)
Email (hosted on privateemail.com) | Purpose |
|---|---|
sokolovsky-law[.]com, oleg.sokolovsky@sokolovsky-law[.]com | Fake lawyer identity |
ominetdata[.]com, f.miller@ominetdata[.]com | Fake data company identity, cloned from evaboot.com |
develevenor[.]com, a.shultz@develevenor[.]com | Fake identity (credentials on file) |
develevenor[.]com, f.dominguez@develevenor[.]com | Fake identity (credentials on file) |
m.gonzales@funconnect[.]com | Fake identity |
myrrtaspenbi1976@rambler[.]ru | Stolen X/Twitter account recovery email |
pearsonterry15@gmail[.]com | Google Drive exfil account 1 |
salvadorchavapizano@gmail[.]com | Google Drive exfil account 2 |
caballerojeff91@gmail[.]com | Google Drive exfil account 3 |
happyclassroomtutoring@gmail[.]com | Google Drive exfil account 4 |
kybuggy2@gmail[.]com | Zoom account for video pretexting, recovery: kybuggy914[at]myrecovery[.]casa |
juandiego20995@gmail[.]com | Fake employee resume identity, • Phone: 813-679-0011 |
Canva Design IDs: DAF1L-FVgTE, BAFtZXrKf1A |
sdvbsbdsndmks55@gmail[.]com | Actor operational email |
|---|---|
BledarMurillo687@gmail[.]com | Actor operational email |
anohin77777777@gmail[.]com | Actor operational email (Henry) |
[at]myrecovery[.]casa | All recovery emails, TOTP 2FA backup codes on file. |
150+ additional victim employee emails (law firm staff) were harvested from corporate directories for vishing campaigns. These are documented in the full chat export.
Telegram Handles
Show table (15 rows)
| Handle | Identity |
|---|---|
@xyz000zz | Fake ID maker |
@woodythedoo | Monty (ST handle) |
@MoeSolnce1010 | OJ (physical operations, work van) |
@DD_party1 | Dean |
@Jackonda12 | Agent contact |
@SAFUexchange | Crypto exchange contact |
@david_ernand | David (LA operative, codename 0037) |
@jevan2333 | Jevan (IL operative, codename 0026, caught) |
@sergiinyvlaso | Sergii (NY operative, codename 104) |
@givingbunny | Lex (NY operative, codename 0044) |
@denzelwg https://web.telegram.org/a/#8655218493 | Agent contact (Goldbear |
@linaqqo | Agent contact (Henry's reference) |
@[handle withheld] | Agent contact |
@seblabyt | Agent contact |
@hernandezemily6y065 | Actor alias |
Telegram Coordination Groups
Henry shared seven invite links to region-based actor coordination chats. The links are withheld from this public release.
SimpleX Chat Handles (Ransom Negotiations)
new2-th1s-talk(REDACTED FIRM 3 negotiation)mutagenic(REDACTED FIRM 4 negotiation)
Financial IOCs
BTC Wallets
All wallet addresses with on-chain verification are documented in the On-Chain Blockchain Analysis section above. Key wallets for law enforcement action:
| Wallet | Owner | Action |
|---|---|---|
14q3MXjwc5CN6uNFXDm585XZSYCTgTdzGP | Goldbear downstream 1 | Seize: $167K balance |
1Cg2bb48P8D3rvF9fipbcxaStSjpo8PPFr | Goldbear downstream 2 | Seize: $11K balance |
1JAVjvoq5c6dGH6eeLTnx4DQYPf5omtGaN | Goldbear exchanger | Seize: 0.13 BTC balance |
bc1q6q9ww5ddr7gculnmmqkvg8944f6ecmzqd4m0kd | Angela (79 deposits) | Subpoena: exchange KYC records |
1DPxRgDgP2aT9PqqSGYtQseHZVCQZQdzQv | Henry salary (19 deposits) | Subpoena: exchange KYC records |
bc1qurppf5r2wtzxjjr0t6n2s2n299d3rgq3rl36rp | Henry treasury top-up (0.08418923 BTC, 2026-07-28) | Trace downstream: received then spent, chat-confirmed |
bc1q62pxr8sgc4jzhxsrw2f709d7ldfadhflrvwywz | Agent Z (never funded) | Cooperating witness lead |
Exfiltration Storage
Google Drive Shared Folders
Adrian shared eight Google Drive folders that hold exfiltrated victim data. The links are withheld from this public release.
Yandex Disk Links
Adrian shared six Yandex Disk links for operational files. The links are withheld from this public release.
File Hashes
| File | SHA256 |
|---|---|
chat_export_full.json.gz | 41900fbcc8a172629c695bba46ad15b7981610ea52d3a61ab4061fd6d860e809 |
target_list_naval_bases.xlsx | 4bee44ec615b61d6f1acdb4b3d92497f9f200757f4b6653068dce23a9f100d4f |
fake_employee_resume.pdf | a6a580e4aff45d4812123eb18ec7bd1c53f44b3369e3b430d7b72f4cdb30778e |
vishing_call_script.txt | d2f3a78a814ca628ca54358cc35808b8bd032bcde81f72134addc05e5546285e |
BITCOIN WALLET EXPLORATION
There are about 52 Bitcoin Wallet Addresses found in the Chat Log. This section lists what each address received. An address named in the chat can belong to an exchange or a third party, so these totals are not the group's income.
Following is the chart of Bitcoin Wallets along with Balance received.
BITCOIN : AMOUNT
================
15HP3kzUGTFQQuDfSqz85gvLz2h6si2evY : $9,821.96
15VLtQrCrdUjDBif9j3yo7UuAiXyfykfUu : $346.22
18TUsETA3Uk3GBJ9geRrVzvssAd8rCP2AK : $283.04
1DPxRgDgP2aT9PqqSGYtQseHZVCQZQdzQv : $26,050.42
1JAVjvoq5c6dGH6eeLTnx4DQYPf5omtGaN : $44,991.36
bc1q07rjleva5yturfc46qp762fxj05nt07nayyvte : $3,270.60
bc1q08u70d39fsf8du673m4jphjmf75rv7au9avtz7 : 0
bc1q0xj6w9y04teeh6ldc8zteyjqglr67d90j9ha6w : $7,597.31
bc1q2nnjmgtzemrxpuxecqsqz2s7nyef8wyy86l3n8 : $7,263.08
bc1q3zwrmdp8g5m9swgrq45zz69w9ngu8uyw2rhrn0 : $393,282
bc1q48judrx0k82cwdtw3wm2glslf0s9e3wq90qag7 : $372,325
bc1q5lfuz8fmetfpcckxf6kmms4kp6xzraazy4gguy : $981.87
bc1q6pmrt4j8r5qaaq9vgzxffwhnwdrppxvcsewexr : $67,975.75
bc1q6q9ww5ddr7gculnmmqkvg8944f6ecmzqd4m0kd : $107,935
bc1q76lwvgcmuhtqk0cvm7k3zhrs7uqe74c4q6tfyv : $754.82
bc1q7cz8wgp23kkx5wc3f4zpevylsdq8u2lw0augf8 : $5,146.64
bc1q8tnmj2wtthsva0fnzyvl6vdv6kcsud354tkwlr : $24.61
bc1q9w97kz9vfrymj5ju75luyy2l76fne9zffylqss : $710.86
bc1qarmsjcr3tf0kqn2e0f3p37ypcr2ttcsq469ce8 : $5,235.01
bc1qctpx4fr4ump33tpzankrm3nuuptepcywnsvyef : $391,186
bc1qej6ecmdvyl2c9rk8r7h25taq6amlktqs246m3q : $2,172.53
bc1qfl857h8wwv9yauynektfh8eahs3vj7x9h4xc0s : $60,813.38
bc1qg0wfhtzsq7paw43wt4gjc826xu3zl744kqzka4 : 0
bc1qgavls503x7l09g46ltcag2k94cu8z04mgwf63l : $1,576.34
bc1qgyvjlkm7dg2he5rl0ce7gxngznuaewh860lghu : $107,526
bc1qk6swlp3yarz8ghg4r093zuhtxxaw9gd5h8x20x : $83,878.43
bc1ql82gf9fc9czqnmhmsfx7ntel9fh588qc2qnakg : $39,301.29
bc1qmwdcm977wx8sjnam9f7a3kwgtnhm8w84vneqjv : $12,227.96
bc1qn0flulmgm29egv8s0r8se08w32auanykyeu7tq : 0
bc1qpns7fuy6eaukumxtpd3t03uws68kk0z3ua4wps : $220,841
bc1qqeyte53f58dnxly5yemwfny90sxxe8ksrflcrn : $2,181.88
bc1qqgsp70raz2xt72clpwry7hjdfcalysextu0vm7 : $301,702
bc1qrcpkt3xf44ve2uadzcgvduwq9jxuceaep97m6l : $312.94
bc1qrqt2n7tnx3znrnf0s9ctarxnp4j6l6z0cexsn9 : $536,741
bc1qsgehsucpxvmnynake7jzdw2ayzkatcymts0x3s : $1,303.67
bc1qsp8qr7djr5kjel8ec9z5p3kelpxxfkjd8sh9kp : $8,154.72
bc1qtahjyeej6z7k2vhad34g82e385gq49u3dsc848 : $5,294.31
bc1qtpzq4x07wtgnlkrrj7f6lzjjxll7qeep2726ag : $7,296.89
bc1qty6fppk4k475k64qahredmy0lrhwv00geqjnea : $112,644
bc1qugpv9y2tejmf9583qk62a0plrdcqjp95kqrqsh : $3,703.36
bc1qujhakjsm8sn78rt32d8c3dm20u5h7xjmx3ft6p : 0
bc1qurppf5r2wtzxjjr0t6n2s2n299d3rgq3rl36rp : $6,966.75
bc1quveda27fvff7gc23jjxzldnxma35pggw9da0dc : $310.64
bc1qv8t80zrsllygwnemychn66w07zzsv9hc55ygsx : $6,607.08
bc1qv94tw4mpcpp8nhy6wceyazkwa5lsaa2ujzddch : 0
bc1qxtauswsz937ydc0smrj4lsjsnuhkzthc60ah7y : $296.89
bc1qxzw8x5t5ddzenyulyprelzqmz5tuqg53atv7p0 : $772.96
bc1qzjunthnuy7ex80fwszmnpul65ux6vlc3gg38wc : 0
bc1qzpqmrxprw9e6zera0mw9h0tkuyc8vzga455meh : $1,359.46
bc1p6avy9xum2uu9rnn7nf9gdp0pynxaw0wlhygvexfnqp53e93pq4rqyf8q5l : 0
As we have seen, there are only 7 wallets which haven’t received any amount (netted 0).
In the collection, we can see there are only 2 Legacy Bitcoin Addresses and 1 Bitcoin Taproot Address (which is 62-char long). Rest of the wallets are SegWit Addresses used.
The biggest amount received is $536,741 to the Wallet: bc1qrqt2n7tnx3znrnf0s9ctarxnp4j6l6z0cexsn9.
Since nearly every address received funds, the focus here is the 12 highest-balance wallets:
bc1q3zwrmdp8g5m9swgrq45zz69w9ngu8uyw2rhrn0 : $393,282
bc1q48judrx0k82cwdtw3wm2glslf0s9e3wq90qag7 : $372,325
bc1q6pmrt4j8r5qaaq9vgzxffwhnwdrppxvcsewexr : $67,975.75
bc1q6q9ww5ddr7gculnmmqkvg8944f6ecmzqd4m0kd : $107,935
bc1qctpx4fr4ump33tpzankrm3nuuptepcywnsvyef : $391,186
bc1qfl857h8wwv9yauynektfh8eahs3vj7x9h4xc0s : $60,813.38
bc1qgyvjlkm7dg2he5rl0ce7gxngznuaewh860lghu : $107,526
bc1qk6swlp3yarz8ghg4r093zuhtxxaw9gd5h8x20x : $83,878.43
bc1qpns7fuy6eaukumxtpd3t03uws68kk0z3ua4wps : $220,841
bc1qqgsp70raz2xt72clpwry7hjdfcalysextu0vm7 : $301,702
bc1qrqt2n7tnx3znrnf0s9ctarxnp4j6l6z0cexsn9 : $536,741
bc1qty6fppk4k475k64qahredmy0lrhwv00geqjnea : $112,644
IOC registry compiled from chat export analysis (5,692 messages) and on-chain blockchain verification (Blockstream API). Actor infrastructure IOCs are separated from victim contact data. 150+ harvested victim employee emails are omitted from this appendix but are preserved in the source data.
Facing a cyber security incident?
If you believe your organisation has been compromised by Silent Ransom Group or a related actor, please reach out to Ransom-ISAC.
Found this article helpful?
Share it with your network